vArmor is a free, open source ai security & privacy project written in Go and released under Apache-2.0. It has 512 GitHub stars, 71 forks and 3 open issues, and was last pushed 23 hours ago. On this registry it ranks #47 of 49 tracked projects in AI Security & Privacy, with 5 head-to-head comparisons available. It gained 7 stars over the last 30 tracked days.

What is vArmor?

vArmor is a cloud-native container hardening system that uses AppArmor LSM, BPF LSM, Seccomp, and an Envoy-based Network Proxy sidecar to enforce access control from system calls up to application protocols, built for Kubernetes operators and platform teams that need to sandbox workloads including AI agents and LLM-based applications.

What it is

vArmor is an open-source project written in Go and published under the Apache-2.0 licence by the bytedance/vArmor organisation. It follows the Kubernetes Operator design pattern, which means users harden specific workloads by manipulating a CRD API rather than by editing host-level configuration. The project abstracts AppArmor, BPF, Seccomp, and NetworkProxy as distinct enforcers that can be used individually or in combination, so a single policy object can govern file access, process execution, syscalls, and network egress at the same time.

The concrete problem it solves is the gap between what a stock container runtime gives you and what a hostile or hijacked workload can reach. By strengthening container isolation and reducing the kernel attack surface, vArmor raises the difficulty and cost of container escape, privilege escalation, and lateral movement inside a cluster. Where a team would otherwise hand-maintain per-workload AppArmor profiles, Seccomp filters, and BPF programs, vArmor makes those enforcement layers declarative and scoped to the business workload being protected. Its NetworkProxy enforcer extends egress control beyond what CNI NetworkPolicy offers, adding L7 inspection for HTTP and HTTPS, TLS SNI-based domain filtering, and header injection.

Key capabilities

  • CRD-driven policy: workloads are hardened through the Kubernetes CRD API, matching enforcement to business intent.
  • Four enforcers — AppArmor, BPF LSM, Seccomp, and NetworkProxy — usable alone or combined.
  • NetworkProxy sidecar powered by Envoy intercepts egress at L4 (TCP), L7 (HTTP/HTTPS), and TLS SNI level.
  • TLS MITM termination enables decrypted HTTPS inspection of outbound traffic.
  • Per-domain HTTP header injection, for example API key injection, plus anti-Domain-Fronting protection.
  • Allow-list and deny-list egress modes with audit logging and dynamic policy updates.
  • Documentation shipped in three languages: README.md, README.zh_CN.md, and README.ja.md.

Who uses it and how

  • Multi-tenant clusters where hardware-virtualised container solutions are ruled out by cost or technical constraints.
  • Teams running critical business containers that want privilege escalation, escape, and lateral movement to be harder for attackers.
  • Organisations facing high-risk vulnerabilities they cannot patch immediately, using vArmor to block or obstruct exploitation depending on vulnerability type and exploitation vector.
  • Deployments of AI agents or LLM-based applications that need precise control over outbound network access to stop data exfiltration, unauthorised API calls, or abuse induced by prompt injection.
  • Platform teams that need L7 egress policy with audit logging in addition to standard CNI NetworkPolicy.

Getting started

vArmor is deployed as a Kubernetes Operator into a cluster, after which vArmor CRD objects are applied to target workloads; release artefacts are published on the project's GitHub releases page and documentation lives at https://varmor.org.

How it compares

The project positions itself against CNI NetworkPolicy, which it complements rather than replaces: NetworkPolicy cannot perform L7 access control for HTTP and HTTPS, TLS SNI domain filtering, per-domain header injection, anti-Domain-Fronting protection, or equivalent audit logging. Against hardware-virtualisation alternatives such as Kata Containers, vArmor is explicit that runc plus vArmor does not reach the same isolation level, and it recommends hardware-virtualised containers for compute isolation when a high-intensity boundary is required.

When to use it — and when not to

A self-hoster must operate a Kubernetes cluster with nodes supporting AppArmor and BPF LSM, run the vArmor Operator and its CRDs, and carry the Envoy-based sidecar and its audit logging as part of the egress path. Teams that genuinely need hardware-virtualisation-grade isolation should not pick it, since the project states plainly that runc plus vArmor is not equivalent to Kata Containers. Note also that the repository shows both Apache-2.0 and GPL licence badges, and the supplied README text trails off mid-sentence in the feature list, so anyone evaluating it should confirm the licence terms and read the full upstream documentation before adopting.

project readme (upstream, from github) — read inline

BHArsenalUSA2024 Go Report Card License License Latest release

English | 简体中文 | 日本語

vArmor is a cloud-native container hardening system. It leverages Linux's AppArmor LSM, BPF LSM, Seccomp, and Network Proxy (Envoy-based sidecar) technologies to implement enforcers. It can be used to strengthen container isolation, reduce the kernel attack surface, enforce network egress access control at L4/L7 levels — including TLS MITM for decrypted HTTPS inspection, HTTP header injection, and anti-Domain-Fronting protection — and increase the difficulty and cost of container escape or lateral movement attacks. You can leverage vArmor in the following scenarios to provide sandbox protection for containers within a Kubernetes cluster.

  • In multi-tenant environments, hardware-virtualized container solutions cannot be employed due to factors such as cost and technical conditions.
  • You want to enhance the security of critical business containers, making it more difficult for attackers to escalate privileges, escape, or laterally move.
  • When high-risk vulnerabilities are present but immediate remediation is not possible due to the difficulty or lengthy process of patching, vArmor can be used to mitigate the risks (depending on the vulnerability type or exploitation vector) to block or increase the difficulty of exploitation.
  • You are deploying AI Agents or LLM-based applications and need to precisely control their outbound network access — preventing data exfiltration, unauthorized API calls, or abuse induced by prompt injection attacks.

Note:
- The core of security defense lies in balancing risks and benefits, transforming uncontrollable risks into controllable costs by choosing different types of security boundaries and defense technologies.

- runc + vArmor does not provide an isolation level equivalent to that of hardware virtualization containers (such as Kata Containers and other lightweight virtual machines). If you require a high-intensity isolation solution, please consider using hardware virtualization containers for compute isolation, and utilize CNI's NetworkPolicy for network isolation.

- vArmor's NetworkProxy enforcer further complements NetworkPolicy by providing L7 access control for both HTTP and HTTPS (via TLS MITM), TLS SNI-based domain filtering, per-domain HTTP header injection, anti-Domain-Fronting protection, and comprehensive audit logging — capabilities that NetworkPolicy does not offer.

vArmor Features:

  • Cloud-Native. vArmor follows the Kubernetes Operator design pattern, allowing users to harden specific workloads by manipulating the CRD API. This approach enables sandboxing of containerized microservices from a perspective closely aligned with business needs.
  • Multiple Enforcers. vArmor abstracts AppArmor, BPF, Seccomp, and NetworkProxy as enforcers, supporting their use individually or in combination. This enables enforcing access control on container file access, process execution, network outbound (L3–L7), syscalls, and more.
  • Network Proxy Enforcer. vArmor introduces a sidecar-proxy-based enforcer (powered by Envoy) that transparently intercepts and controls container network egress traffic at L4 (TCP), L7 (HTTP/HTTPS), and TLS SNI levels. It supports TLS MITM termination, per-domain HTTP header injection (e.g., API key injection), anti-Domain-Fronting protection, allow-list and deny-list modes, audit logging, and dynamic policy updates without Pod restarts.
  • AI Agent Protection. vArmor provides defense-in-depth for AI Agent workloads by combining kernel-level mandatory access control (AppArmor/BPF/Seccomp) with application-protocol-level network access control (NetworkProxy), effectively mitigating risks such as prompt injection-induced tool abuse, key leakage, and unauthorized data exfiltration.
  • Allow-by-Default. vArmor currently focuses on supporting this model, where only explicitly declared behaviors will be blocked, which effectively minimizes performance impact and enhances usability. Besides, it supports auditing violations, and these violations can also be allowed rather than blocked.
  • Built-in Rules. vArmor features a range of built-in rules ready to use out of the box. They are designed for the Allow-by-Default security model, eliminating the need for expertise in security profile creation.
  • Behavior Modeling. vArmor features a range of built-in rules ready to use out of the box. They are designed for the Allow-by-Default security model, eliminating the need for expertise in security profile creation.
  • Deny-by-Default. vArmor is capable of using allowlist profiles to harden workloads and provide a more user-friendly approach to develop and manage profiles.

vArmor was created by the Elkeid Team of the endpoint security department at ByteDance. And the project is still in active development.

Architecture
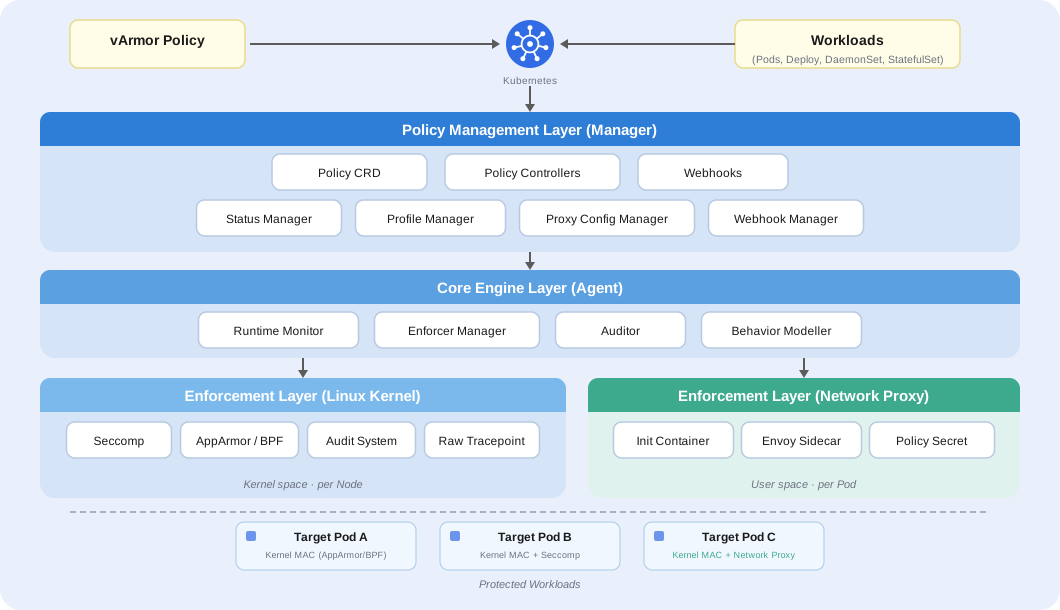
Documentation

vArmor reference documents are available at varmor.org.

⏩ Quick Start

⚙️ Installation

📔 Usage Instructions

📜 Policies and Rules

⏱️ Performance Specifications

Contributing

Thanks for your interest in contributing to vArmor! Here are some steps to help get you started:

🤝🏻 Read and agree to the code of conduct.

🛠️ Read the development guide.

💬 Join vArmor Lark group.

License

The vArmor project is licensed under Apache 2.0, except for third party components which are subject to different license terms. Please refer to the code header information in the code files.

Your integration of vArmor into your own projects should require compliance with the Apache 2.0 License, as well as the other licenses applicable to the third party components included within vArmor.

The eBPF code is located at vArmor-ebpf and licensed under GPL-2.0.

Credits

vArmor use cilium/ebpf to manage and interact with the eBPF program.

vArmor references part of the code of kyverno developed by Nirmata.

Demo

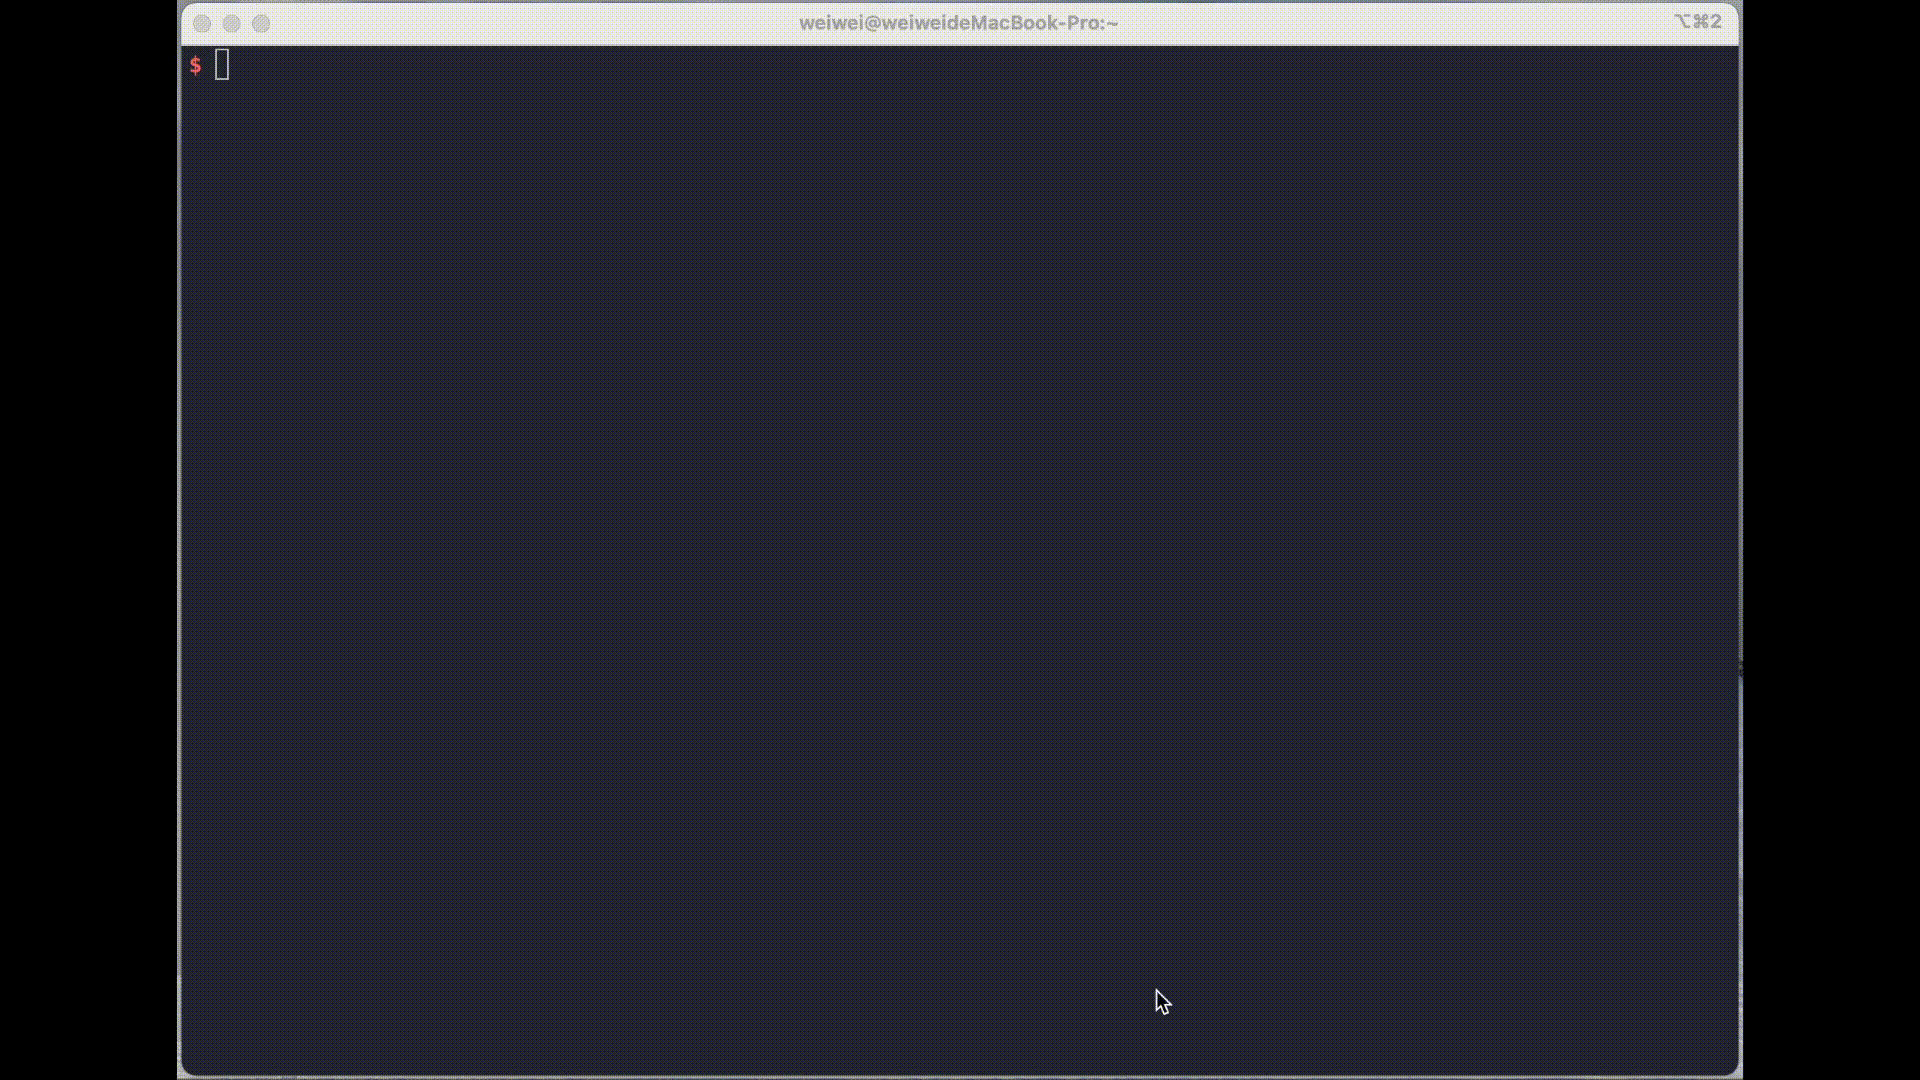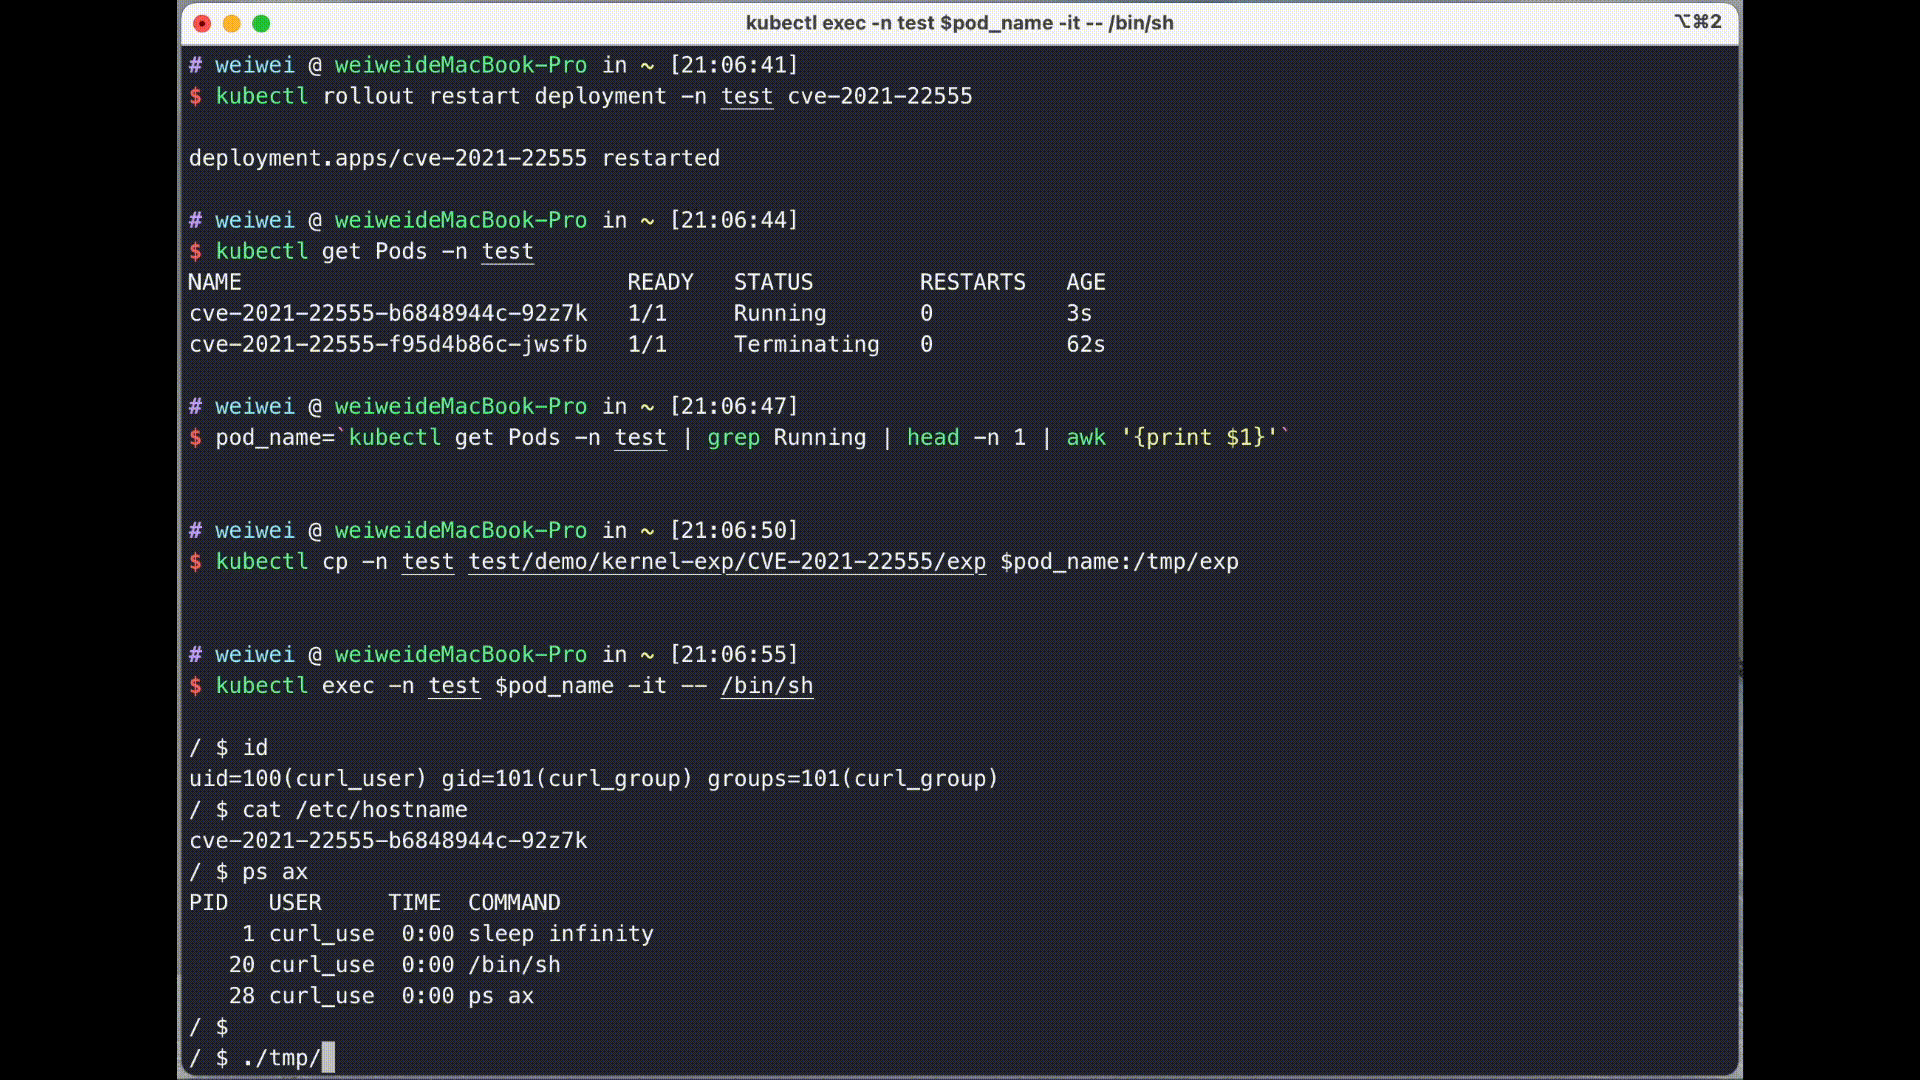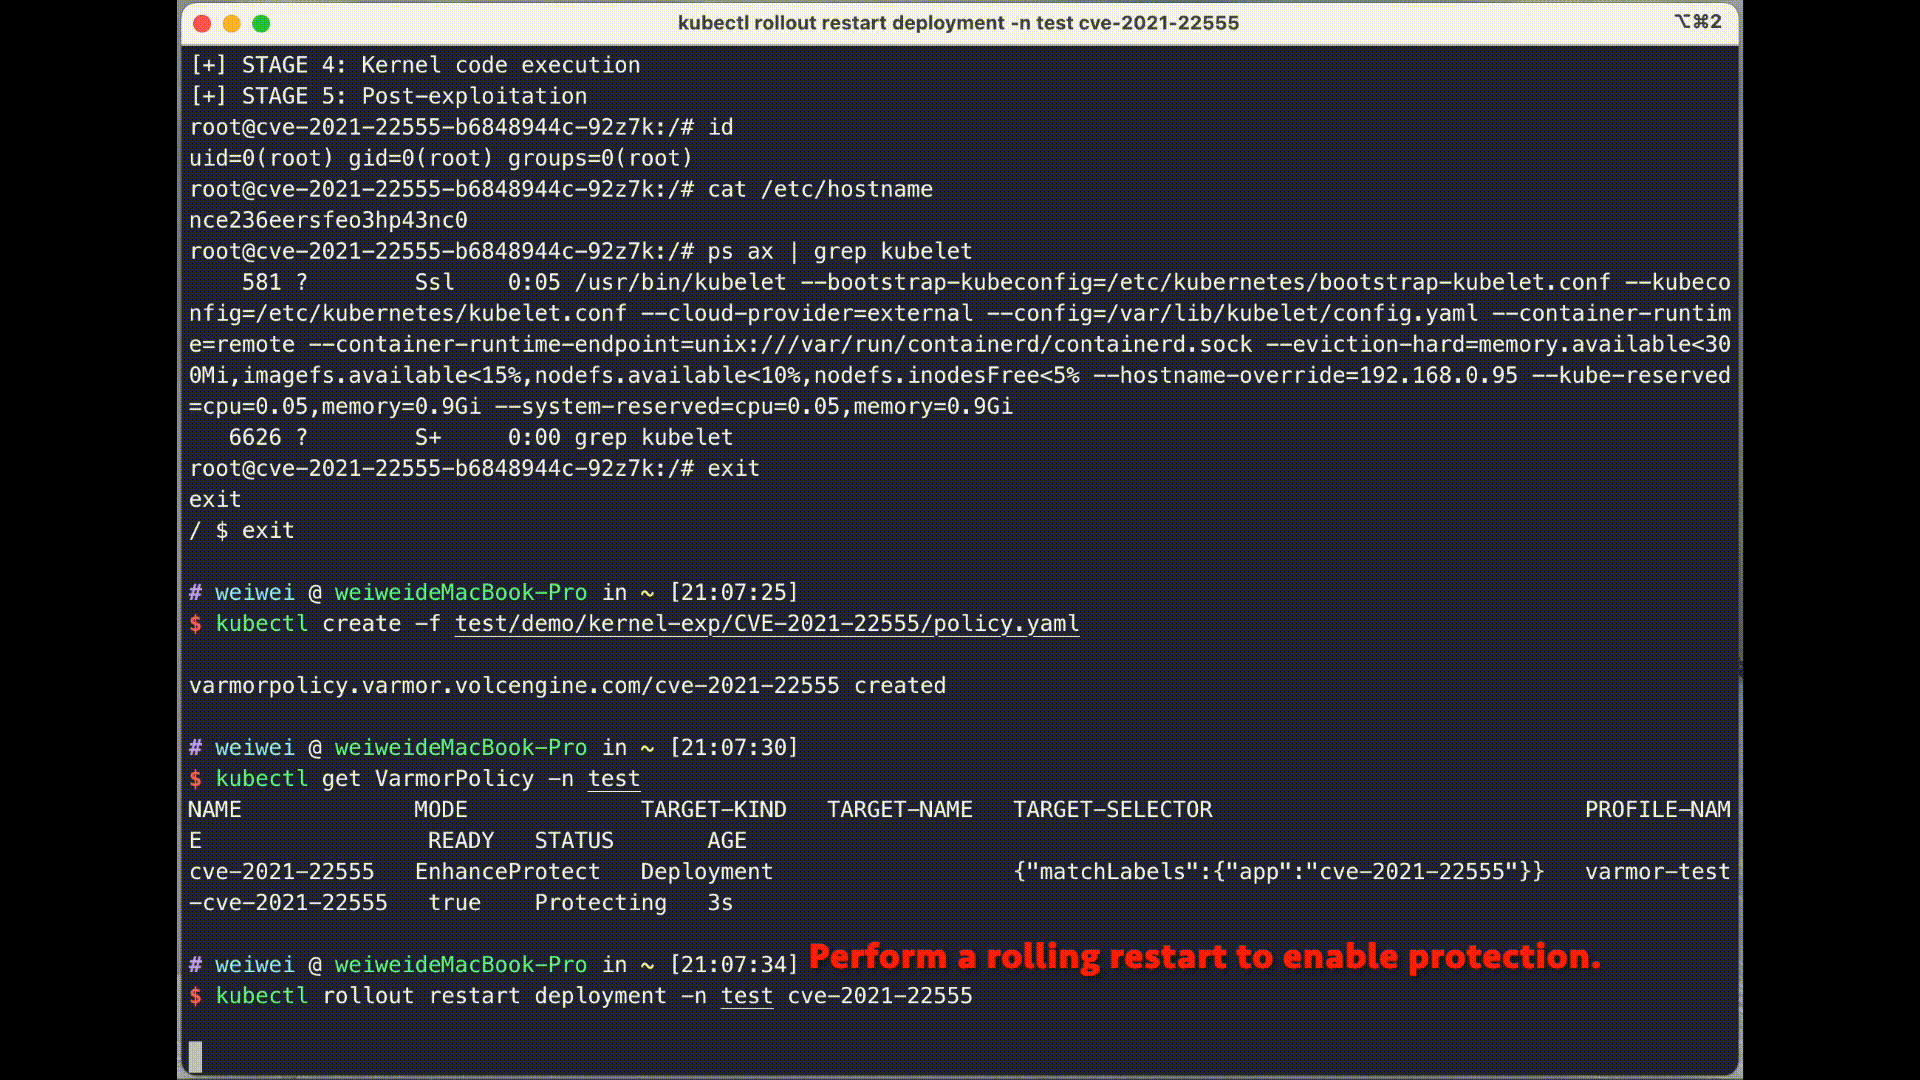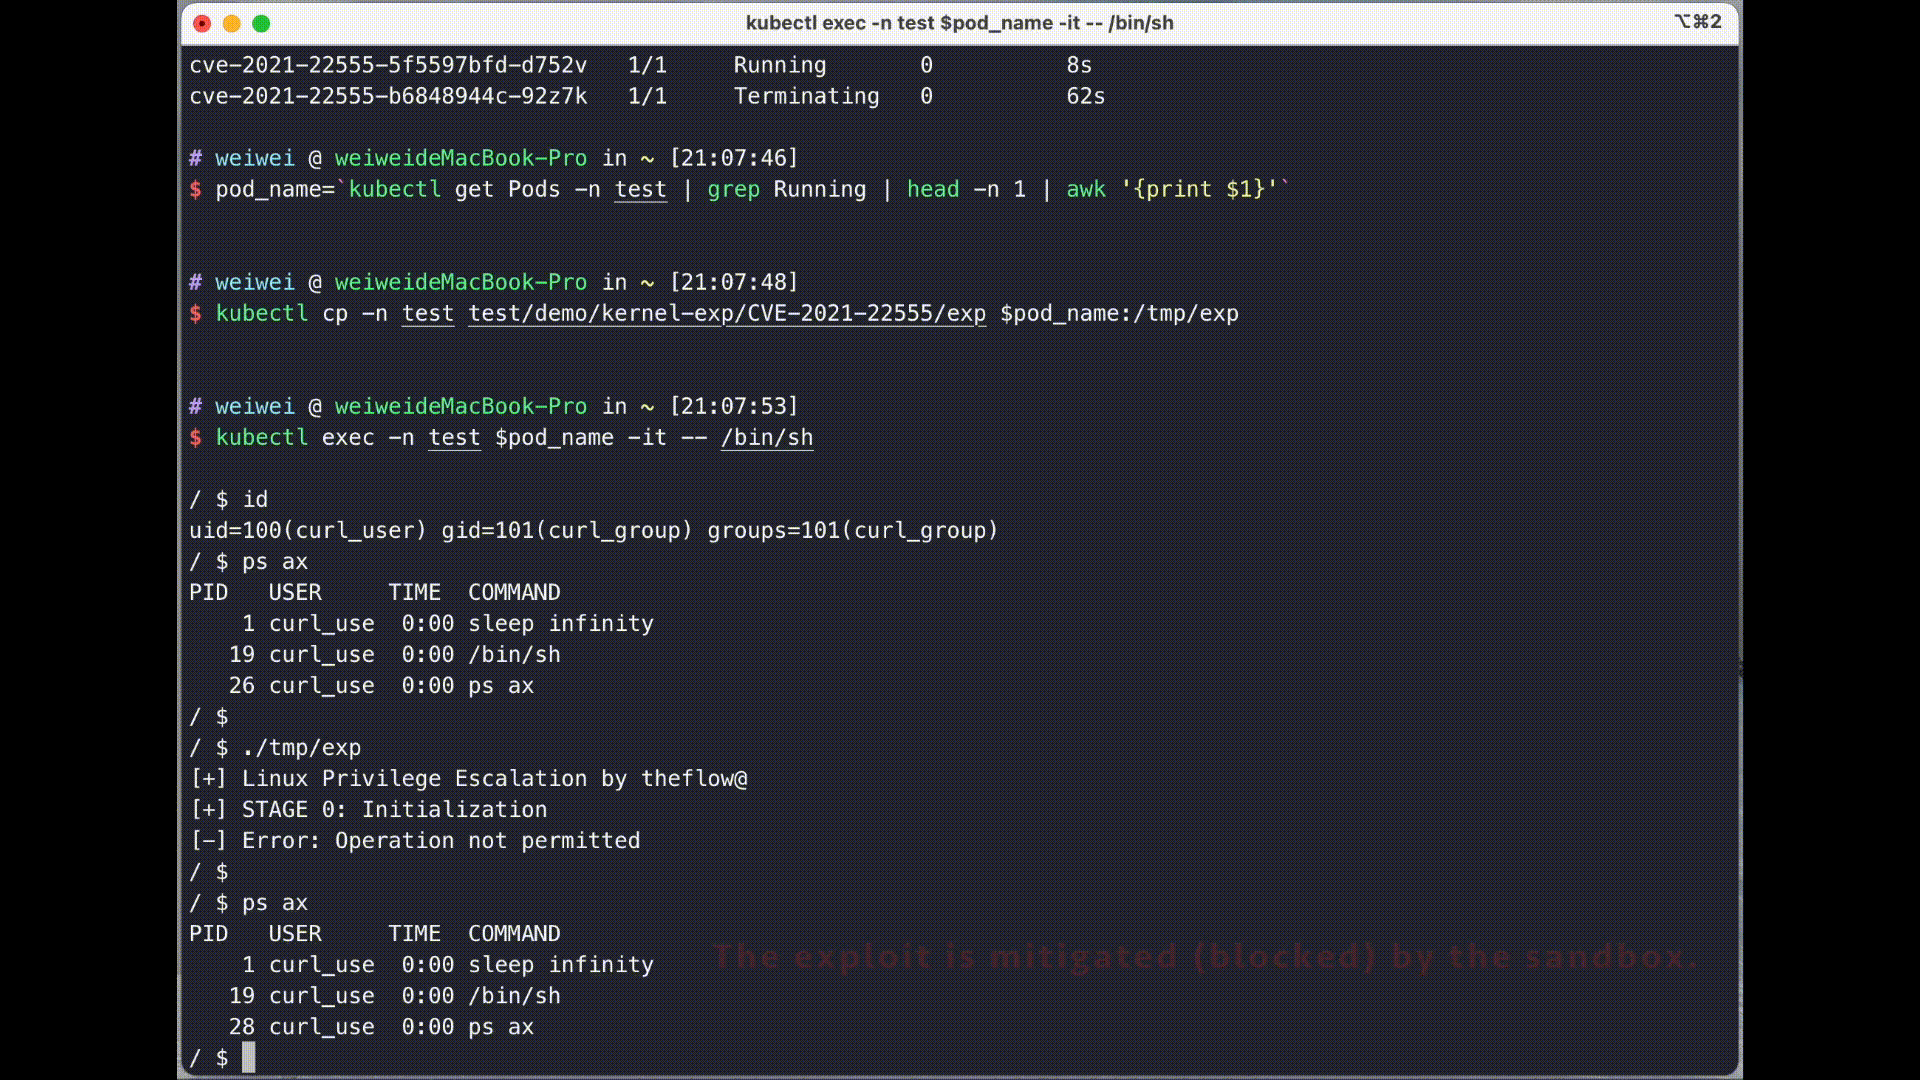
Below is a demonstration of using vArmor to harden a Deployment and defend against CVE-2021-22555. (The exploit is modified from cve-2021-22555)
image

404Starlink

vArmor has joined 404Starlink

Frequently asked questions

Is vArmor free to use?

vArmor is open source under the Apache-2.0 licence. There is no licence fee and no seat count — you can self-host it or, where the project offers one, pay a vendor for a managed version instead.

What does vArmor do?

vArmor is a cloud-native container hardening system that leverages AppArmor/BPF/Seccomp and NetworkProxy technologies to enforce access control from system call

What is vArmor written in?

vArmor is primarily written in Go. Its source is publicly available at https://github.com/bytedance/vArmor, and it has 512 GitHub stars.