What it is
PwnDoc is a JavaScript pentest reporting application released under the MIT license. It lives in the information security and penetration testing ecosystem, and it is positioned as a tool for audit work, vulnerability reporting, and compliance or risk management workflows. The project describes itself as a pentest report generator, with the stated aim of helping users spend more time testing and less time documenting by sharing data such as vulnerabilities among users.
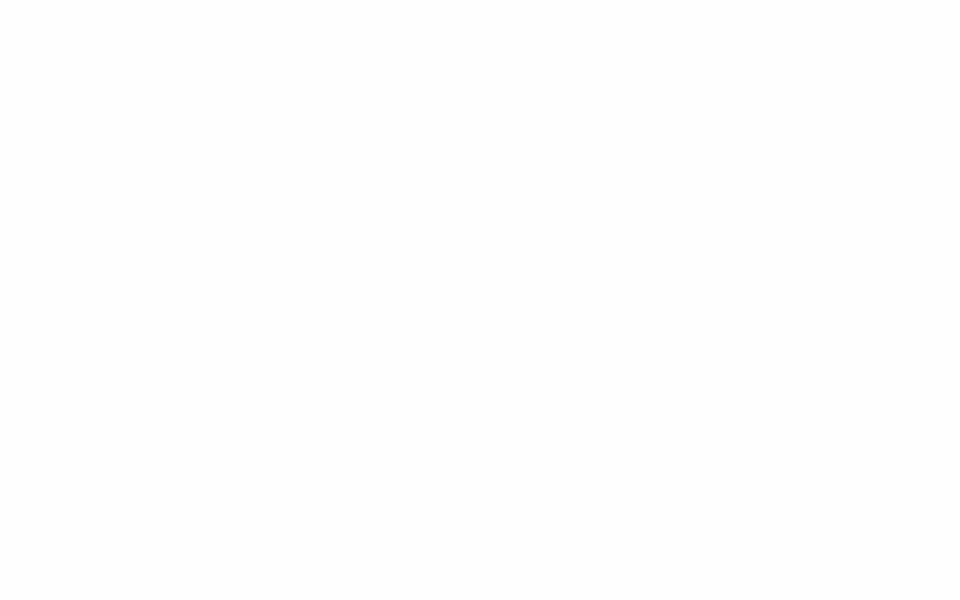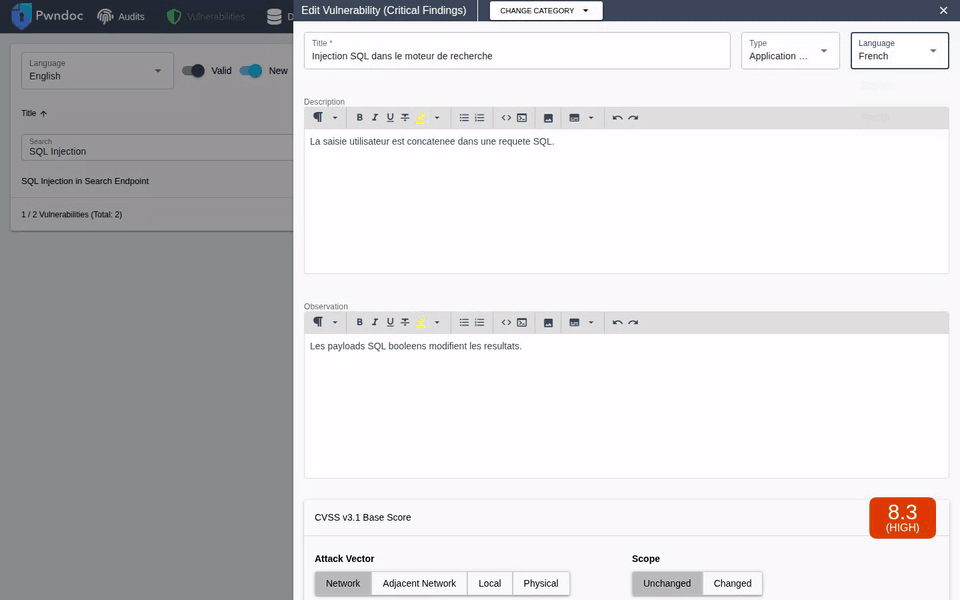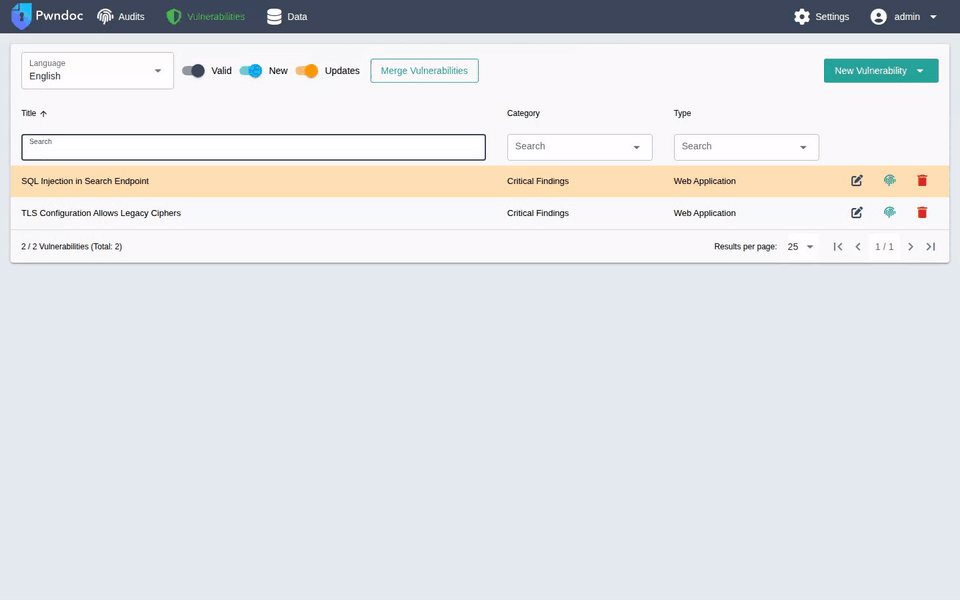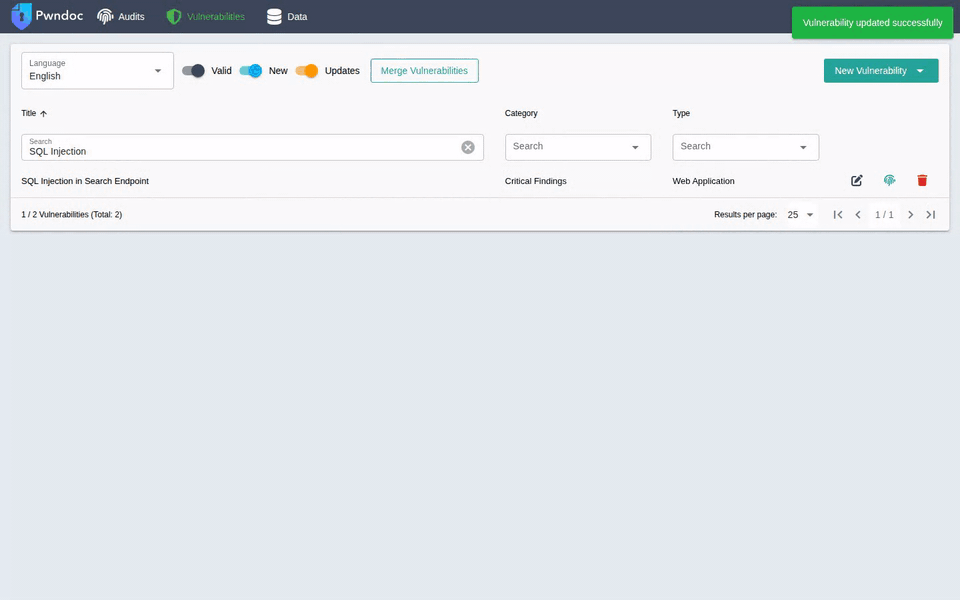
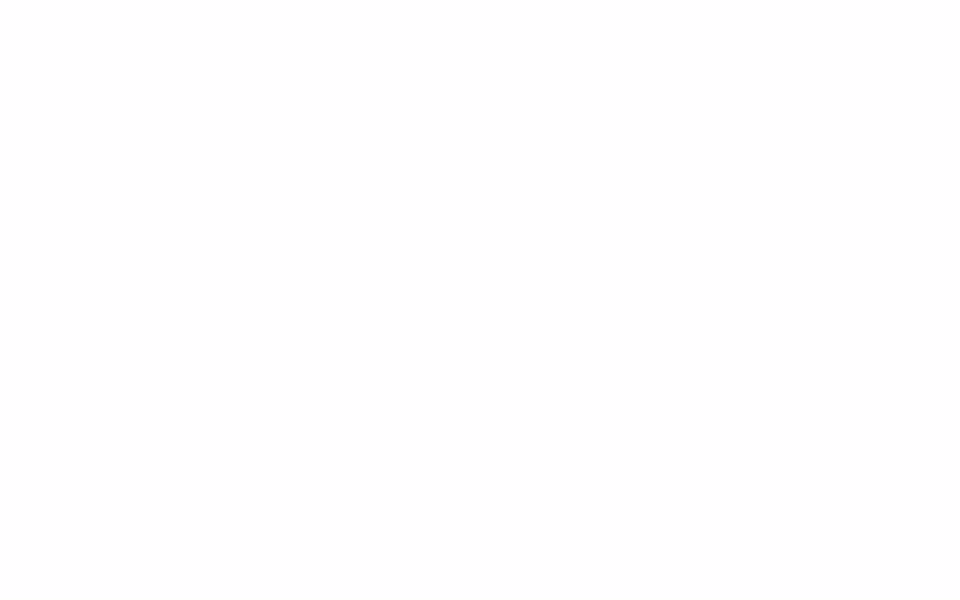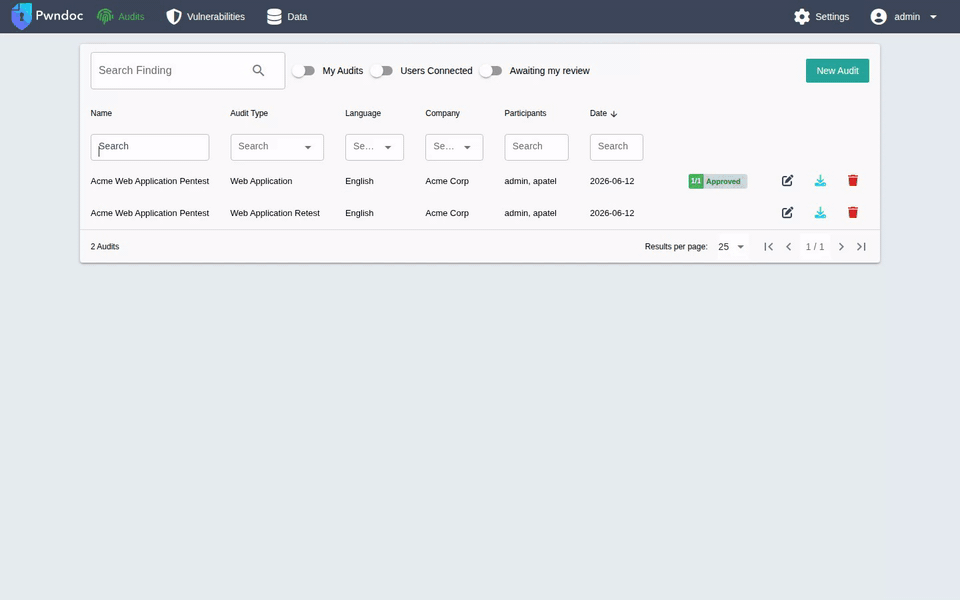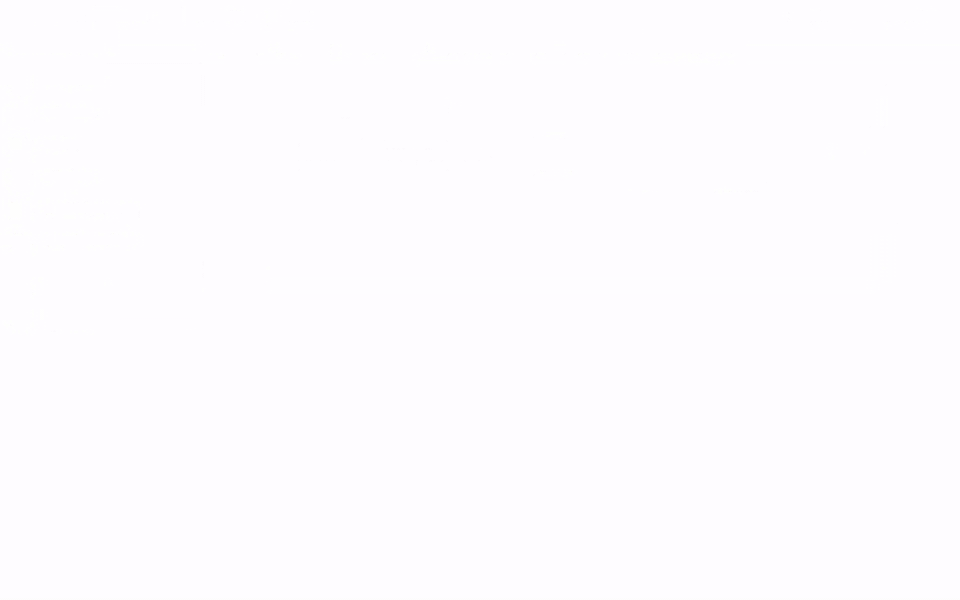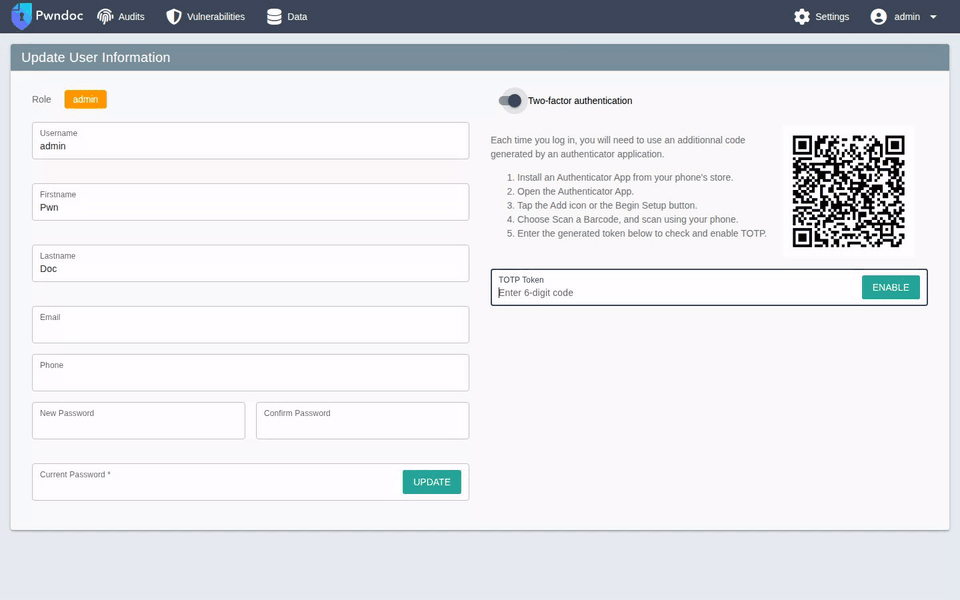
The concrete problem it solves is the repetitive and fragmented nature of penetration testing reports. Instead of each tester rewriting findings from scratch, PwnDoc provides reusable audit and vulnerability data, customizable report templates, and structured review workflows. It supports writing findings, organizing audits, managing vulnerability records, and producing customizable Docx reports from that shared data.
Key capabilities
- It generates Docx reports and supports Docx template customization, so report output can be shaped around an organization's preferred structure.
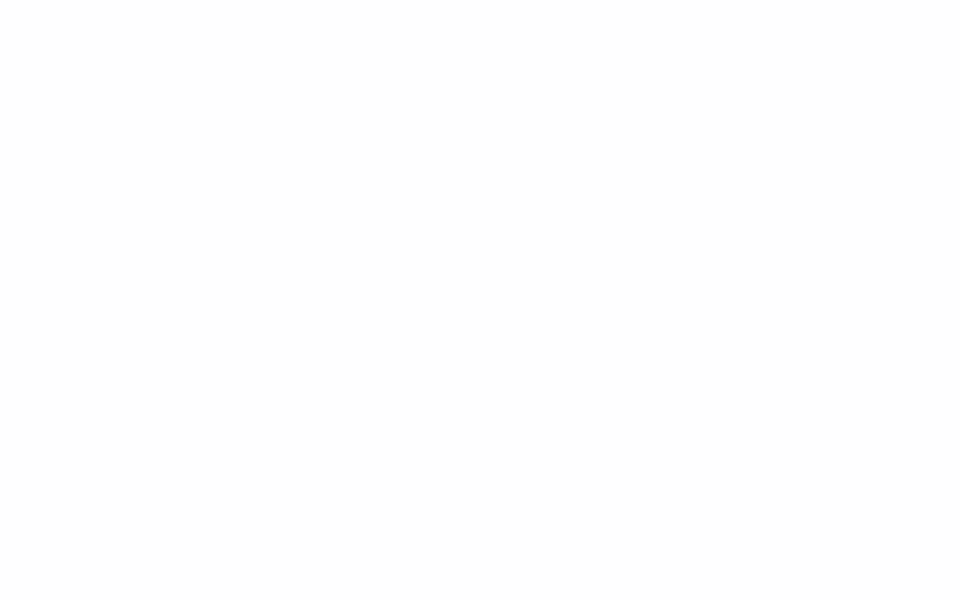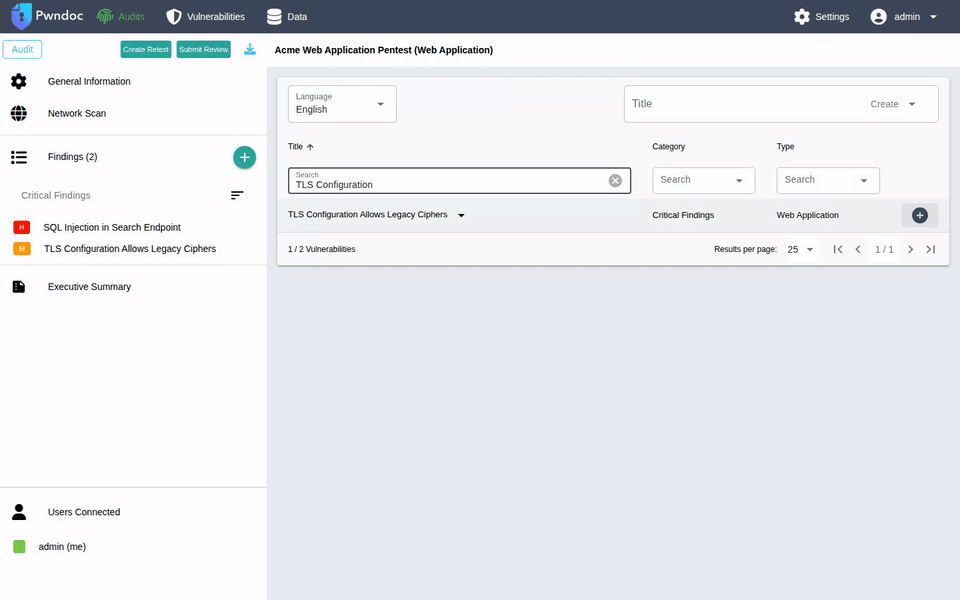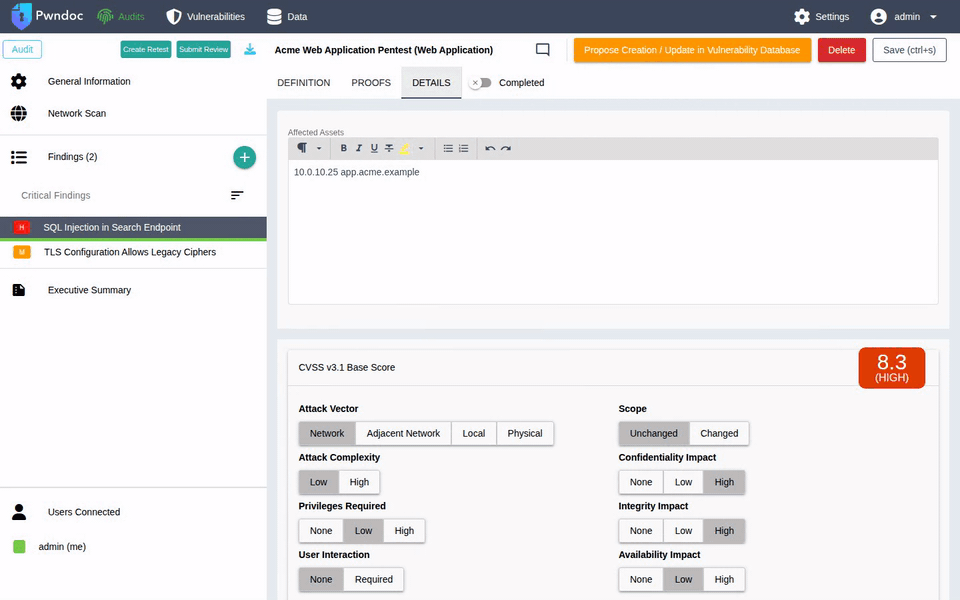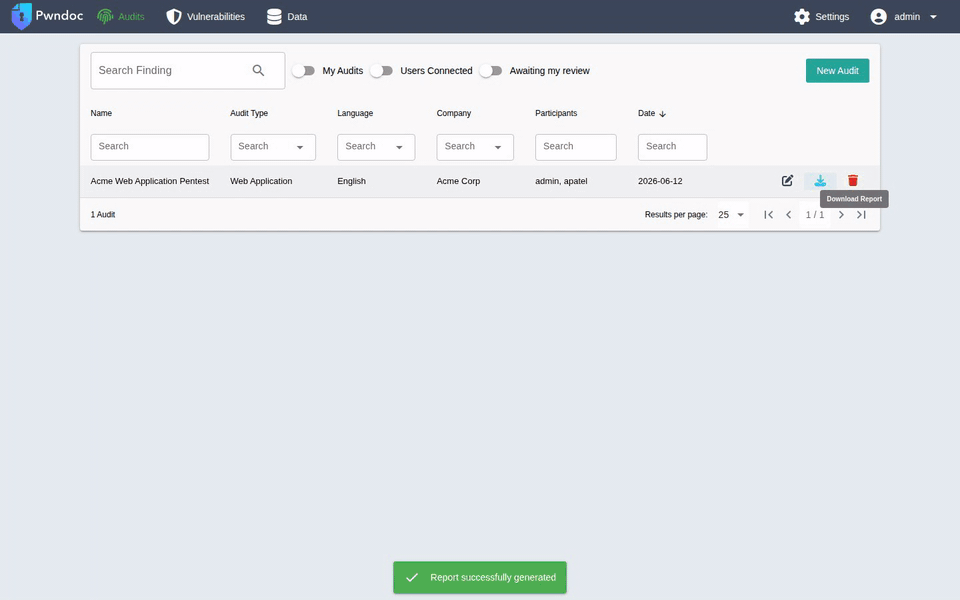
- It manages reusable audit and vulnerability data, including custom sections, custom fields for vulnerabilities, and vulnerability scoring with CVSS v3 and v4.
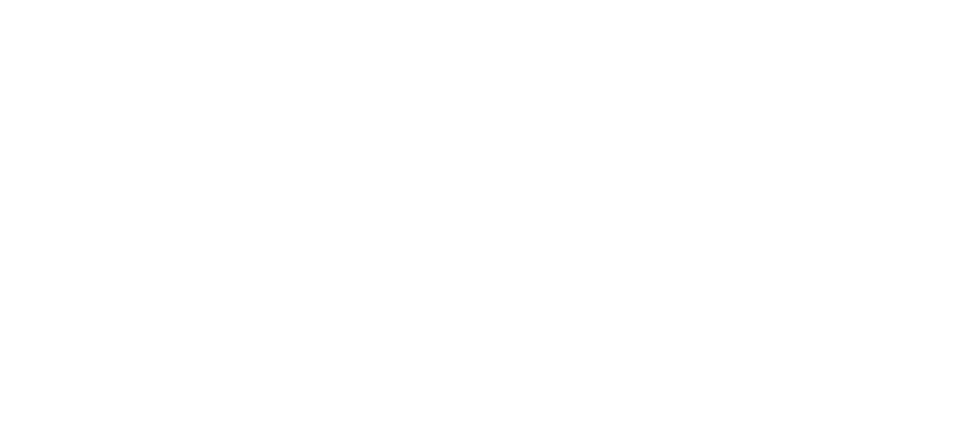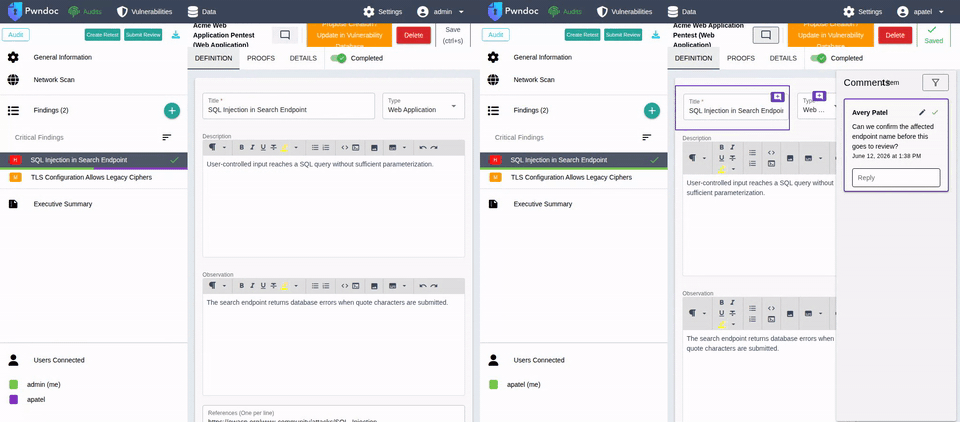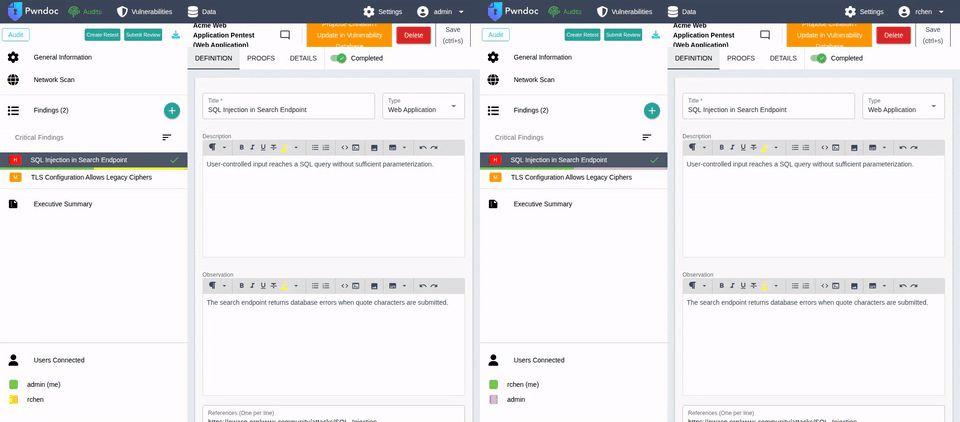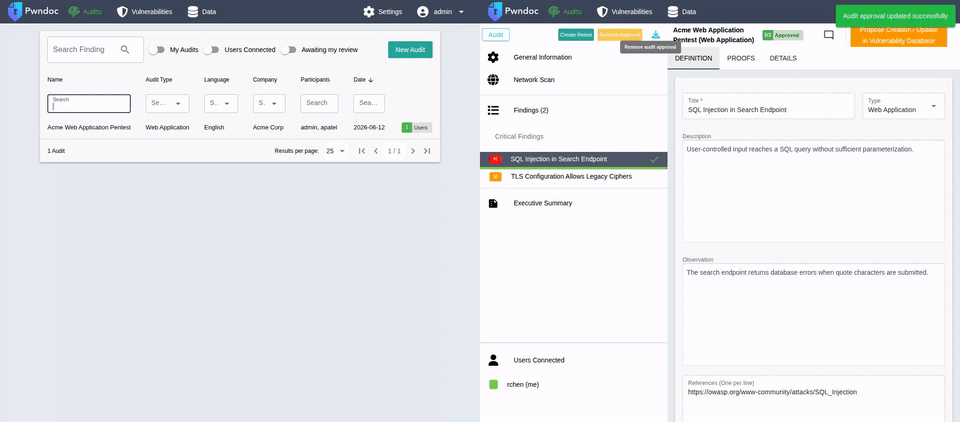
- It supports multi-user reporting with real-time collaboration, audit comments with threaded replies, and an audit review and approval workflow.
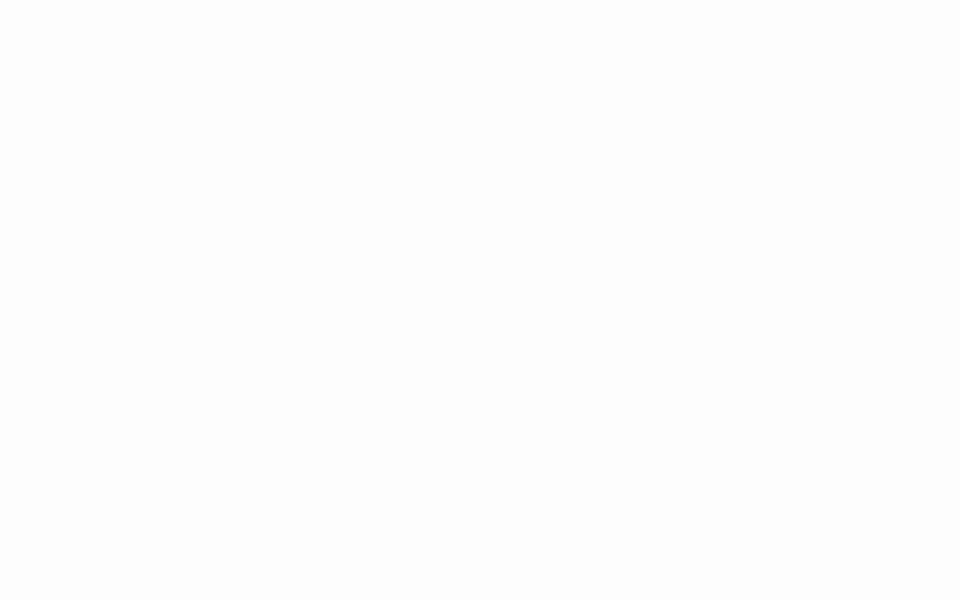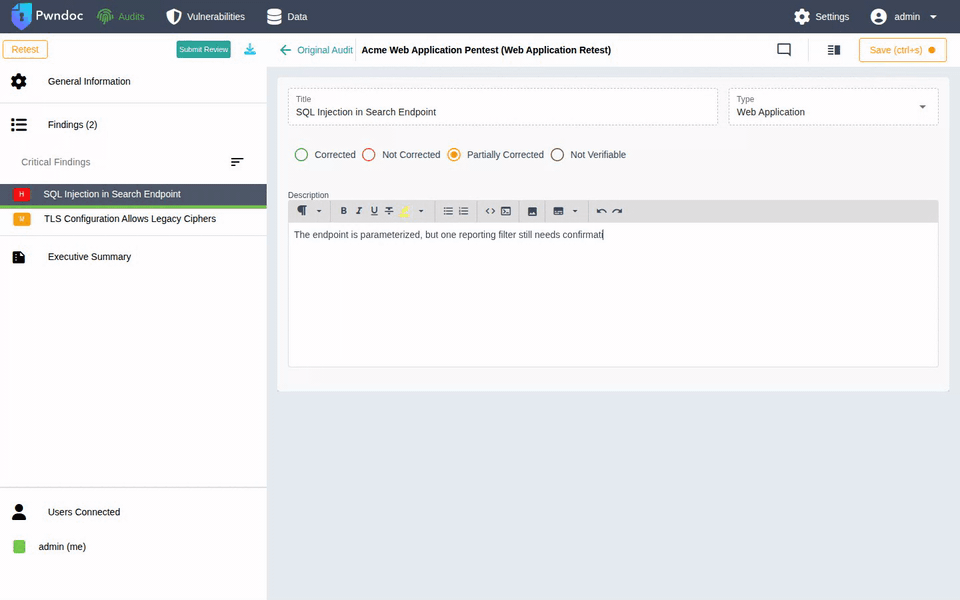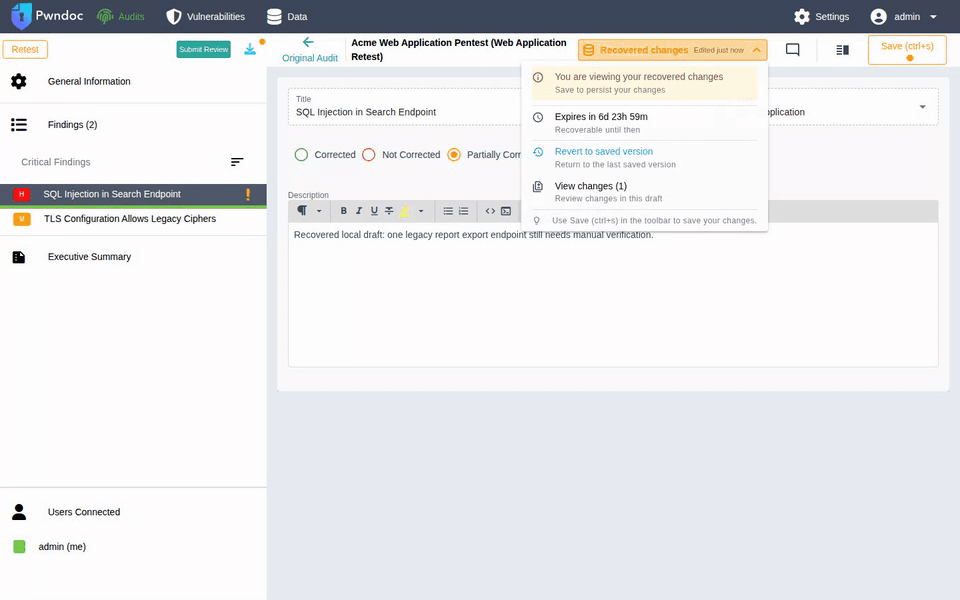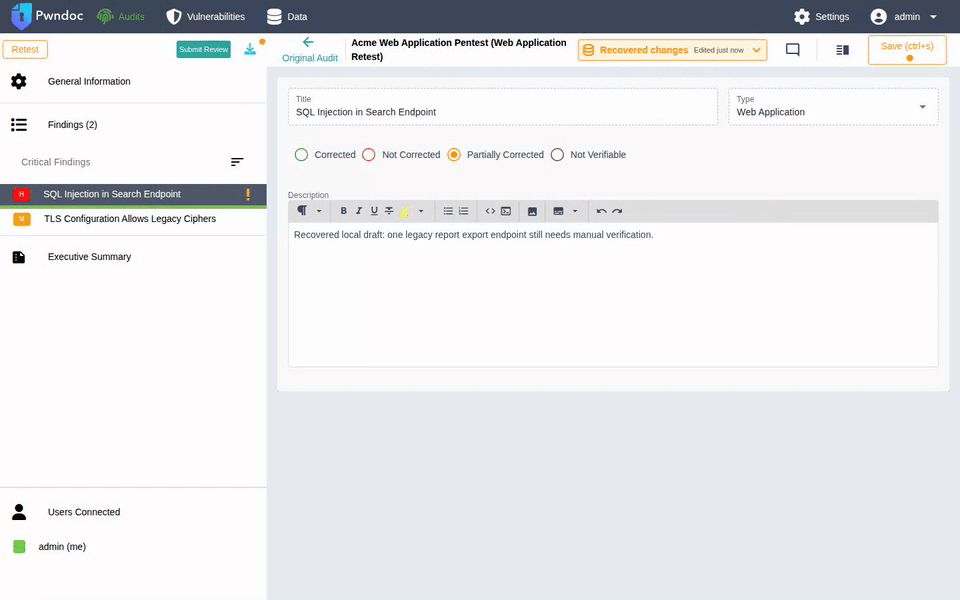
- It includes retest and multi-audit workflows, automatic recovery for unsaved work, and quality assurance review of audits and vulnerability templates using built-in and AI checks.
- It offers spellcheck and grammar checking through LanguageTool with custom rules, and AI-assisted writing with configurable prompts for OpenAI, Anthropic, DeepSeek, Ollama, and AWS Bedrock.
- It provides backup and restore with encryption and selective restore, two-factor authentication with TOTP, custom roles, and granular permissions.
Who uses it and how
- Penetration testing teams can use it to draft audit reports, store reusable vulnerability descriptions, and generate Docx deliverables from a shared data set.
- Security auditors can use the review and approval workflow, threaded comments, and role-based permissions to coordinate feedback before a report is finalized.
- Teams performing follow-up testing can use retest and multi-audit workflows to connect new findings with earlier audit records.
- Administrators can use backup, restore, authentication, roles, and settings to operate the application as a shared reporting platform.
Getting started
The README points to an Installation documentation page, but it does not list specific Docker image names, package managers, or a hosted option.
When to use it — and when not to
PwnDoc is useful when a security team wants an open-source reporting tool for pentest findings, shared vulnerability data, and customizable Docx output. It may be less suitable for users who need a fully managed hosted service, because the provided facts only describe installation documentation and no hosted option. Its feature set also depends on external services or components for some functions, such as LanguageTool for spellchecking and configured AI providers for assisted writing.