open·kritt
Orchestrate AI agents to find real vulnerabilities in code.
An open-source, self-hosted security and vulnerability research platform that turns focused AI analysis into de-duplicated, ranked findings with configurable validation and enrichment.


Website · Documentation · Getting started · Contributing · Owners · Research paper


What is open·kritt?
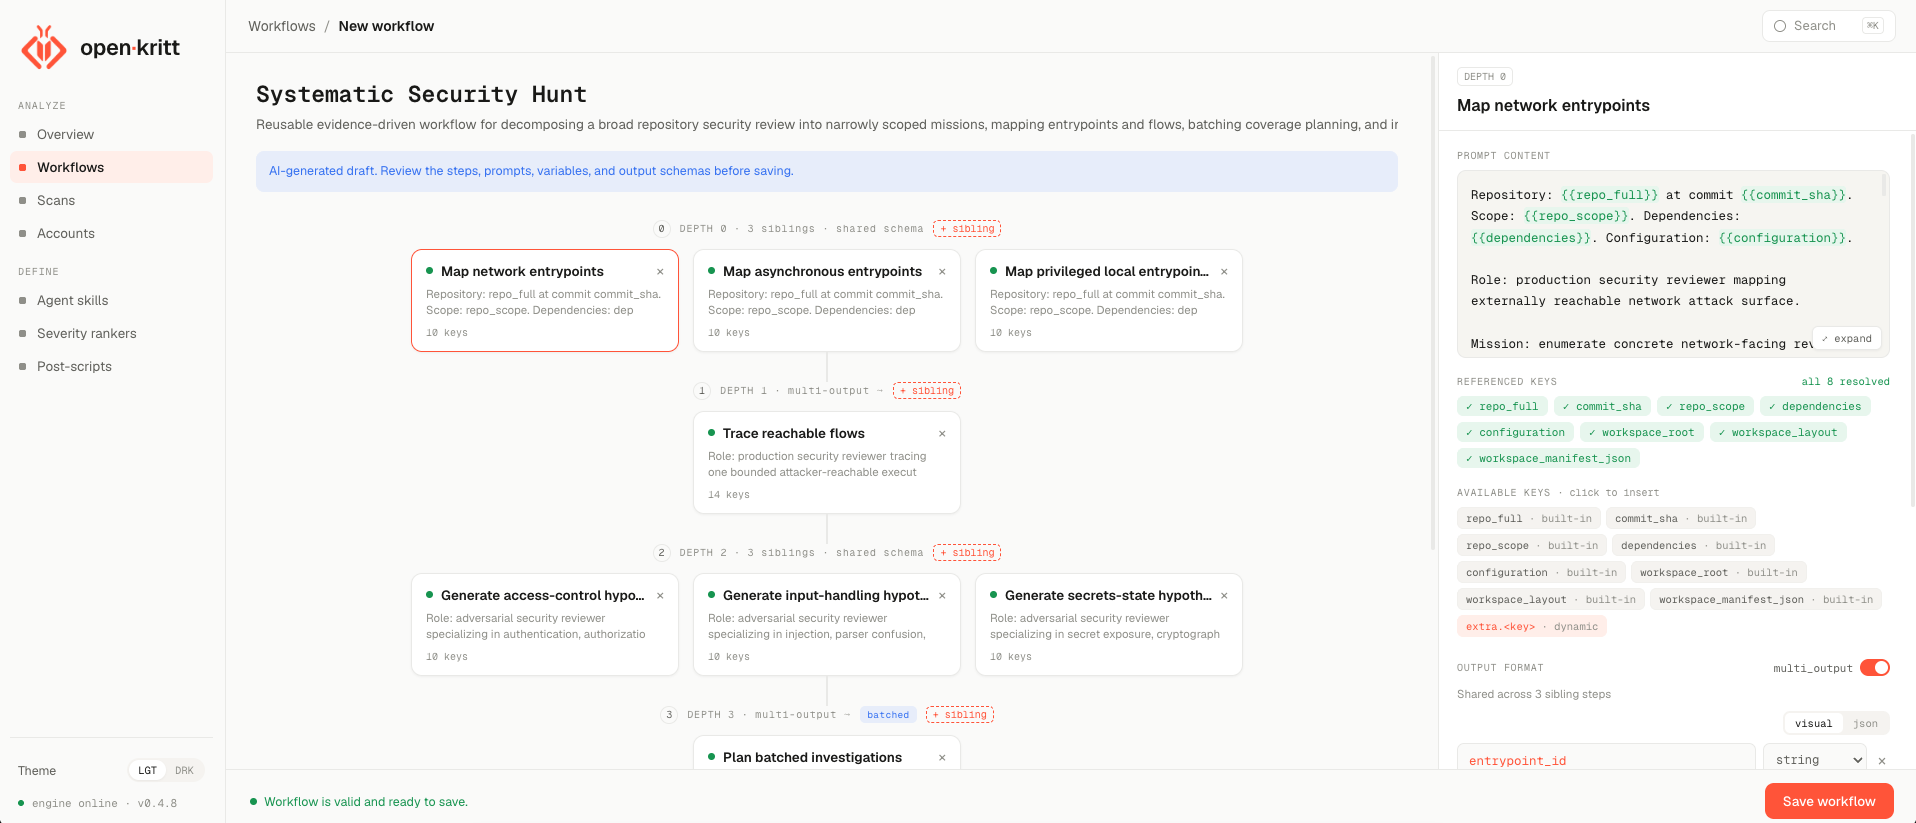
Pointing a model at an entire repository and asking it to find vulnerabilities rarely works well. open·kritt takes a focused approach: break the research into small, well-defined tasks, run them across AI agents in parallel, and combine their output into findings you can validate and prioritize.
It is built for security researchers and security-minded developers who want control over their prompts, workflows, model providers, and infrastructure.
What it does
- Build workflows — chain focused prompts into reusable security research playbooks.
- Run scans — analyze remote or local repositories and their dependencies with Codex or Claude Code.
- Verify findings — use post-scripts to validate issues, build proofs of concept, and produce reports.
- Export scan results — package canonical findings, structured data, post-processing output, reports, and proofs of concept in one ZIP archive with a share-safe manifest; completed scans produce complete exports, while stopped or failed scans with findings produce clearly marked partial exports. Attacker-influenced report and PoC source is kept as plain text.
- Prioritize results — apply custom severity rankers, a consistent finding schema, and automatic de-duplication.
- Bring your own model access — use a Codex login or connect through OpenAI, Anthropic, OpenRouter, or xAI.
Built from real security research. The Kritt team has earned over $1,500,000 in bug-bounty payouts under the researcher name Blockian (Immunefi · HackenProof · blockian.xyz · @Kritt_AI). open·kritt is the open-source distillation of the internal project behind that work.
Getting started
You need Git, Docker with Docker Compose, and Node.js 20 or newer. The repository-local CLI has no install step.
git clone https://github.com/Kritt-ai/open-kritt
cd open-kritt
./kritt setup
./kritt start
Open http://localhost:5173 once the stack is running. You only
need one model-access option; ./kritt setup guides you through the available logins and
API keys. A GITHUB_TOKEN is optional and only needed for private GitHub repositories.
On a server without a browser or desktop, leave the stack running and open another shell:
./kritt-headless
The headless CLI imports portable workflow, post-script, skill, and ranker JSON; creates scans with the same backend validation as the web form; displays scan status, stages, and failure reasons; edits non-secret runtime settings; and exports finding bundles. It does not display finding contents in the terminal. See the headless CLI guide.
The default ports bind to 127.0.0.1, and the backend does not include application
authentication. Keep the stack private.
Tool-enabled agents run as root inside disposable job containers, with writable repository copies and direct internet access so they can install tools, compile targets, run tests, and build proofs of concept. Run open·kritt on a dedicated Docker host or VM; see the threat model before scanning untrusted code.
For prerequisites, manual Docker setup, and provider-specific instructions, read the installation guide and AI provider setup.
In Accounts, use the persisted Active switch to choose which accounts may receive new assignments while keeping other credentials saved. See active provider accounts.
Documentation
Preview the documentation locally with Mint:
npm install -g mint
cd docs-site
npm run dev
Open http://localhost:3001 to view the site.
- Product overview
- Use open·kritt without a graphical interface
- Run your first scan
- Workflows and prompt steps
- Security and threat model
Community and contributing
open·kritt is jointly owned and maintained by
Harel Rom (@harel-coffee) and
Gabriel Balko (@GabiCtrlZ). See
project ownership and copyright for details.
Questions and ideas belong in GitHub Discussions. Use GitHub Issues for bugs and feature requests.
Contributions are welcome. Read CONTRIBUTING.md for the development setup, test commands, and Conventional Commit requirements.
Please report security vulnerabilities privately by following SECURITY.md, not through a public issue.
License
open·kritt is licensed under the GNU Affero General Public License v3.0.