Witness is an Apache-2.0 Go command-line framework from the CNCF in-toto ecosystem that creates and verifies signed attestations about how software artifacts were built, and it is aimed at platform, release, and security engineers who must prove artifact provenance across a software development lifecycle.
What it is
Witness is a pluggable framework for software supply chain risk management. It is a dynamic CLI tool that integrates into pipelines and infrastructure to create an audit trail for software's entire journey through the software development lifecycle, using the in-toto specification as its attestation format. Alongside attestation it carries its own policy engine with embedded support for OPA Rego, so the same tool both records what happened and checks that what happened was allowed. The project originated at TestifySec and was later donated to the CNCF in-toto ecosystem, where it is now maintained by the open community. It is written in Go and released under the Apache-2.0 licence.
The concrete problem it solves is provenance that cannot be proven. Build systems commonly produce artifacts without a durable, verifiable record of which tools ran, in what order, and under whose authority, which leaves downstream consumers unable to distinguish a legitimate build from a tampered one. Witness addresses this by attesting each step of the supply chain as it occurs, normalizing those records into in-toto attestations, and then verifying them against policy. That lets a team confirm how software was produced and what tools were used, ensure each step was completed by authorized users and machines, and detect potential tampering or malicious activity before an artifact reaches deployment. It also supports distributing attestations and policy across air gaps.
Key capabilities
- Attestation generation through a dynamic CLI that integrates into pipelines and infrastructure to record each SDLC step as an in-toto attestation.
- Policy verification through an embedded OPA Rego policy engine, so software can be checked as having been handled safely from source to deployment.
- Implementation of the in-toto specification including ITE-5, ITE-6, and ITE-7.
- Keyless signing with Sigstore and SPIFFE/SPIRE, plus integration with RFC3161 compatible timestamp authorities.
- Attestation storage with Archivista.
- Process tracing and process tampering prevention, marked experimental in the README.
- Deployment in containerized and non-containerized environments without elevated privileges, with integrations for GitLab, GitHub, AWS, and GCP.
Who uses it and how
- CI/CD owners insert the Witness CLI as a pipeline step on GitLab or GitHub so that every build step emits an attestation rather than relying on after-the-fact logs.
- Security and compliance teams write OPA Rego policy and gate promotion or deployment on successful verification of the artifact's recorded history.
- Regulated or classified environments use the air-gap distribution of attestations and policy to carry provenance evidence between isolated networks.
- Multi-cloud teams lean on the AWS and GCP integrations to capture provenance for workloads built and run across those providers.
- Operators running constrained or mixed infrastructure deploy Witness in containerized and non-containerized modes without needing elevated privileges.
Getting started
Installation requires only the Witness binary, which can be downloaded from the releases page on GitHub or fetched with the install script for the latest release.
How it compares
Witness sits inside the CNCF in-toto ecosystem rather than replacing it: it implements the in-toto specification, and it composes with Sigstore and SPIFFE/SPIRE for keyless signing, with Archivista for attestation storage, and with OPA Rego for policy evaluation. Teams already using those components can add Witness as the pipeline-side tool that generates and verifies the metadata those systems consume. In this registry it does not stand alone on the attestation and verification problem, but it is the piece that ties those named tools into a working supply chain workflow.
When to use it — and when not to
A self-hoster must operate the pieces Witness depends on, including Archivista for attestation storage, an OPA Rego policy authoring practice, and a keyless signing path through Sigstore or SPIFFE/SPIRE, so the tool is not a single binary that solves provenance on its own. Teams that want a turnkey hosted service, or that cannot invest in running and writing policy for those supporting systems, should look elsewhere; the README notes that commercial services exist from TestifySec and are not part of the CNCF sponsorship of Witness. The project also carries 75 open issues, and its process tracing and tampering prevention capability is explicitly experimental, so it should not be treated as a mature control in that area.
project readme (upstream, from github) — read inline
Witness


Witness originated at TestifySec and was later donated to the CNCF in-toto ecosystem. It is now maintained by the open community.
DOCS •
CONTRIBUTING •
LICENSE
`bash
What does Witness do?
✏️ Attests - Witness is a dynamic CLI tool that integrates into pipelines and infrastructure to create an
audit trail for your software's entire journey through the software development lifecycle (SDLC) using the in-toto specification.
🧐 Verifies - Witness also features its own policy engine with embedded support for OPA Rego, so you can
ensure that your software was handled safely from source to deployment.
What can you do with Witness?
- Verify how your software was produced and what tools were used
- Ensure that each step of the supply chain was completed by authorized users and machines
- Detect potential tampering or malicious activity
- Distribute attestations and policy across air gaps
Key Features
- Integrations with GitLab, GitHub, AWS, and GCP.
- Designed to run in both containerized and non-containerized environments without elevated privileges.
- Implements the in-toto specification (including ITE-5, ITE-6 and ITE-7)
- An embedded OPA Rego policy engine for policy enforcement
- Keyless signing with Sigstore and SPIFFE/SPIRE
- Integration with RFC3161 compatible timestamp authorities
- Process tracing and process tampering prevention (Experimental)
- Attestation storage with Archivista
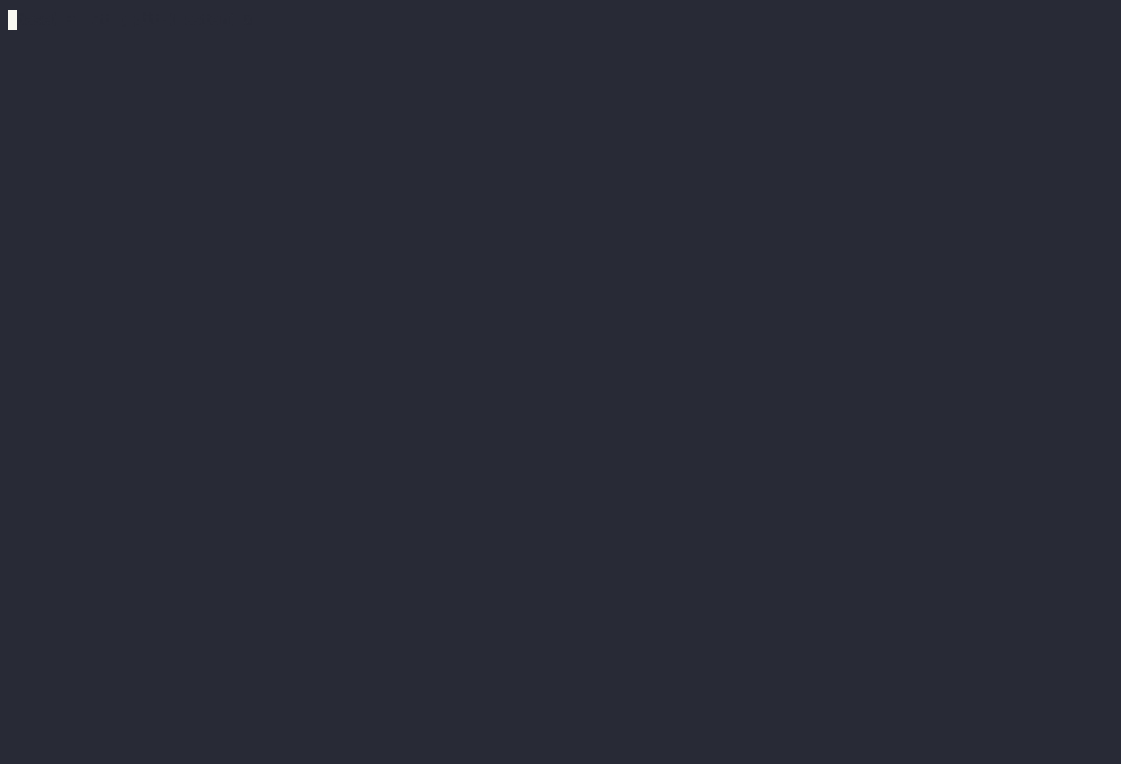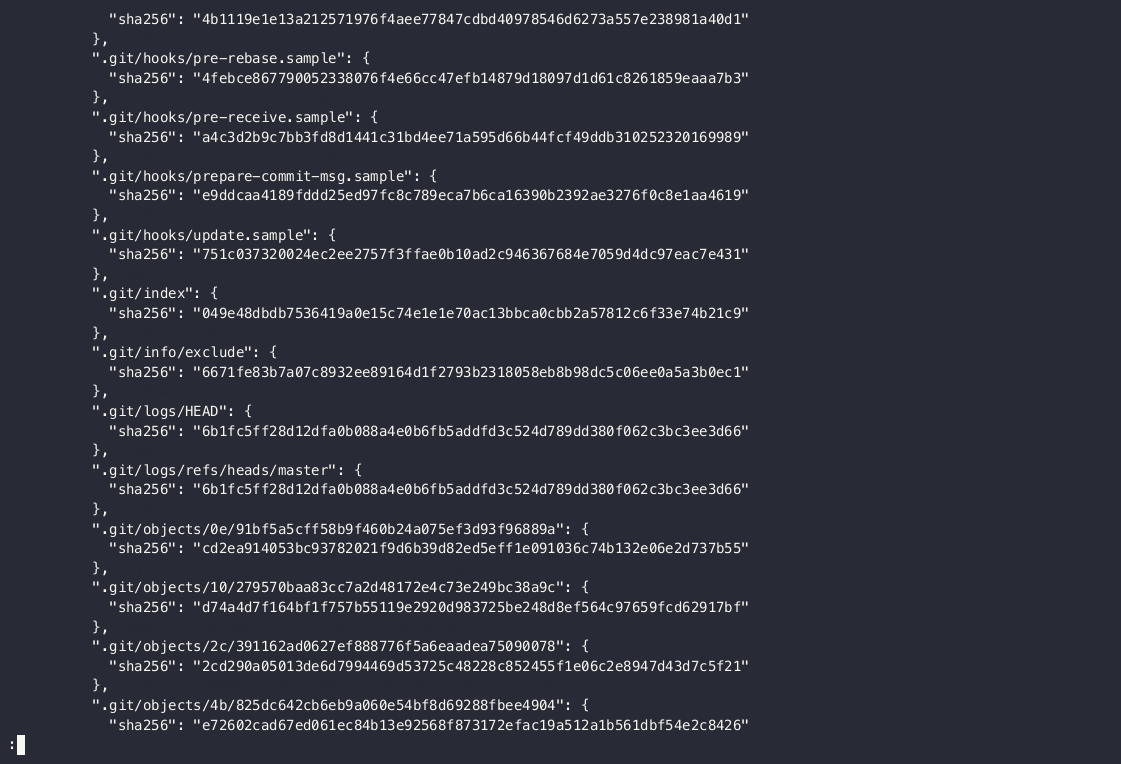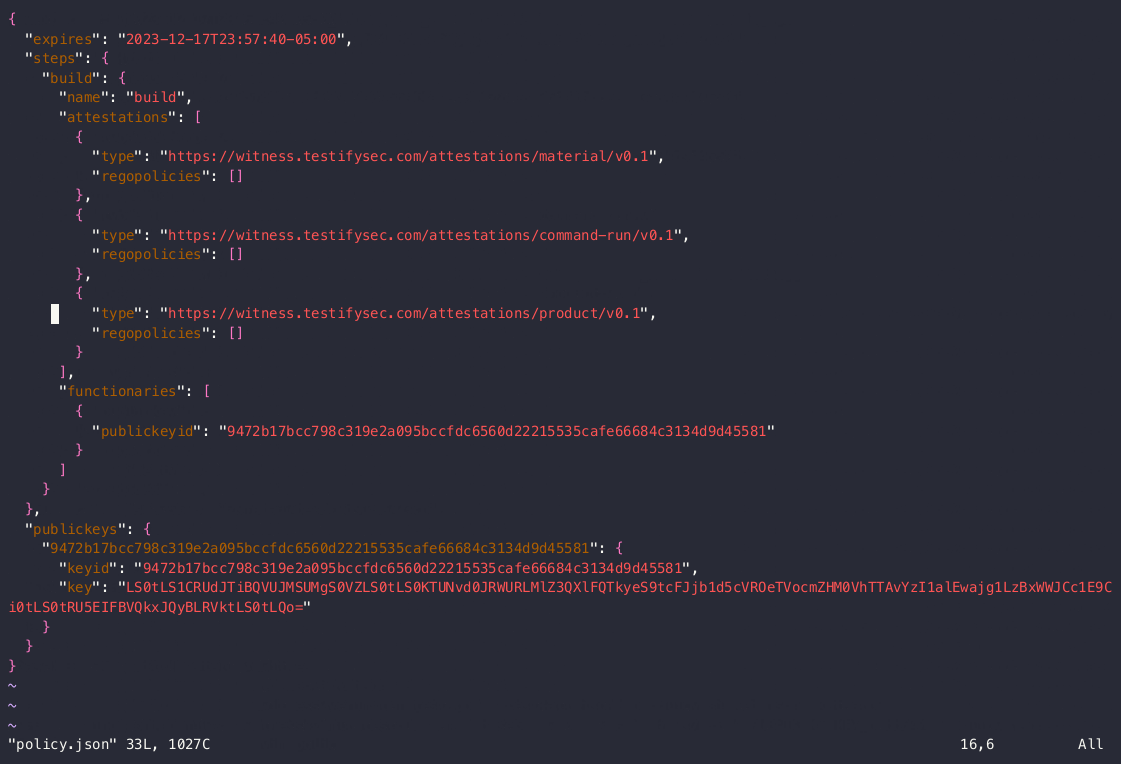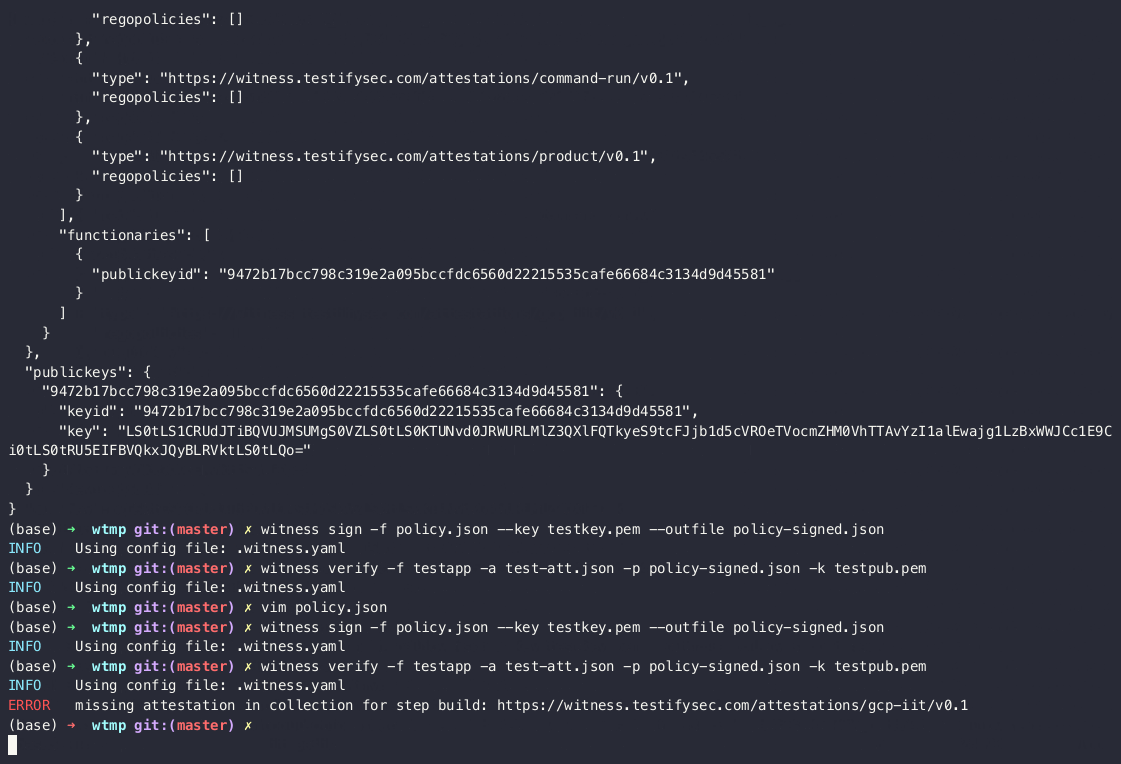
Demo
Quick Start
Installation
To install Witness, all you will need is the Witness binary. You can download this from the releases page or use the install script to download the
latest release:
bash <(curl -s https://raw.githubusercontent.com/in-toto/witness/main/install-witness.sh)
If you want install it manually and verify its integrity follow the instructions in the INSTALL.md.
Tutorials
Check out our Tutorials:
Media
Check out some of the content out in the wild that gives more detail on how the project can be used.
Get Involved with the Community!
Join the CNCF Slack and join the #in-toto-witness channel. You might also be interested in joining the #in-toto channel for more general in-toto discussion, as well as
the #in-toto-archivista channel for discussion regarding the Archivista project.
Community & Commercial Support
- Community channels – Slack, GitHub Issues, and bi-weekly office hours are free and open to all contributors.
- Commercial platform & SLAs – TestifySec offers managed Witness/Archivista hosting, and 24 × 7 support.
(These commercial services are provided by TestifySec and are not part of the CNCF sponsorship of Witness.)