TheIdServer is a free, open source identity & access management (iam) project written in C# and released under Apache-2.0. It has 756 GitHub stars, 92 forks and 2 open issues, and was last pushed 2 days ago. On this registry it ranks #58 of 64 tracked projects in Identity & Access Management (IAM), with 5 head-to-head comparisons available.

What is TheIdServer?

TheIdServer is an open-source identity and access management server for .NET teams that need to issue OpenID/Connect, OAuth2, WS-Federation and SAML 2.0 tokens from a single self-hosted system with a browser-based admin interface.

What it is

TheIdServer is an identity server written in C# for the .NET and ASP.NET Core ecosystem. It is built on two libraries: Duende IdentityServer, which implements the OpenID Connect and OAuth 2.0 protocols for ASP.NET Core applications, and ITFoxtec Identity SAML 2.0, which implements SAML-P for both the identity provider (IdP) and relying party (RP) roles. The project combines these into one deployable server that also ships an administration user interface, and it is released under the Apache-2.0 licence.

The concrete problem it solves is consolidating several federation protocols that would otherwise each require separate tooling. Applications on the web — browsers, mobile apps, web APIs and single-page applications — need to authenticate users and grant access to resources without exposing credentials to those applications, and different consumers speak different protocols: OpenID/Connect and OAuth2 for modern apps, WS-Federation and SAML 2.0 for enterprise federation. TheIdServer implements all Duende IdentityServer features plus a SAML 2.0 identity provider behind one admin interface, replacing the need to run a stack of independent sign-in servers to cover that protocol spread.

Key capabilities

  • Implements every Duende IdentityServer feature, including OpenID/Connect and OAuth 2.0 token issuance, on top of the ASP.NET Core stack.
  • Acts as a SAML 2.0 Identity Provider through ITFoxtec Identity SAML 2.0, supporting both IdP and relying party roles.
  • Supports WS-Federation alongside OpenID/Connect, OAuth2 and SAML 2.0 from the same server.
  • Ships an admin app built with Blazor WebAssembly for managing clients, users and identity configuration through a browser.
  • Integrates key material with Azure Key Vault using the modern Azure.Security.KeyVault.Keys SDK, including DefaultAzureCredential support for Managed Identity and Azure CLI, with AzureKeyVaultTenantId required for Service Principal authentication.
  • Publishes its documentation as a browsable HTML site generated from the repository's markdown, with dedicated pages such as doc/DATA_PROTECTION.md and doc/KEYS_ROTATION.md.
  • Is built and published through CI, with an AppVeyor build, a SonarCloud quality gate, and Docker images produced by the docker.yml GitHub Actions workflow.

Who uses it and how

  • Operators who want to evaluate the server quickly use the hosted in-memory instance on Heroku at theidserver-duende.herokuapp.com, which logs in with alice / Pass123$.
  • Development teams deploying on their own infrastructure run it as a .NET application or as a container, pulling images from the aguafrommars ArtifactHub repository.
  • Administrators who are migrating from the older Azure integration follow doc/DATA_PROTECTION.md and doc/KEYS_ROTATION.md to move existing encrypted data to the new Key Vault SDK, which the project states remains fully compatible.
  • Projects needing enterprise federation use it as the single provider when some relying parties consume SAML 2.0 or WS-Federation while others consume OpenID/Connect.

Getting started

Run the project locally with the .NET SDK from the repository, or deploy it by pulling the published Docker image from the aguafrommars ArtifactHub repository; the same images are built automatically by the docker.yml workflow. For a zero-install look, the in-memory demo instance is available at theidserver-duende.herokuapp.com.

How it compares

TheIdServer does not offer itself as an alternative to Duende IdentityServer or ITFoxtec Identity SAML 2.0 — it is assembled from both, so it inherits their protocol coverage rather than competing with them. The project facts name no other comparable identity servers, so it stands alone in this registry.

When to use it — and when not to

A self-hoster must operate the server itself: a persistent database backing users and configuration (the hosted demo deliberately runs an in-memory version), any Azure Key Vault used for data protection, and the container or host that runs it. It is a poor fit for teams that want a managed identity provider without running infrastructure, and for anyone needing a documented commercial support contract — the README leans on links to a separate documentation site and badges rather than self-contained setup instructions, so expect to read the external docs before deploying.

project readme (upstream, from github) — read inline

TheIdServer

OpenID/Connect, OAuth2, WS-Federation and SAML 2.0 server based on Duende IdentityServer and ITfoxtec Identity SAML 2.0.

OpenID/Connect, OAuth2, WS-Federation and SAML 2.0 are protocols that enable secure authentication and authorization of users and applications on the web. They allow users to sign in with their existing credentials from an identity provider (such as Google, Facebook, Microsoft, Twitter ans so-on) and grant access to their data and resources on different platforms and services. These protocols also enable developers to create applications that can interact with various APIs and resources without exposing the user's credentials or compromising their privacy. Some examples of applications that use these protocols are web browsers, mobile apps, web APIs, and single-page applications.

Duende IdentityServer is a framework that implements OpenID Connect and OAuth 2.0 protocols for ASP.NET Core applications. It allows you to create your own identity and access management solution that can integrate with various identity providers and APIs.

ITfoxtec Identity SAML 2.0 is a framework that implements SAML-P for both Identity Provider (IdP) and Relying Party (RP).

TheIdServer implements all Duende IdentityServer features, a SAML 2.0 Identity Provider and comes with an admin UI.

Quality gate

Build status Docker Artifact HUB libs.tech recommends

⚠️ Azure Key Vault Update

TheIdServer now uses the modern Azure.Security.KeyVault.Keys SDK. The old Microsoft.Azure.KeyVault SDK is obsolete.

Key changes:

  • AzureKeyVaultTenantId is now required when using Service Principal authentication
  • New DefaultAzureCredential support (recommended) - works with Managed Identity and Azure CLI
  • Existing encrypted data remains 100% compatible

See Data Protection and Keys Rotation documentation for migration details.

Documentation

Thanks @ldeluigi and its markdown-docs GitHub action. All markdown files are deployed in html here.

Try it now at https://theidserver-duende.herokuapp.com/

login: alice
pwd: Pass123$

An in-memory database version is available on Heroku.

Give a Star! :star:

If you like or are using this project to learn or start your solution, please give it a star. Thanks!

Or if you're feeling really generous, we support sponsorships.

Choose your favorite:

Main features

Admin app
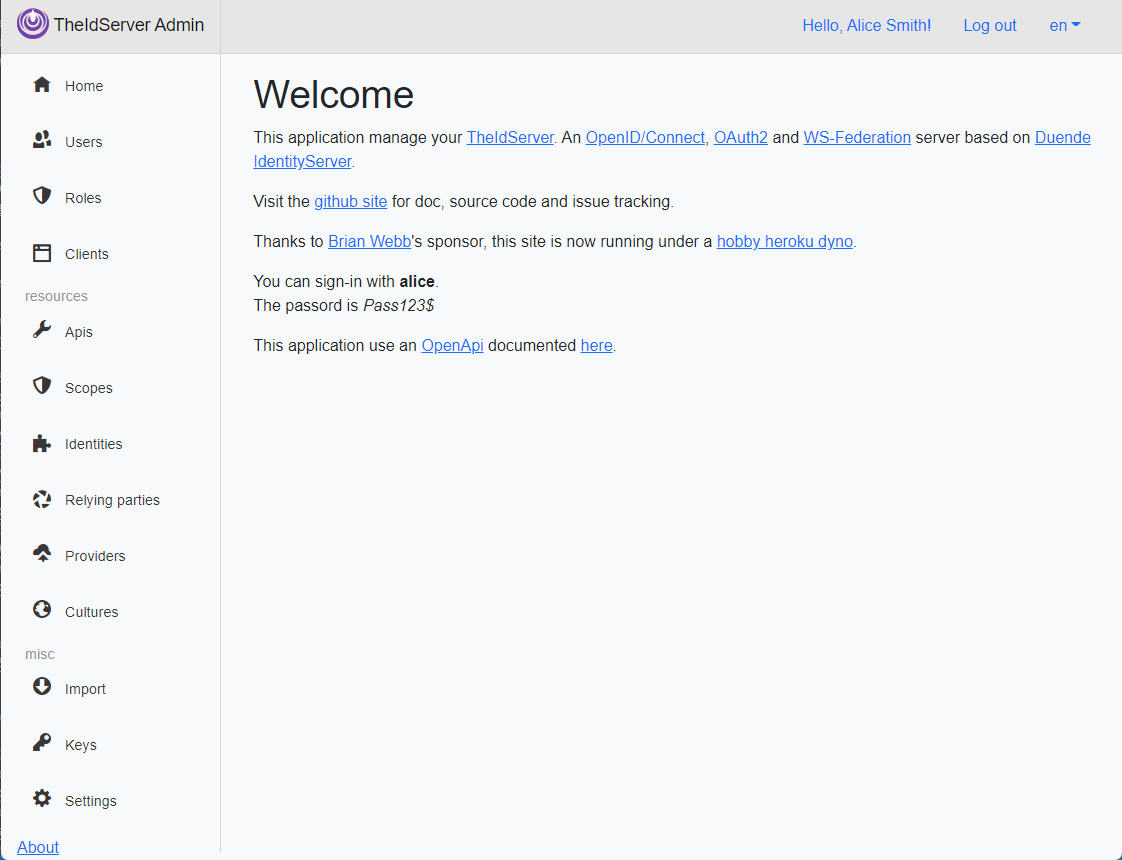
home

Server

Setup

Build from source

You can build the solution with Visual Studio or use the dotnet build command.
To build docker images launch at solution root:

docker build -t aguacongas/theidserver.duende:dev -f "./src/Aguacongas.TheIdServer.Duende/Dockerfile" .
docker build -t aguacongas/theidserverapp:dev -f "./src/Aguacongas.TheIdServer.BlazorApp/Dockerfile" .

Contribute

We warmly welcome contributions. You can contribute by opening an issue, suggest new a feature, or submit a pull request.

Read How to contribute and Contributor Covenant Code of Conduct for more information.

OIDC Certification test result

The server pass the oidcc-basic-certification-test-plan with some warnings. It is anticipated that it will pass the certification process, but we need your assistance. Please sponsor this project to help us pay the required certification fee.

Choose your favorite:

IdentityServer4 end of support

The old IS4 version has been remove from the solution as IS4 reach is end of support.

Frequently asked questions

Is TheIdServer free to use?

TheIdServer is open source under the Apache-2.0 licence. There is no licence fee and no seat count — you can self-host it or, where the project offers one, pay a vendor for a managed version instead.

What does TheIdServer do?

OpenID/Connect, OAuth2, WS-Federation and SAML 2.0 server based on Duende IdentityServer and ITFoxtec Identity SAML 2.0 with its admin UI

What is TheIdServer written in?

TheIdServer is primarily written in C#. Its source is publicly available at https://github.com/Aguafrommars/TheIdServer, and it has 756 GitHub stars.