[!NOTE] Shannon 3.0 is live: deeper security code analysis, more thoroughly vetted findings, a rebuilt CLI, native CI/CD, professional PDF reports, and SARIF.
Shannon is an autonomous, AI pentester for web applications and APIs.
It analyzes your source code, identifies attack paths, and executes real exploits to prove vulnerabilities before they reach production. No exploit, no report.
This repository is Shannon Open Source: the full agent, run locally from your command line.
Launch Shannon
npx @keygraph/shannon@latest
The interactive launcher will guide you through setup and your first pentest.
[!TIP] AI agents and LLMs: start with llms.txt for a concise map of this repository, or use llms-full.txt for the README and docs combined into one file.
Table of Contents
- Table of Contents
- What is Shannon?
- Shannon in Action
- Quick Start
- Key Capabilities
- CI/CD Integrations
- Editions
- Architecture
- Documentation
- Safety, Scope, and Limitations
- License
- Acknowledgements
- About Keygraph
- Community and Support
- Common Questions
What is Shannon?
Shannon is an autonomous AI pentester developed by Keygraph. It performs security testing of web applications and their underlying APIs by combining source-code analysis with live exploitation.
Shannon analyzes your web application's source code to identify potential attack vectors, then uses browser automation and command-line tools to execute real exploits against the running application and its APIs. Only vulnerabilities with a working proof-of-concept are included in the final report.
Shannon is the agent. This repository is Shannon Open Source, the standalone pentester you run yourself. The same Shannon also powers the Keygraph platform, Keygraph's commercial pentesting product. See Editions for how the two compare.
Why Shannon Exists
Thanks to tools like Claude Code and Cursor, your team ships code non-stop. But your penetration test? That happens once a year. This creates a massive security gap. For the other 364 days, you could be unknowingly shipping vulnerabilities to production.
Shannon closes that gap by providing on-demand, automated penetration testing that can run against every build or release.
Why "Shannon"?
It's named after Claude Shannon, the father of information theory. At its core, pentesting is an information problem: every probe reduces uncertainty about a system's state. The best tools maximize the signal gained from every request, turning those bits of knowledge into an exploit path.
Also, we wanted you to be able to say, "Hey Claude, run Shannon" to find all the security flaws in your vibe-coded app.
Not a replacement for human pentesters
Shannon is built to work alongside expert pentesters and red teamers, not replace them. Great pentesters understand the business, chain attacks in ways nobody anticipated, and bring years of judgment that current models can't match.
Shannon solves a different problem: there is far more software to test than security teams have time to cover. Critical systems get periodic expert assessments, while the long tail of internal apps, APIs, and fast-moving services rarely gets tested at all.
Shannon shifts pentesting left into the software development lifecycle (SDLC). Use it to run exploitation-backed tests against staging environments and releases at the cadence they actually ship, and save expert human time for the risks that need someone who knows the organization.
Shannon in Action
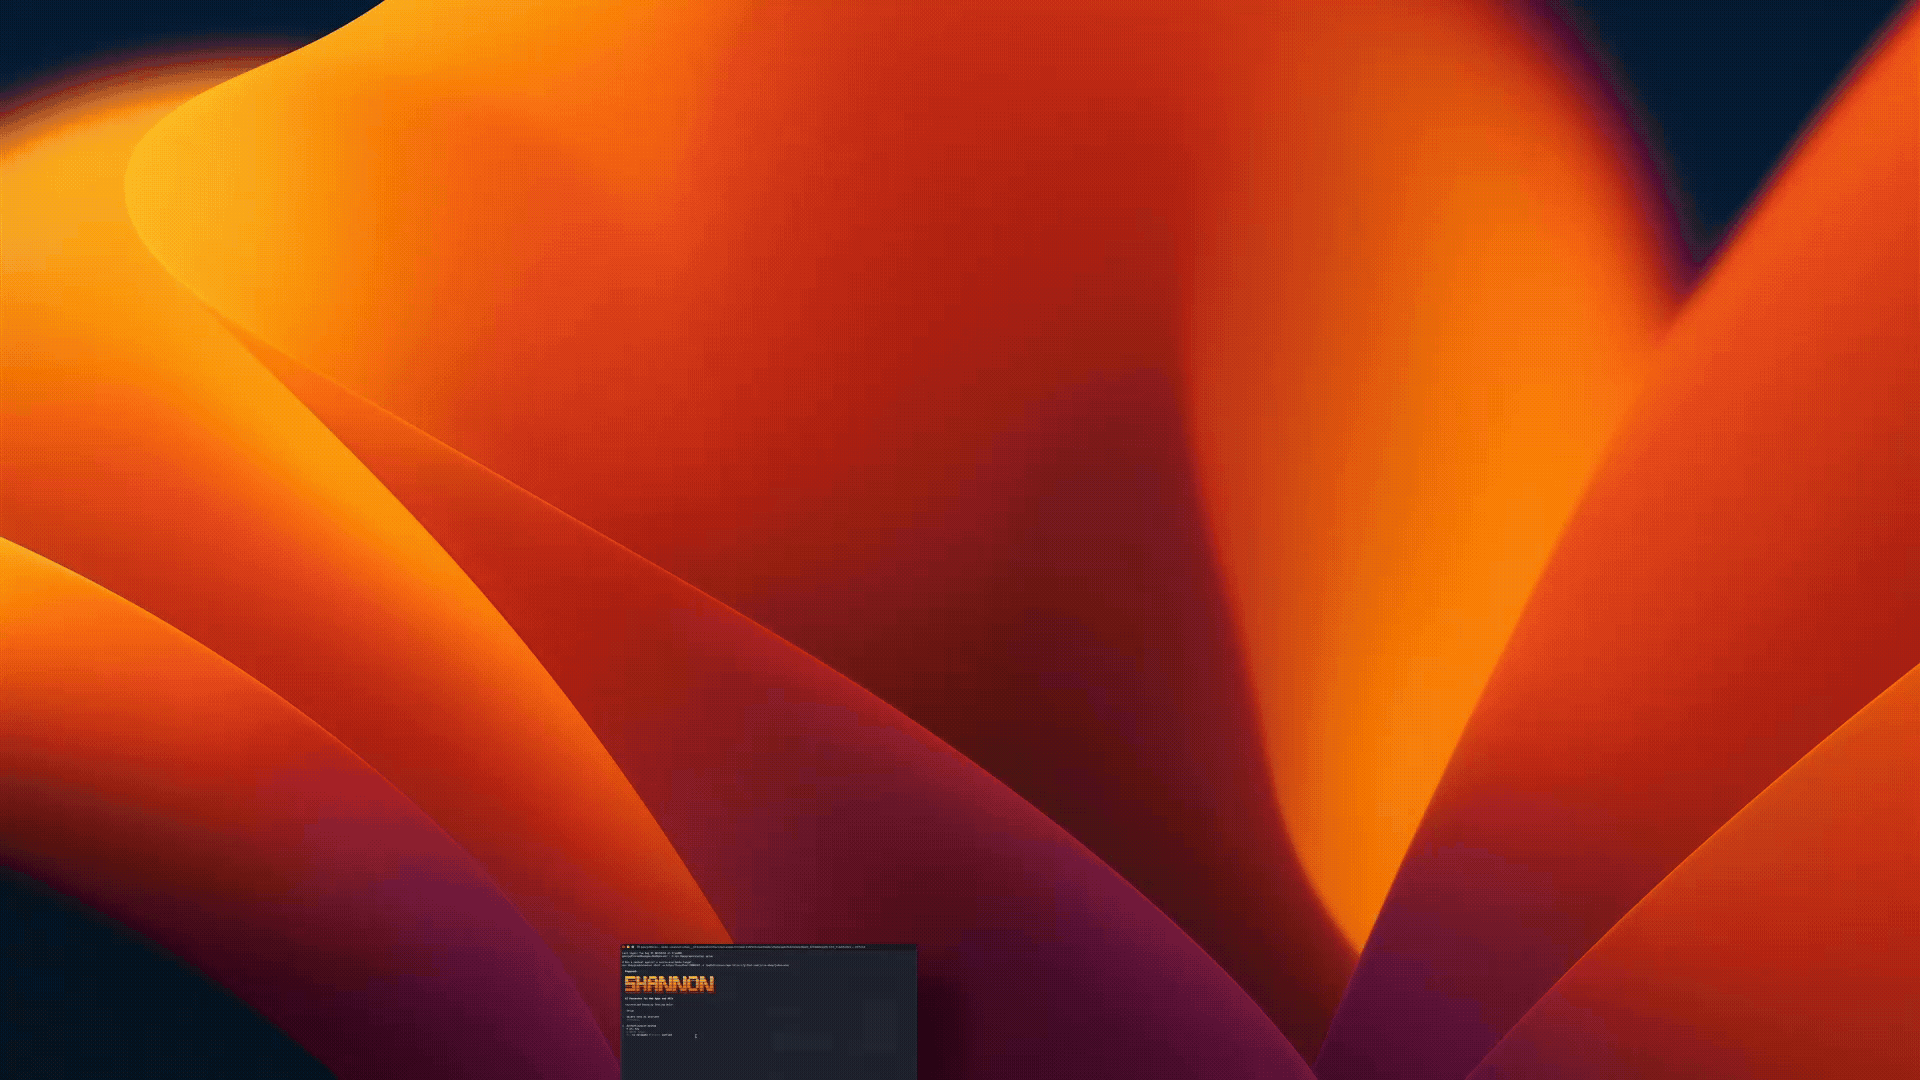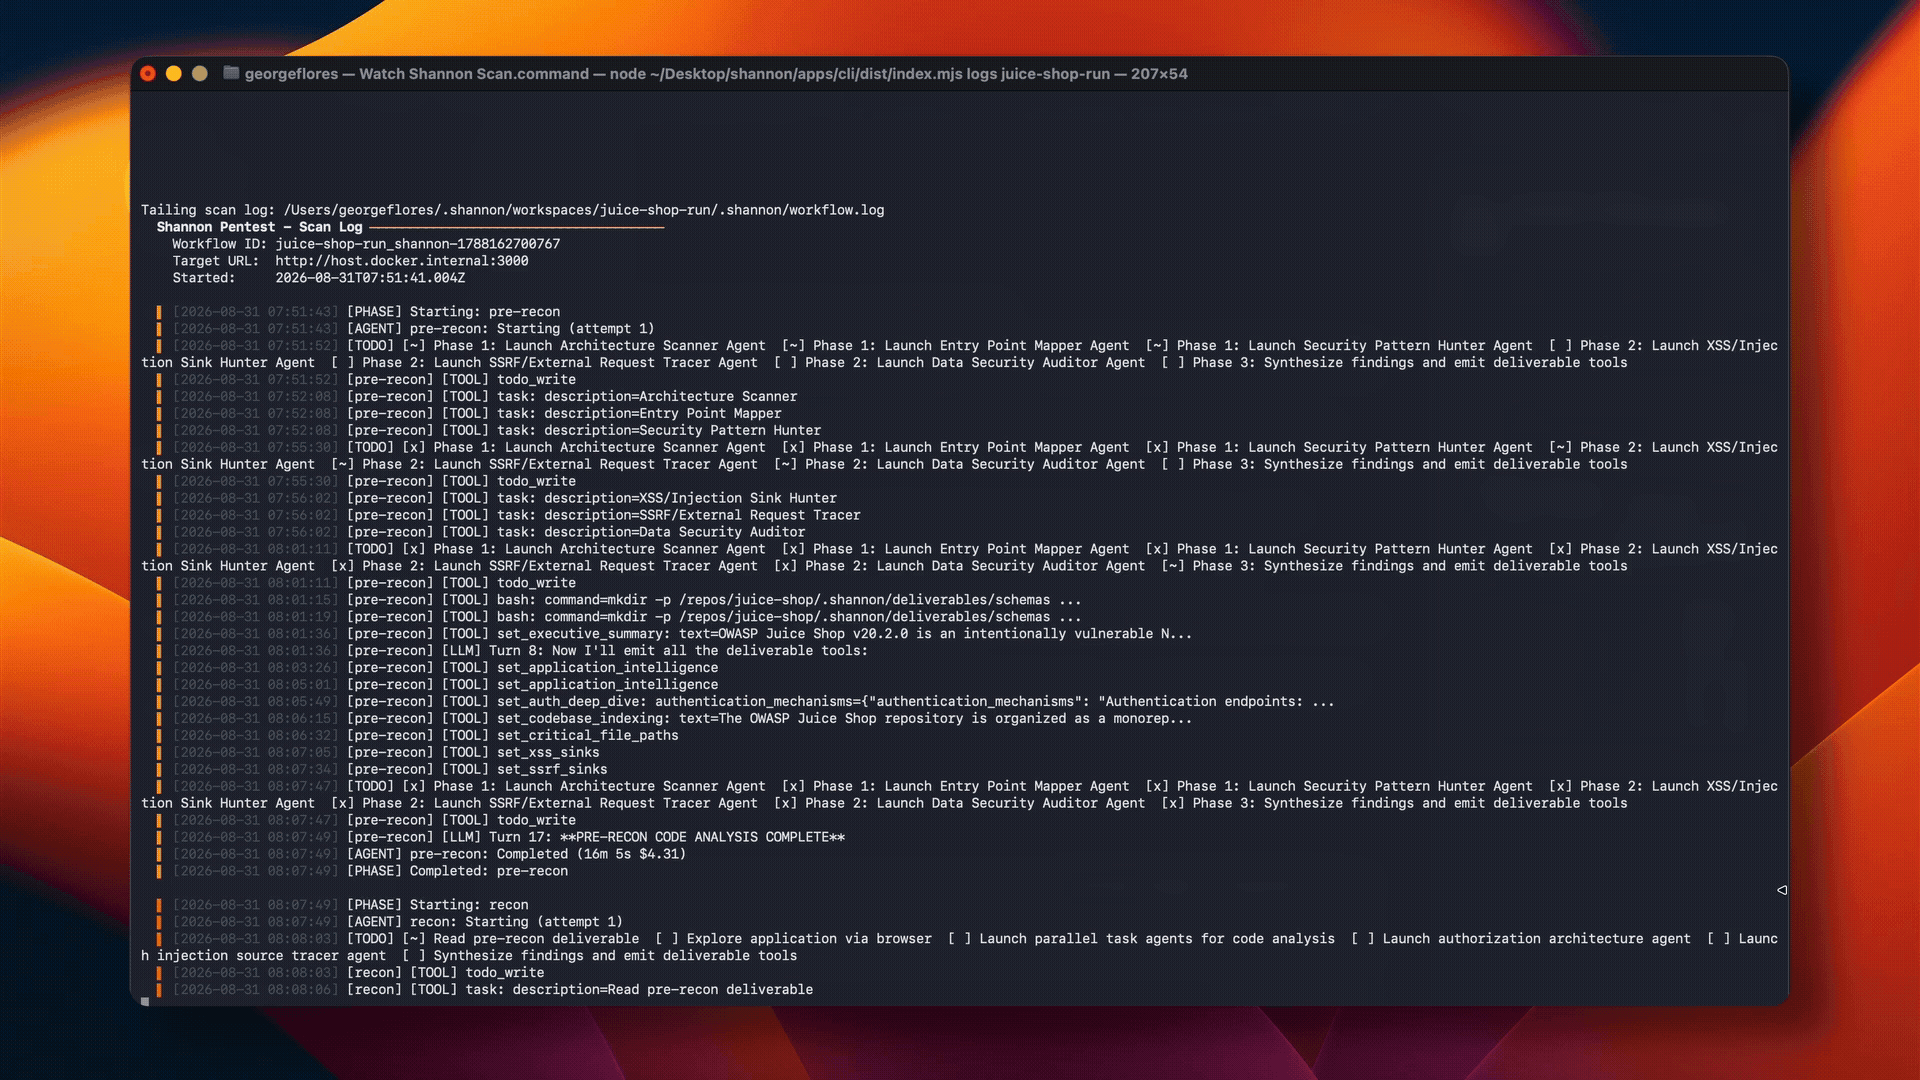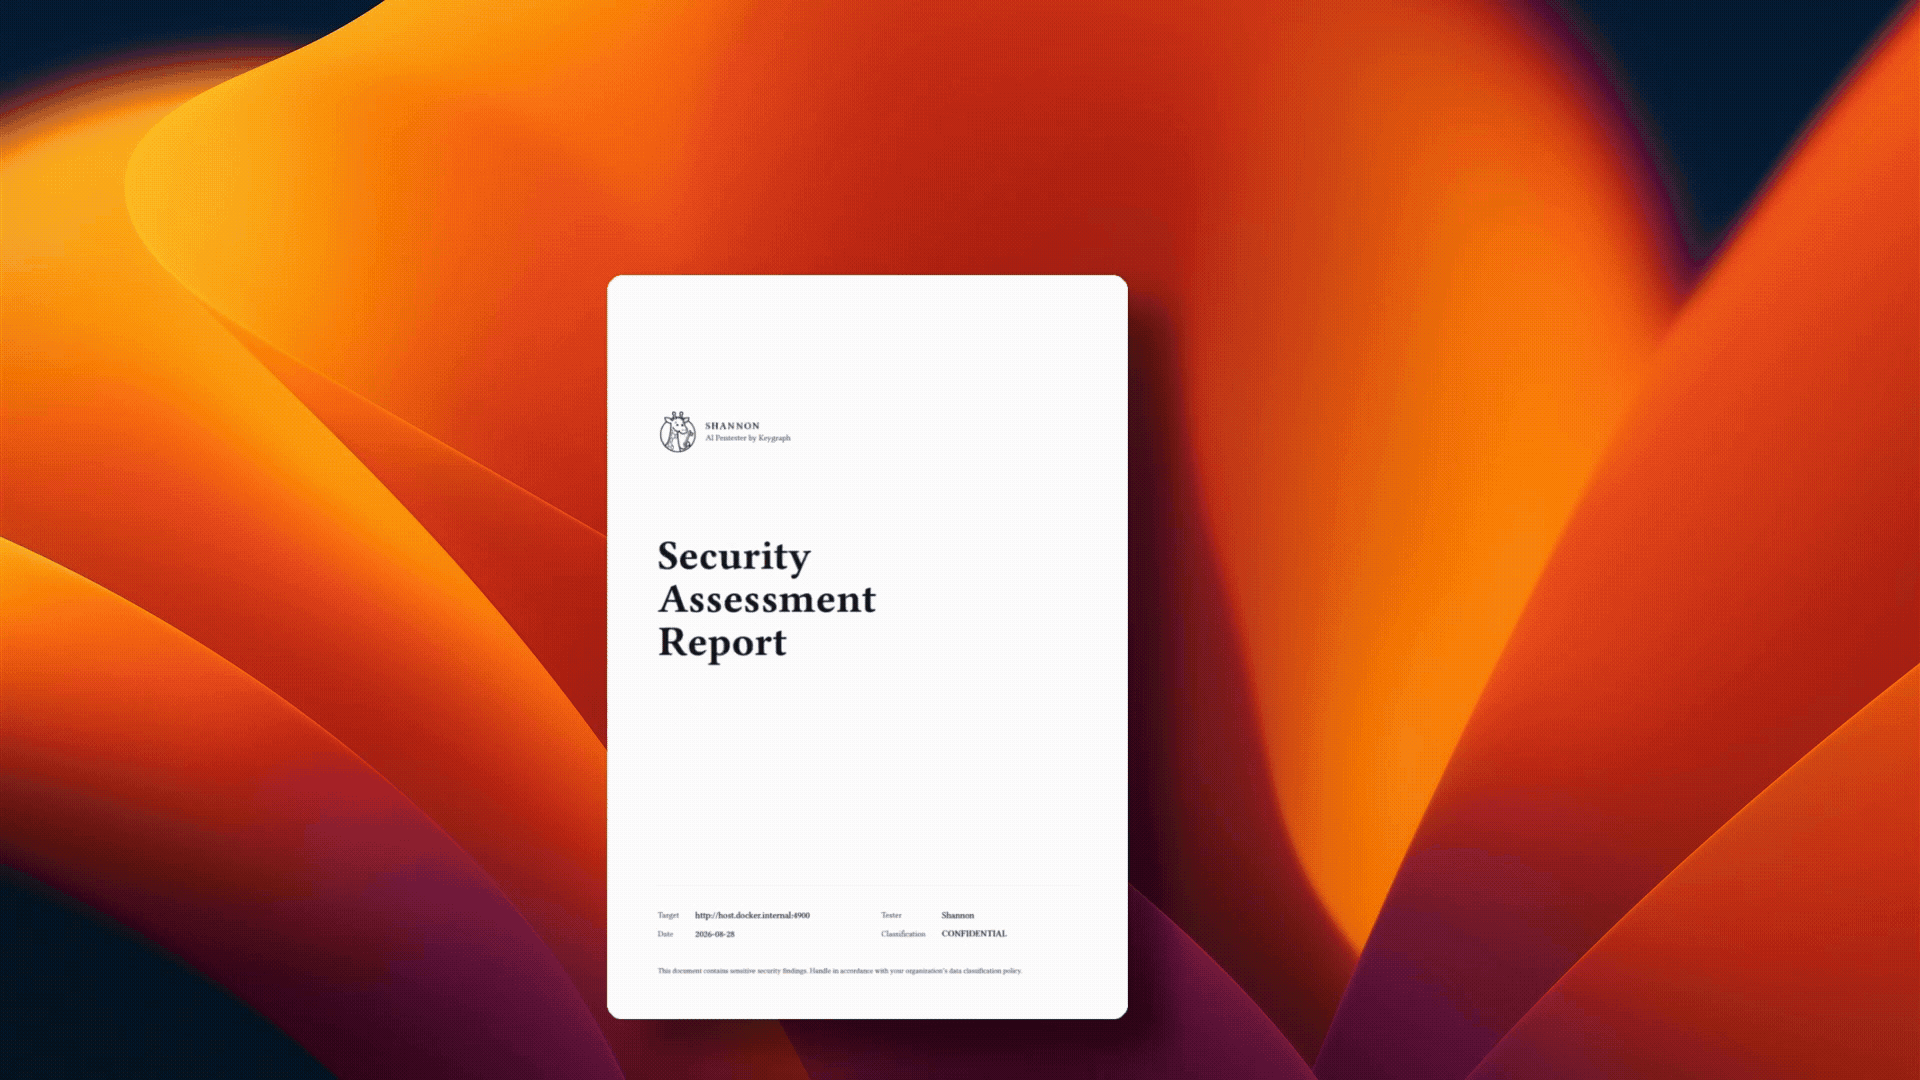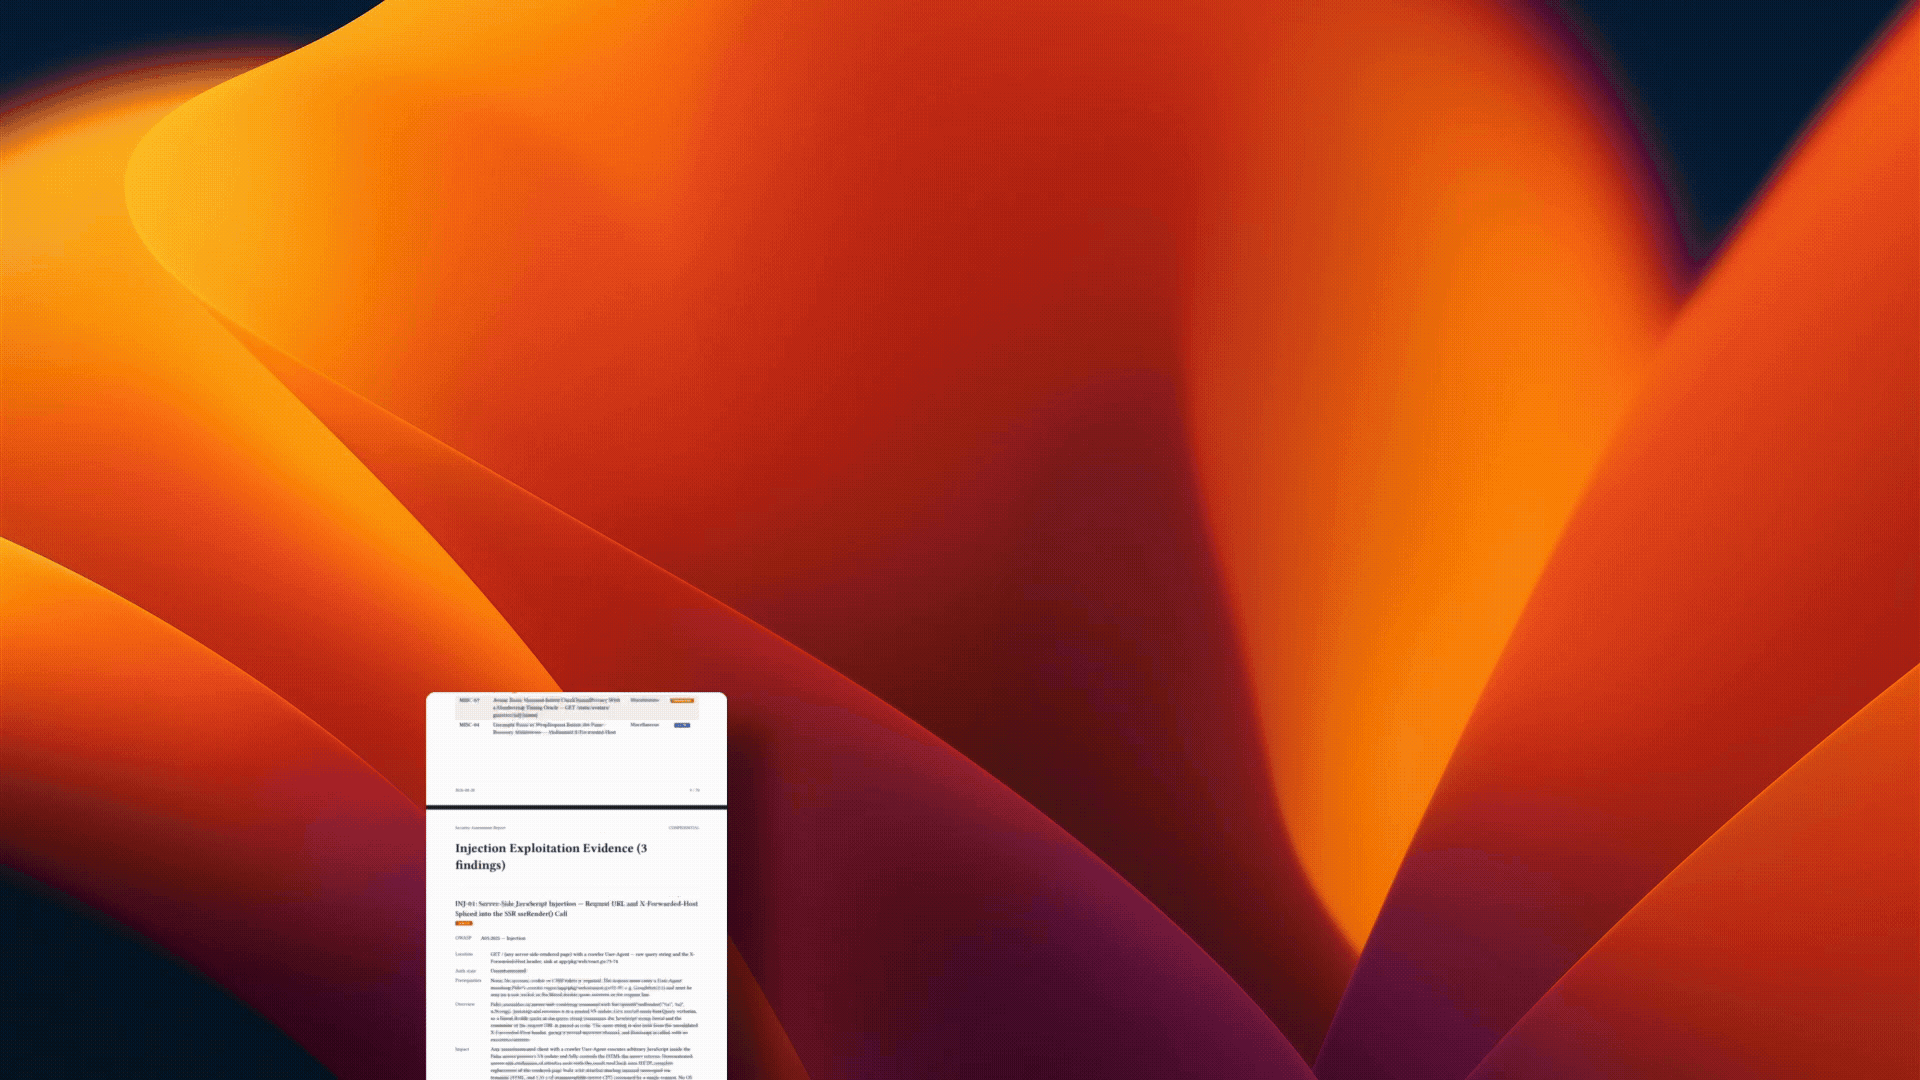
These reports are from Shannon Open Source scans of Photoview 2.4.0, one of the applications in Doyensec's comparison of Aikido and XBOW. We ran Shannon against the same application version and evaluated its results separately. Read the Doyensec study and our Shannon follow-up comparison for the methodology, limitations, costs, and results.
| Model | Report | SARIF |
|---|---|---|
| DeepSeek v4 Flash | View report | SARIF |
| Grok 4.6 | View report | SARIF |
| Claude Opus 5 | View report | SARIF |
Quick Start
Prerequisites
- Docker: required for the worker container.
- Node.js 18+: required for the recommended
npxworkflow. - AI provider credentials: Shannon runs on Anthropic, OpenAI, xAI, AWS Bedrock, and any other provider in the harness catalogue — each of which you can point at a proxy or LLM gateway through a custom base URL, and a model the catalogue does not yet carry can be described with a custom model configuration. You bring your own key, and Keygraph never proxies your model traffic. Shannon is provider-agnostic. See AI providers for suggested model IDs.
- Cyber safeguards cleared with your provider: Anthropic and OpenAI apply real-time safeguards to cyber-security workloads, which can interrupt a scan mid-run. Complete their guidance for legitimate security testers before your first run - see AI providers.
Run Shannon
[!WARNING] Shannon actively executes exploits. Run it only against applications and environments you own or have explicit written authorization to test. Do not run Shannon against production syste