Mobile-Security-Framework-MobSF is a free, open source api development & testing project written in Python and released under GPL-3.0. It has 22,109 GitHub stars, 3,800 forks and 31 open issues, and was last pushed 29 hours ago. On this registry it ranks #10 of 187 tracked projects in API Development & Testing, with 5 head-to-head comparisons available. It gained 249 stars over the last 30 tracked days.

What is Mobile-Security-Framework-MobSF?

Mobile Security Framework (MobSF) is an open-source, automated, all-in-one framework for mobile application security testing across Android, iOS, and Windows Mobile that performs static and dynamic analysis for penetration testing, malware analysis, and privacy assessment, built for security researchers, penetration testers, and DevSecOps teams.

What it is

MobSF is a security research platform for mobile applications on Android, iOS, and Windows Mobile. It combines a Static Analyzer, which inspects popular mobile app binaries such as APK, IPA, and APPX as well as source code, with a Dynamic Analyzer that supports Android and iOS applications and provides a platform for interactive instrumented testing, runtime data collection, and network traffic analysis. The project is written for Python 3.12 and above, is licensed under GPL-3.0, and is published both as a PyPI package under the name mobsf and as a Docker image. The README describes it as capable of mobile application security assessment, penetration testing, malware analysis, and privacy analysis.

The concrete problem it solves is the fragmentation of mobile security testing. Rather than assembling separate tooling for each artifact type, a tester or pipeline submits an APK, IPA, APPX, or source tree to one platform and receives static findings and, for Android and iOS, dynamic runtime and network traffic results. It also replaces manual, one-off reviewing in continuous delivery settings: REST APIs and CLI tools let the same engine run as a step inside a DevSecOps or CI/CD pipeline instead of as a human-driven, ad-hoc task. The category listing places it in Developer Tools / API Development & Testing, and its topic list spans android-security, apk, cwe, devsecops, dynamic-analysis, ios-security, malware-analysis, mastg, masvs, and mobile-security.

Key capabilities

  • Static Analyzer for APK, IPA, APPX, and source code, covering the main mobile binary formats.
  • Dynamic Analyzer for Android and iOS applications, offering interactive instrumented testing, runtime data, and network traffic analysis.
  • REST APIs and CLI tools that integrate with a DevSecOps or CI/CD pipeline.
  • Mapping to the MASVS standard and the MASTG testing guide, reflected in the repository topics.
  • CWE-based weakness reporting as part of the assessment output.
  • Official Docker image opensecurity/mobile-security-framework-mobsf, runnable with docker run -it --rm -p 8000:8000 opensecurity/mobile-security-framework-mobsf:latest, with default credentials mobsf/mobsf.
  • Distribution through Android Tamer, BlackArch, and Pentoo, and platform support for macOS, Linux, and Windows.

Who uses it and how

  • Penetration testers assessing Android and iOS application builds who need static findings and instrumented runtime behavior from one interface.
  • Malware analysts examining suspicious APK, IPA, or APPX samples, using the same platform for binary inspection and dynamic observation.
  • DevSecOps and application security teams that call the REST APIs or CLI tools from a pipeline so mobile builds are scanned automatically.
  • Security researchers and trainers, evidenced by appearances at Black Hat Arsenal Asia 2015 and 2018 and Black Hat Arsenal Europe 2023, plus a rank 5 placement in the ToolsWatch 2016 security tools vote and rank 9 in 2017.
  • Analysts working from prebuilt security distributions, since MobSF ships inside Android Tamer, BlackArch, and Pentoo alongside its standalone Docker and Python installs.

Getting started

The README's quick setup pulls and runs the Docker image: docker pull opensecurity/mobile-security-framework-mobsf:latest, then docker run -it --rm -p 8000:8000 opensecurity/mobile-security-framework-mobsf:latest, with the default username and password mobsf/mobsf. A PyPI package named mobsf is also published for environments running Python 3.12 or newer, and full setup guidance lives in the MobSF documentation site.

How it compares

No comparable products are named in the supplied facts, so MobSF stands alone in this registry rather than being positioned against a specific set of alternatives. The only adjacent projects named are security distributions, Android Tamer, BlackArch, and Pentoo, which bundle MobSF rather than compete with it.

When to use it — and when not to

A self-hoster must operate the Docker image or a Python 3.12+ installation, and the default mobsf/mobsf credentials shipped in the image should be replaced before any exposure, since anyone reaching port 8000 could otherwise use the instance. Dynamic analysis additionally depends on a working instrumented test setup, so teams that only want passive binary scanning carry more environment than they need, and organizations that cannot accept the GPL-3.0 licence or that require a vendor-managed service should look elsewhere. Note also that the registry metadata lists the language as JavaScript while the README and PyPI package describe a Python 3.12+ project, so metadata consumers should not treat the language field as authoritative.

project readme (upstream, from github) — read inline

Mobile Security Framework (MobSF)

Mobile Security Framework (MobSF) is a security research platform for mobile applications in Android, iOS and Windows Mobile. MobSF can be used for a variety of use cases such as mobile application security, penetration testing, malware analysis, and privacy analysis. The Static Analyzer supports popular mobile app binaries like APK, IPA, APPX and source code. Meanwhile, the Dynamic Analyzer supports both Android and iOS applications and offers a platform for interactive instrumented testing, runtime data and network traffic analysis. MobSF seamlessly integrates with your DevSecOps or CI/CD pipeline, facilitated by REST APIs and CLI tools, enhancing your security workflow with ease.

Made with Love in India

Docker Pulls python PyPI version platform License MobSF tests Quality Gate Status GitHub closed issues CII Best Practices

ToolsWatch Best Security Tools 2016 ToolsWatch Best Security Tools 2017 Blackhat Arsenal Asia 2015 Blackhat Arsenal Asia 2018 Blackhat Arsenal Europe 2023

MobSF is also bundled with Android Tamer, BlackArch and Pentoo.

Support MobSF

Donate to MobSF

Has MobSF made a difference for you? Show your support and help us innovate with a donation. It's easy to build open source, maintaining one is a different story.

Long live open source!

Documentation

Quick setup with docker

docker pull opensecurity/mobile-security-framework-mobsf:latest
docker run -it --rm -p 8000:8000 opensecurity/mobile-security-framework-mobsf:latest

# Default username and password: mobsf/mobsf

See MobSF Documentation

Collaborators

Ajin Abraham india | Magaofei china | Matan Dobrushin israel | Vincent Nadal france

e-Learning Courses & Certifications

MobSF Course Automated Mobile Application Security Assessment with MobSF -MAS

Android Security Tools Course Android Security Tools Expert -ATX

MobSF Support

  • Free Support: Free limited support, questions, help and discussions, join our Slack channel Join_MobSF_Slack
  • Enterprise Support: Priority feature requests, live support & onsite training, see MobSF Support Packages
Contribution, Feature Requests & Bugs

  • Read CONTRIBUTING.md before opening bugs, feature requests and pull request.
  • For Project updates and announcements, follow @ajinabraham or @OpenSecurity_IN.
  • Github Issues are only for tracking bugs and feature requests. Do not post support or help queries there. We have a slack channel for that.

Static Analysis - Android
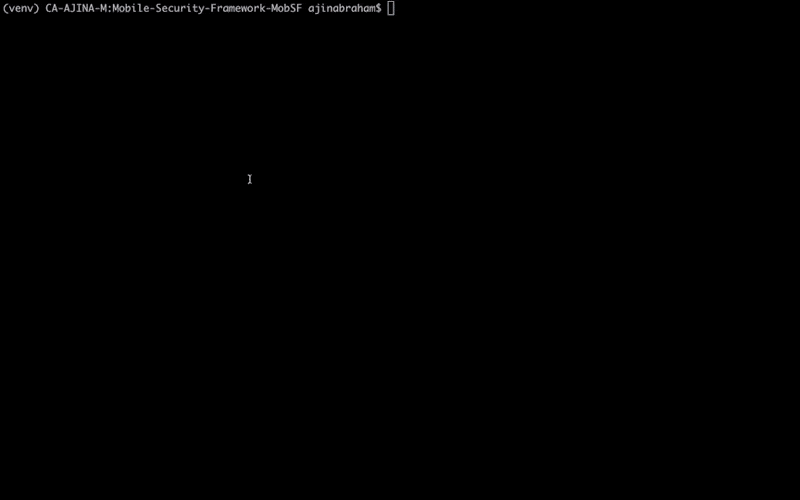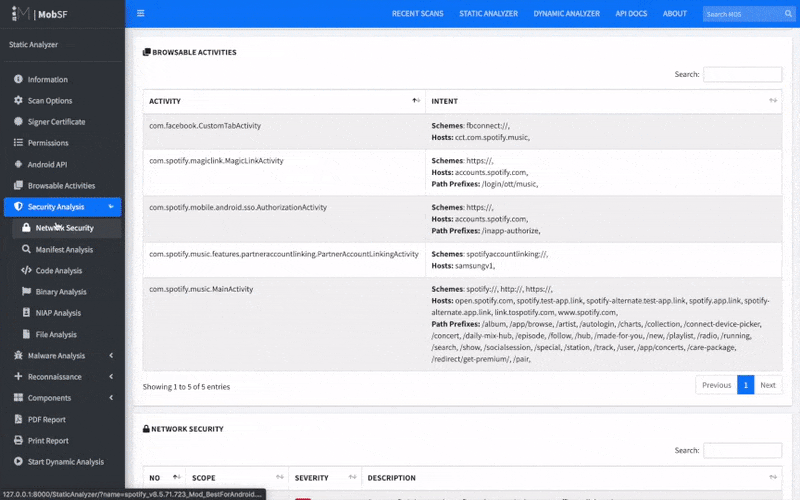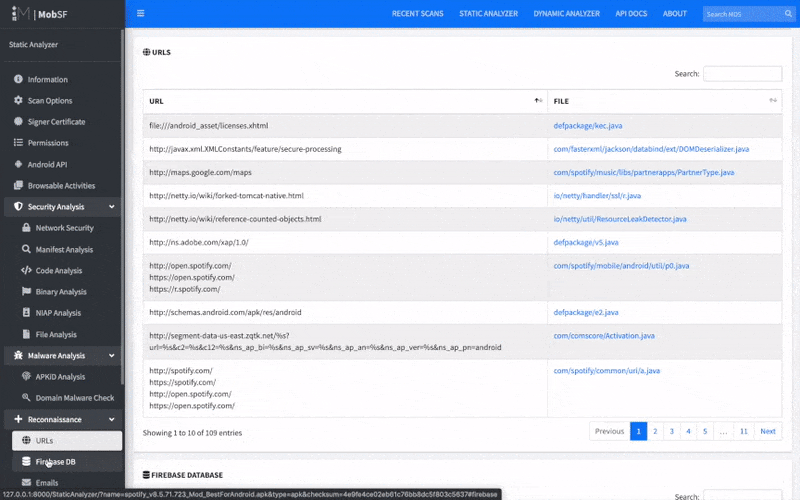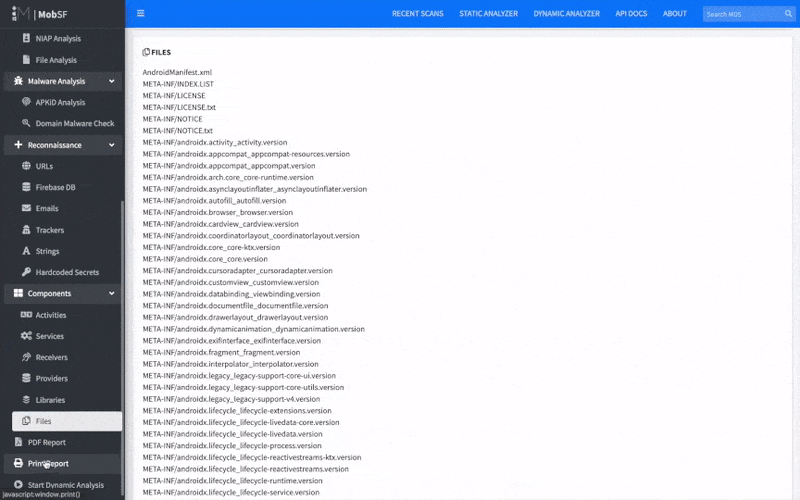
mobsf_android_static_analysis

Static Analysis - iOS

mobsf_ios_ipa_static_analysis

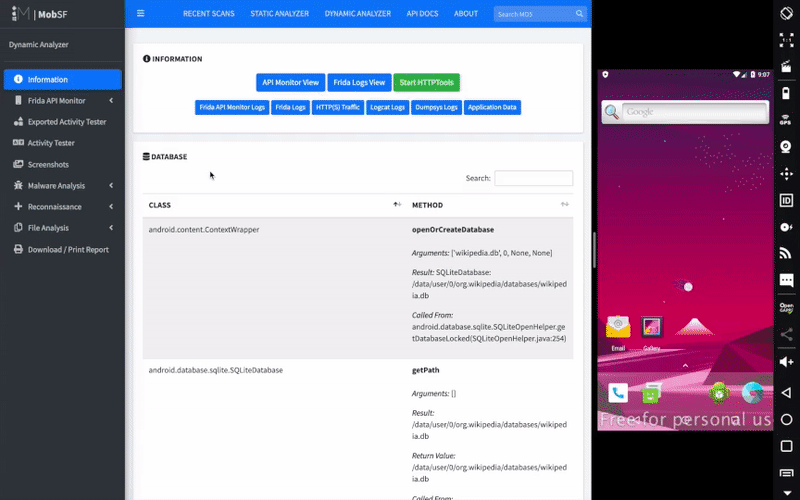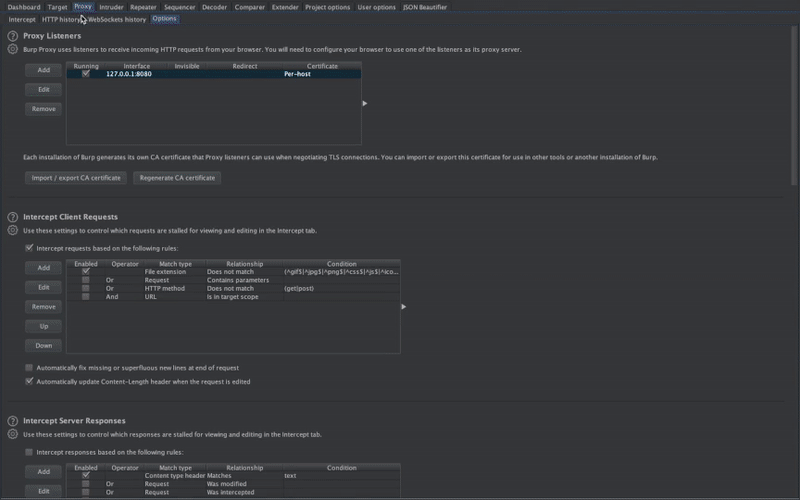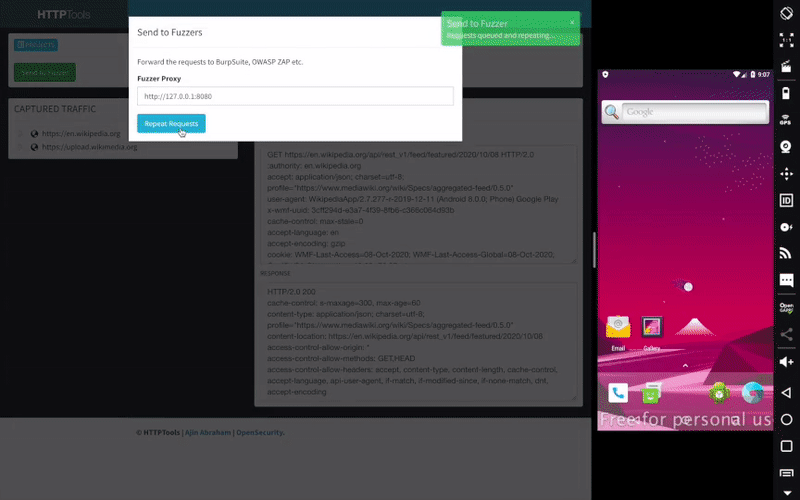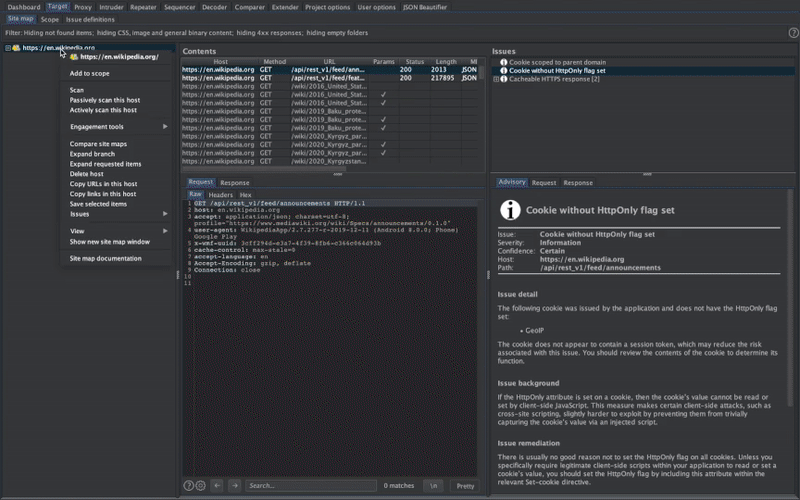
Dynamic Analysis - Android APK

mobsf_android_dynamic_analysis

Web API Viewer

mobsf_web_api_fuzzing_with_burp

Dynamic Analysis - iOS IPA

mobsf_ios_dynamic_analysis

Past Collaborators

Honorable Contributors & Shoutouts

  • Amrutha VC - For the new MobSF logo
  • Dominik Schlecht - For the awesome work on adding Windows Phone App Static Analysis to MobSF
  • Esteban - Better Android Manifest Analysis and Static Analysis Improvement.
  • Matan Dobrushin - For adding Android ARM Emulator support to MobSF - Special thanks goes for cuckoo-droid
  • Shuxin - Android Binary Analysis
  • Abhinav Saxena - (@xandfury) - For Travis CI and Logging integration
  • netguru Netguru (@karolpiateknet, @mtbrzeski) - For iOS Swift support, Rule contributions and SAST refactoring.
  • Maxime Fawe - (@Arenash13) - For Matching Strategy implementation of SAST pattern matching algorithms.
  • Abhinav Sejpal (@Abhinav_Sejpal) - For poking me with bugs, feature requests, and UI & UX suggestions
  • Anant Srivastava (@anantshri) - For Activity Tester Idea
  • Anto Joseph (@antojoseph) - For the help with SuperSU
  • Bharadwaj Machiraju (@tunnelshade) - For writing pyWebProxy from scratch
  • Rahul (@c0dist) - Kali Support
  • MindMac - For writing Android Blue Pill
  • Oscar Alfonso Diaz - (@OscarAkaElvis) - For Dockerfile contributions
  • Thomas Abraham - For JS Hacks on UI
  • Tim Brown (@timb_machine) - For the iOS Binary Analysis Ruleset
  • Shanil Prasad (@Rajuraju14) - For improving iOS ATS Analysis
  • Jovan Petrovic (@JovanPetrovic) - For sponsoring a server to host mobsf.live

Frequently asked questions

Is Mobile-Security-Framework-MobSF free to use?

Mobile-Security-Framework-MobSF is open source under the GPL-3.0 licence. There is no licence fee and no seat count — you can self-host it or, where the project offers one, pay a vendor for a managed version instead.

What does Mobile-Security-Framework-MobSF do?

Mobile Security Framework (MobSF) is an automated, all-in-one mobile application (Android/iOS/Windows) pen-testing, malware analysis and security assessment fra

What is Mobile-Security-Framework-MobSF written in?

Mobile-Security-Framework-MobSF is primarily written in Python. Its source is publicly available at https://github.com/MobSF/Mobile-Security-Framework-MobSF, and it has 22,109 GitHub stars.