khi is a free, open source monitoring & observability project written in Go and released under Apache-2.0. It has 2,087 GitHub stars, 99 forks and 11 open issues, and was last pushed 4 days ago. On this registry it ranks #172 of 270 tracked projects in Monitoring & Observability, with 5 head-to-head comparisons available. It gained 3 stars over the last 30 tracked days.

What is khi?

Kubernetes History Inspector (KHI) is an agentless, open-source log visualization tool that turns Kubernetes audit logs into an interactive timeline and topology view, and it is built for the SREs, platform engineers, and cluster operators who have to reconstruct what happened during a cross-component Kubernetes incident.

What it is

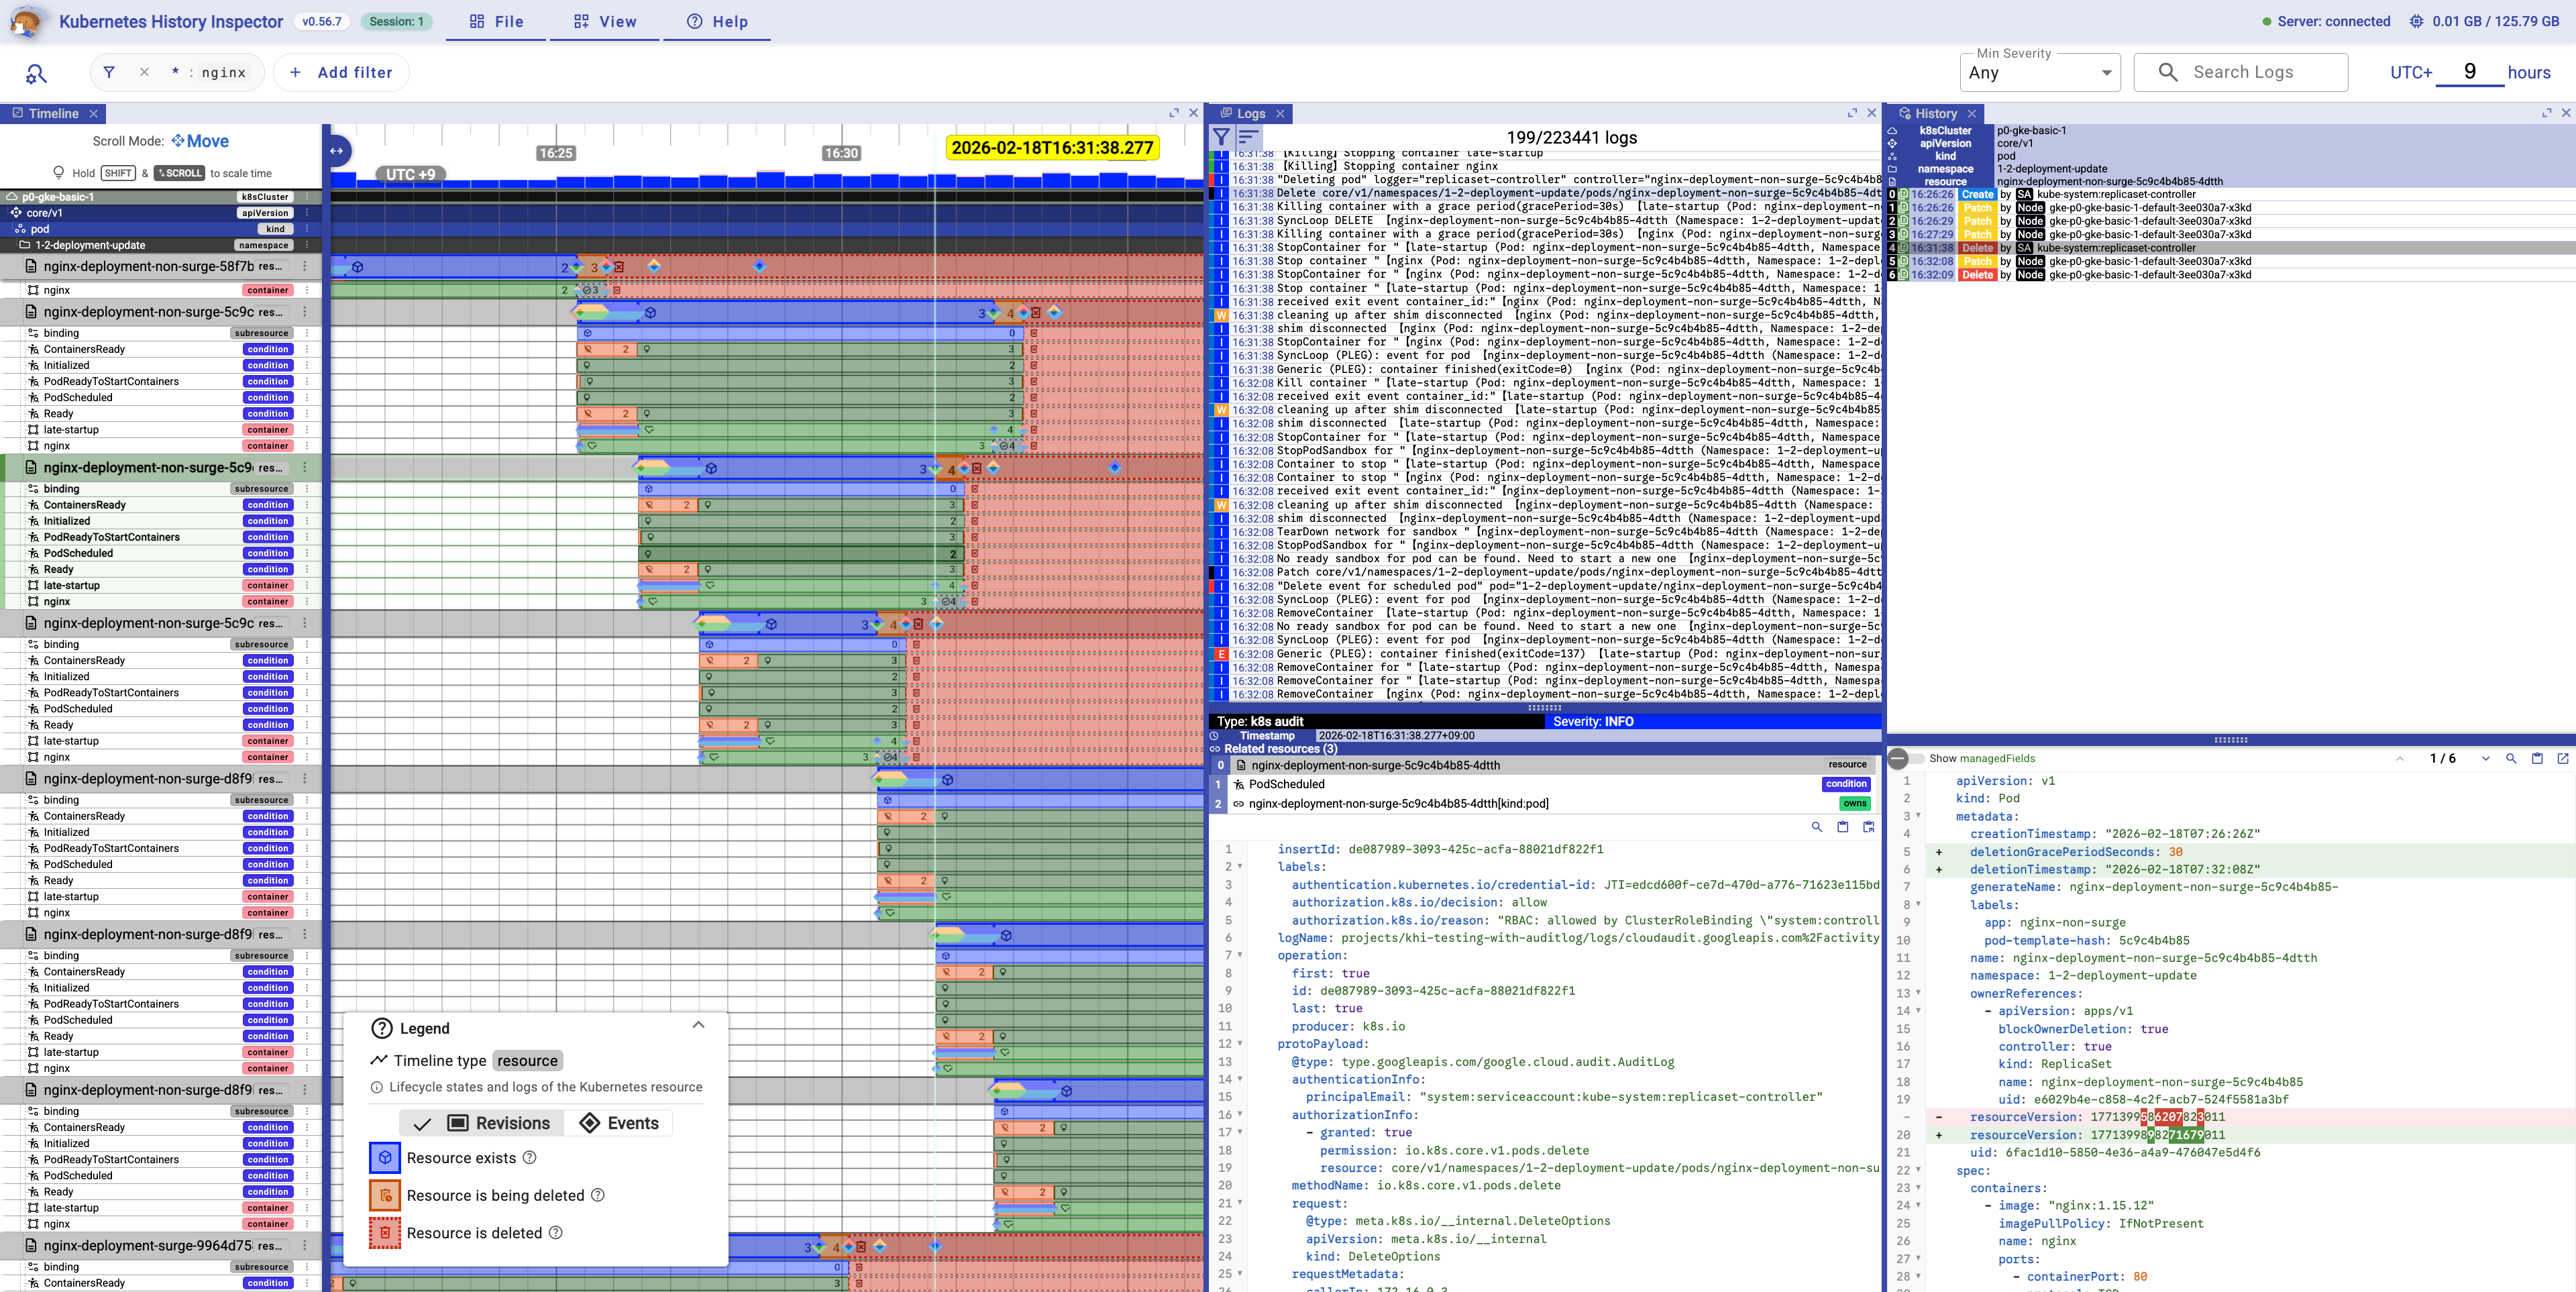
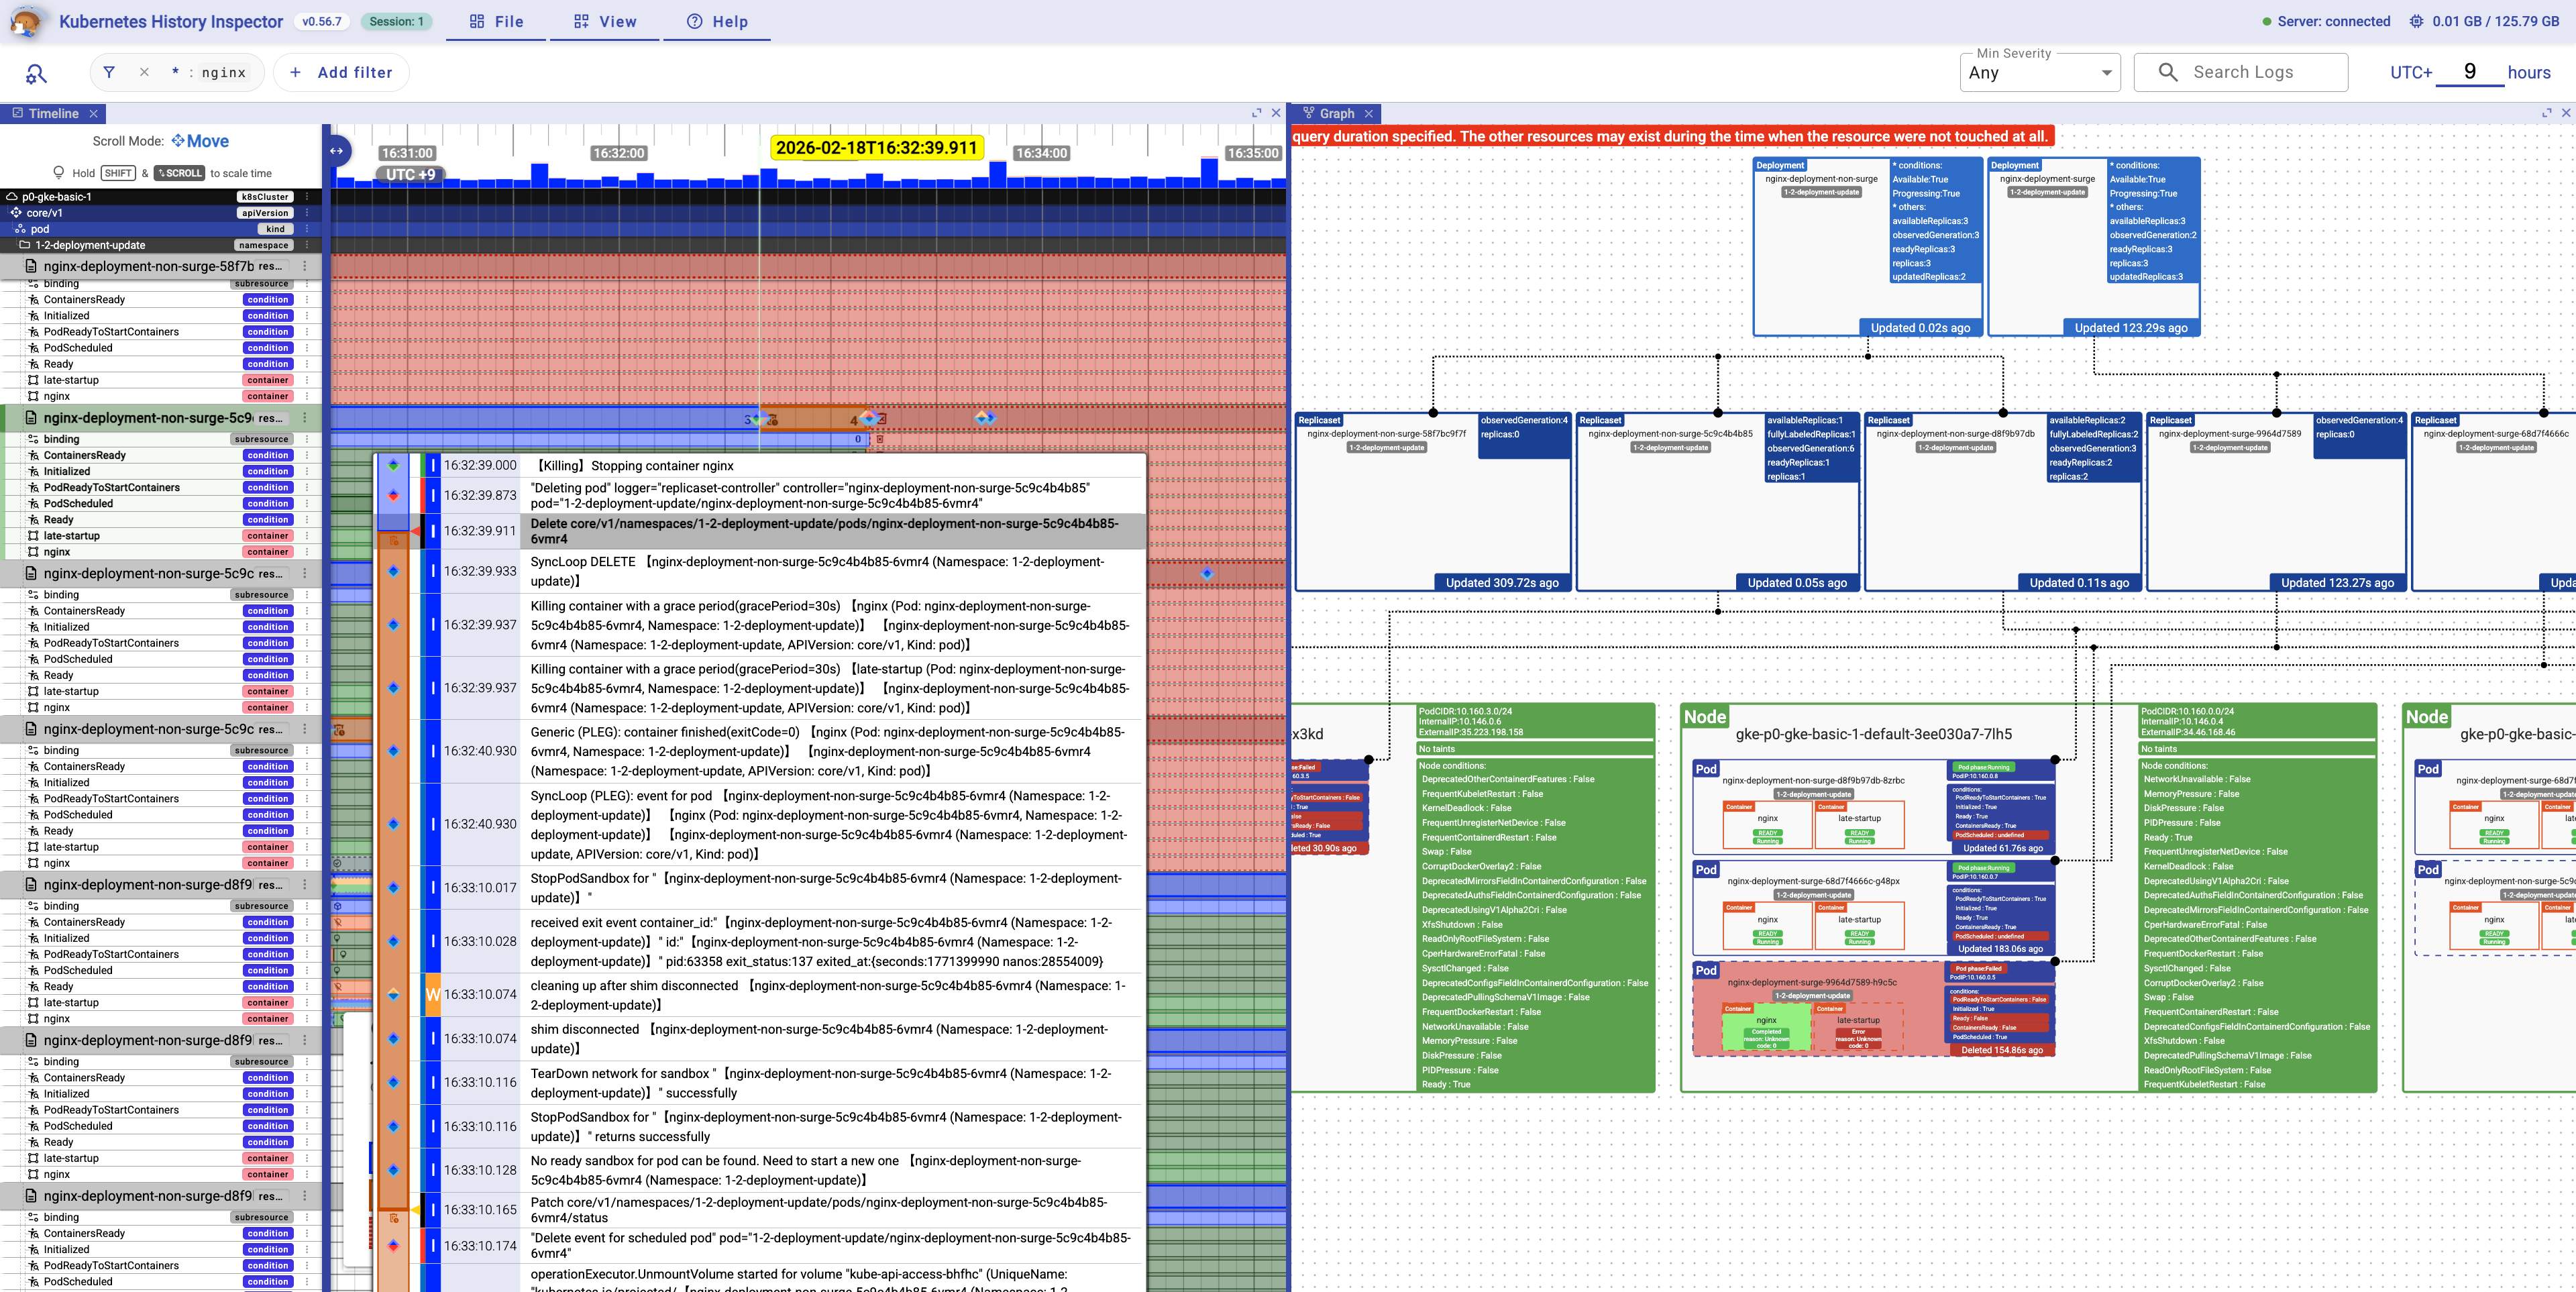
KHI is a Go application, licensed under Apache-2.0, that sits in the Kubernetes observability and troubleshooting space under Infrastructure & Operations / Monitoring & Observability. It takes large volumes of Kubernetes logs and transforms them into a single interactive timeline, so that events spread across many components can be read in one place instead of being assembled by hand. The project is agentless: nothing is installed inside the cluster, which means no DaemonSet to deploy, no sidecar to upgrade, and no cluster-side permissions to reason about beyond the log sources it reads. Its two primary surfaces are the Timeline view, which renders resource status change timings as timeline charts alongside manifest diffs taken from Kubernetes audit logs, and the Topology view, which derives relationships among Kubernetes resources solely from kube-apiserver audit logs.

The concrete problem it addresses is the reconstruction work that follows a complex incident, where the cause is spread across controllers, workloads, and the API server rather than localized in one pod. KHI consumes kube-apiserver audit logs, either as JSONlines for OSS Kubernetes clusters or through Cloud Logging for clusters on Google Cloud, and it also accepts uploaded log files. That replaces the practice of querying raw audit entries and manually ordering events to work out which resource changed first and what that change touched. Because the log source is audit data rather than application output, the view works regardless of what the workloads themselves log.

Key capabilities

  • Timeline view presents resource status change timings as timeline charts together with manifest diffs from Kubernetes audit logs.
  • Topology view maps relationships among Kubernetes resources using only kube-apiserver audit logs.
  • Agentless design, so no component runs inside the inspected cluster.
  • Accepts kube-apiserver audit logs as JSONlines for OSS Kubernetes clusters.
  • Reads Cloud Logging for all clusters on Google Cloud, and also supports log file upload.
  • Job Mode runs KHI in automated workflows such as CI/CD pipelines and alert triggers without starting the web server, documented at docs/en/setup-guide/job-mode.md.
  • Ships as the container image gcr.io/kubernetes-history-inspector/release:latest, serving its web UI on port 8080.
  • Documented support for GKE, Cloud Composer, GKE on AWS, GKE on Azure, GDCV for Baremetal, and GDCV for VMWare.

Who uses it and how

  • SRE and platform teams investigating incidents that span multiple Kubernetes components and need a single ordered picture of resource changes.
  • Google Cloud operators running GKE, Cloud Composer, GKE on AWS, GKE on Azure, GDCV for Baremetal, or GDCV for VMWare, where Cloud Logging is available as the log backend.
  • OSS Kubernetes operators who export kube-apiserver audit logs as JSONlines and use the Loki-based setup guide, uploading log files rather than connecting to a managed backend.
  • Platform and release engineers wiring KHI into CI/CD pipelines or alert triggers through Job Mode, where the web server is skipped and the tool runs as an automated step.
  • First-time evaluators using Cloud Shell, where the metadata server is present and no initial credential setup is required.

Getting started

The fastest path is Cloud Shell, where running docker run -p 127.0.0.1:8080:8080 gcr.io/kubernetes-history-inspector/release:latest starts the UI on localhost:8080. On a local PC, macOS, Linux, WSL, or Windows PowerShell, run gcloud auth application-default login and mount application_default_credentials.json into the container so Application Default Credentials are available.

How it compares

The facts provide no list of paid products that KHI replaces and name no comparable tools, so on the information given here it stands alone in this registry rather than being contrasted against a set of alternatives. What the facts do establish is its position: an agentless, audit-log-driven visualizer rather than a general log search interface, and an Apache-2.0 project that can be run locally from a public container image.

When to use it — and when not to

Self-hosters need Docker and the docker command, plus Google Cloud credentials through ADC or a reachable metadata server when Cloud Logging is the source; OSS clusters instead need kube-apiserver audit logs enabled and exported as JSONlines, since the topology view has no other input. Browser support is narrow, as KHI is tested only on the latest version of Google Chrome and is unsupported elsewhere. The README excerpt is thin and defers most operational detail to the docs tree, so anyone planning a deployment should read the setup guides and the Google Cloud permissions guide before relying on it.

project readme (upstream, from github) — read inline

Language: English | 日本語
GitHub Release PR Tests License

Kubernetes History Inspector Demo


Kubernetes History Inspector

Kubernetes History Inspector (KHI) is a rich log visualization tool for Kubernetes clusters. KHI transforms vast quantities of logs into an interactive, comprehensive timeline view. This makes it an invaluable tool for troubleshooting complex issues that span multiple components within your Kubernetes clusters. Also, KHI is agentless, allowing anyone to access its features without a complicated process.

Timeline view Topology view

Timeline view visualizes resource status change timings with timeline charts and manifest diffs from Kubernetes audit logs.

Topology view visualizes relationships among Kubernetes resources, solely from kube-apiserver audit logs.

Getting started

The easiest way to try KHI is using Cloud Shell, where the metadata server is available without requiring initial credential setup.

Running in Cloud Shell

  1. Open Cloud Shell

  2. Run the following command:

    docker run -p 127.0.0.1:8080:8080 gcr.io/kubernetes-history-inspector/release:latest
    
  3. Click the link http://localhost:8080 on the terminal and start working with KHI!

Running in environment without a metadata server (Local PC, etc.)

If you want to run KHI in an environment where the metadata server is not available, you can use Application Default Credentials (ADC) by mounting your ADC file from your host filesystem to the container.

For Linux, MacOS or WSL
gcloud auth application-default login
docker run \
 -p 127.0.0.1:8080:8080 \
 -v ~/.config/gcloud/application_default_credentials.json:/root/.config/gcloud/application_default_credentials.json:ro \
 gcr.io/kubernetes-history-inspector/release:latest
For Windows PowerShell
gcloud auth application-default login
docker run `
-p 127.0.0.1:8080:8080 `
-v $env:APPDATA\gcloud\application_default_credentials.json:/root/.config/gcloud/application_default_credentials.json:ro `
gcr.io/kubernetes-history-inspector/release:latest

Supported Products & Environments

Kubernetes cluster

Logging backend

  • Google Cloud

    • Cloud Logging (For all clusters on Google Cloud)
  • Other

Supported environment

  • Latest Google Chrome
  • docker command

[!IMPORTANT] We only test KHI on the latest version of Google Chrome. KHI may work with other browsers, but we do not provide support if it does not.

Environment Setup Guide

Google Cloud

Read Google Cloud Permissions & Configuration Guide.

OSS Kubernetes

Read Using KHI with OSS Kubernetes Clusters - Example with Loki.

User Guide

Please refer to the User Guide for detailed usage.

Development Contribution Guide

If you'd like to contribute to the project KHI, read Contribution Guide and then follow Development Guide

Disclaimer

Please note that this tool is not an officially supported Google Cloud product. If you find any issues and have a feature request, file a Github issue on this repository and we are happy to check them on best-effort basis.

[!IMPORTANT] Do not expose KHI port on the internet. KHI itself is not providing any authentication or authorization features and KHI is intended to be accessed from its local user.

Frequently asked questions

Is khi free to use?

khi is open source under the Apache-2.0 licence. There is no licence fee and no seat count — you can self-host it or, where the project offers one, pay a vendor for a managed version instead.

What does khi do?

A log viewer for Kubernetes troubleshooting

What is khi written in?

khi is primarily written in Go. Its source is publicly available at https://github.com/GoogleCloudPlatform/khi, and it has 2,087 GitHub stars.