brutespray is a free, open source threat detection & response project written in Go and released under MIT. It has 2,542 GitHub stars, 438 forks and 14 open issues, and was last pushed 17 hours ago. On this registry it ranks #34 of 54 tracked projects in Threat Detection & Response, with 5 head-to-head comparisons available.

What is brutespray?

Brutespray is a fast, multi-protocol credential brute-forcer for penetration testers and red teams that automatically tests default and custom credentials across dozens of services directly from scanner output.

What it is

Brutespray is a command-line security tool written in Go, created by Shane Young (@x90sky) and Jacob Robles (@shellfail) and inspired by Leon Johnson (@sho-luv). It lives in the offensive-security and network-security ecosystem alongside tools such as Nmap, Nessus, and Nexpose, and it ships as a single static binary (version 2.7.2) under the MIT licence with an interactive terminal UI, embedded wordlists, and checkpoint-based resume support.

The concrete problem it solves is the manual translation between service discovery and credential testing. Rather than reading scan results by hand and invoking a separate attacker for each host, you feed Brutespray your existing scan output in Nmap GNMAP/XML, Nessus, Nexpose, JSON, or plain list format, and it parses the discovered services itself and attacks them in parallel across 40+ protocols. It replaces the repeated, per-service invocation of individual brute-force tools with one pass over a scan file, targeting the exact host, port, and service combination that was actually observed.

Key capabilities

  • Imports Nmap GNMAP/XML, Nessus, Nexpose, JSON, and plain list formats, and can also be fed over pipeline stdin from tools such as naabu, fingerprintx, and masscan.
  • Brute-forces 41 services including ssh, ftp, telnet, smtp, imap, pop3, mysql, postgres, mssql, mongodb, redis, vnc, snmp, smbnt, rdp, http, ldap, winrm, and oracle.
  • Runs a lockout-aware password spray mode with configurable delays, alongside standard parallel credential attempts with dynamic threading, a circuit breaker, and rate limiting.
  • Supports HTTP Basic/Digest/NTLM (auto and forced modes), SMTP PLAIN/LOGIN, IMAP/POP3 SASL, and SMB pass-the-hash, with per-module settings passed via -m KEY:VALUE.
  • Provides an interactive TUI with tabbed Findings and live settings views, plus pause-and-resume of individual hosts, and Ctrl+C checkpointing that can be resumed later.
  • Emits summary reports as JSON, CSV, Metasploit RC, and NetExec scripts, with per-attempt JSONL output.
  • Ships embedded wordlists compiled into the binary through a layered manifest system, and routes traffic through a SOCKS5 proxy with authentication.

Who uses it and how

  • Penetration testers who have already run an Nmap, Nessus, or Nexpose engagement feed the saved scan file straight into brutespray -f nmap.gnmap -u admin -p password to test every discovered service in one pass.
  • Red-team operators working through a CIDR range use invocations such as -H ssh://10.1.1.0/24:22 -u root -p passlist.txt, or supply combo credentials with -C root:root for known username/password pairs.
  • Assessments against environments with account lockout policies run the spray mode with configured delays rather than unrestricted parallel attempts.
  • Operators working through proxies route attempts through an authenticated SOCKS5 proxy, and long engagements interrupt with Ctrl+C and resume from the checkpoint rather than restarting.
  • Teams standardising output import results into Metasploit RC files or NetExec scripts for follow-on tooling.

Getting started

Install it with go install github.com/x90skysn3k/brutespray/v2@latest, or use the release binaries and the Docker instructions documented in docs/installation.md.

How it compares

Brutespray sits alongside hydra, medusa, ncrack, and brutus as a service-credential attacker, but it differs on the workflow features those tools document as absent: a single static binary with an interactive TUI, checkpoint/resume, lockout-aware spray mode, per-attempt JSONL output, and import from Nmap GNMAP/XML, Nessus, and Nexpose. Its 41 supported services sit below hydra's 50+ but above medusa (34), ncrack (14), and brutus (23), and the README notes that competing tools change quickly and that comparison symbols reflect documented behaviour at PR time.

When to use it — and when not

It suits operators who already have scanner output and want one binary to turn it into credential tests, particularly where checkpointing, spraying, and proxy support matter. It is the wrong choice if you need coverage of services outside its 41 supported protocols — hydra supports more — and note that the project carries 14 open issues, so expect some rough edges rather than a fully polished tool.

project readme (upstream, from github) — read inline

Brutespray

Version goreleaser Go Report Card GitHub stars

Created by: Shane Young/@x90sky && Jacob Robles/@shellfail

Inspired by: Leon Johnson/@sho-luv

Description

Brutespray automatically attempts default credentials on discovered services. It takes scan output from Nmap (GNMAP/XML), Nessus, Nexpose, JSON, and lists, then brute-forces credentials across 40+ protocols in parallel. Built in Go with an interactive terminal UI, embedded wordlists, and resume capability.

Quick Install

go install github.com/x90skysn3k/brutespray/v2@latest

Release Binaries | Build from Source | Docker

Quick Start

# From Nmap scan output
brutespray -f nmap.gnmap -u admin -p password

# Target a specific host
brutespray -H ssh://192.168.1.1:22 -u admin -p passlist.txt

# CIDR range
brutespray -H ssh://10.1.1.0/24:22 -u root -p passlist.txt

# Combo credentials
brutespray -H ssh://10.0.0.1:22 -C root:root

See all examples for more usage patterns.

Demo
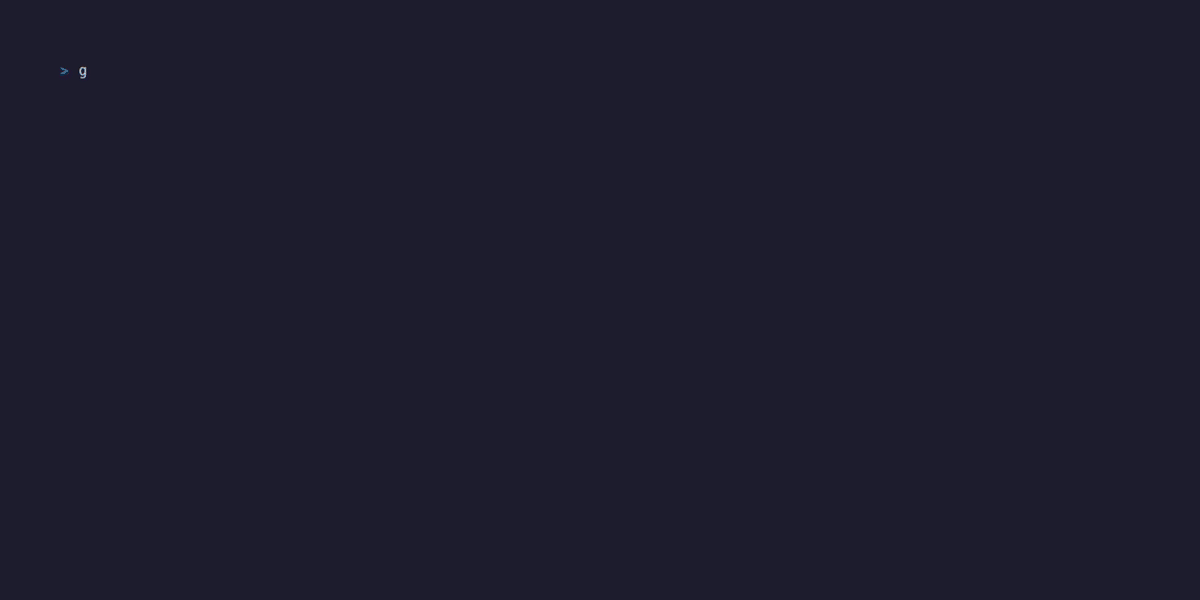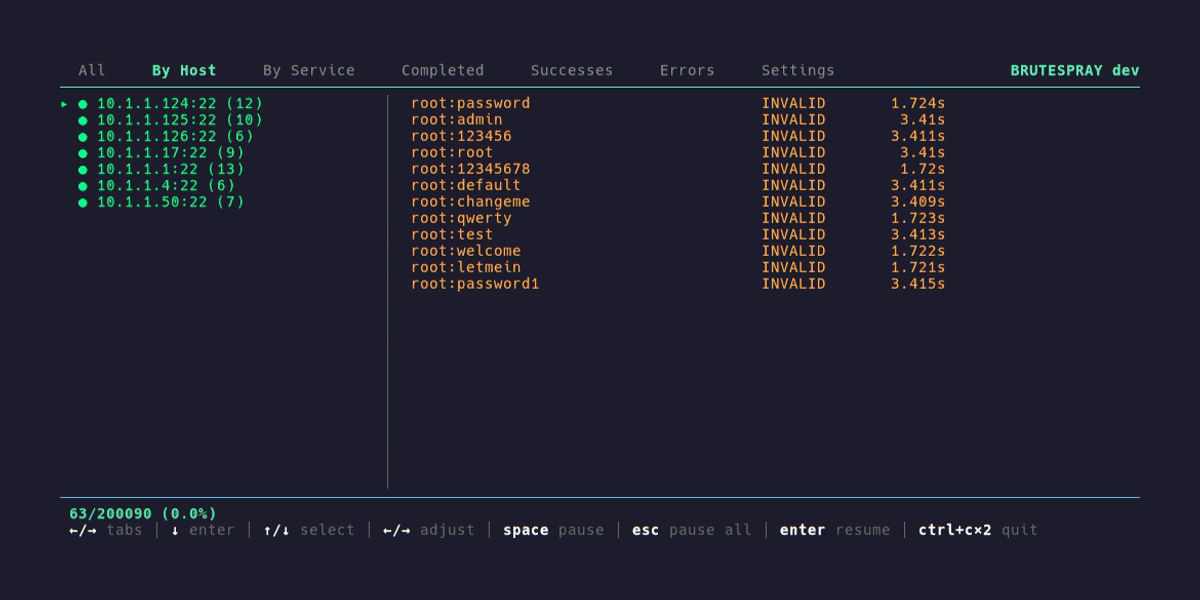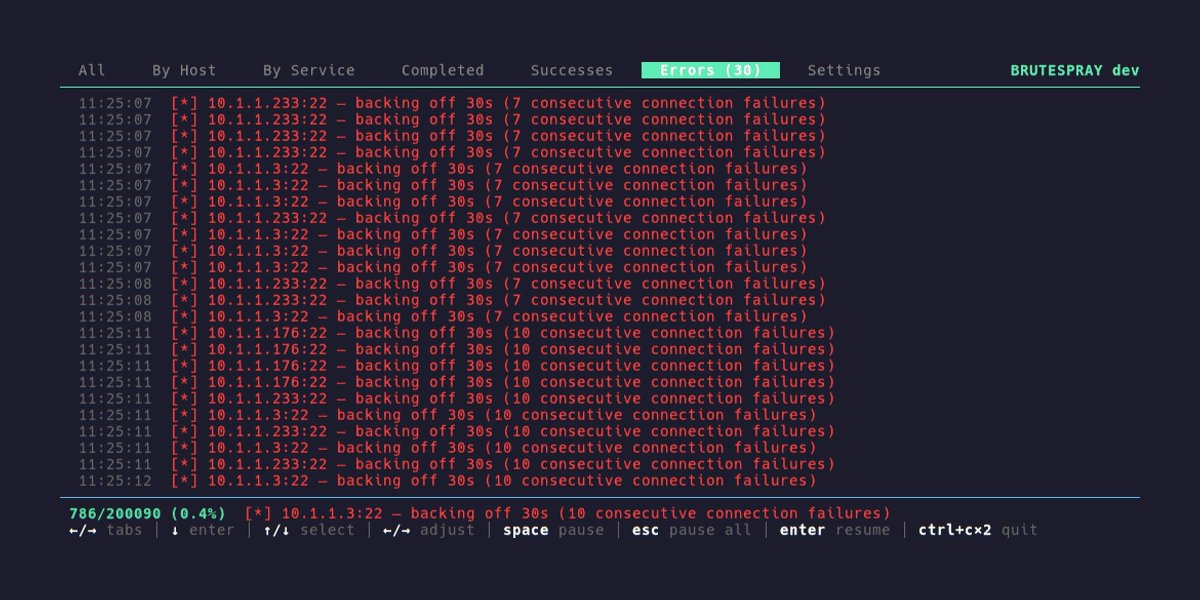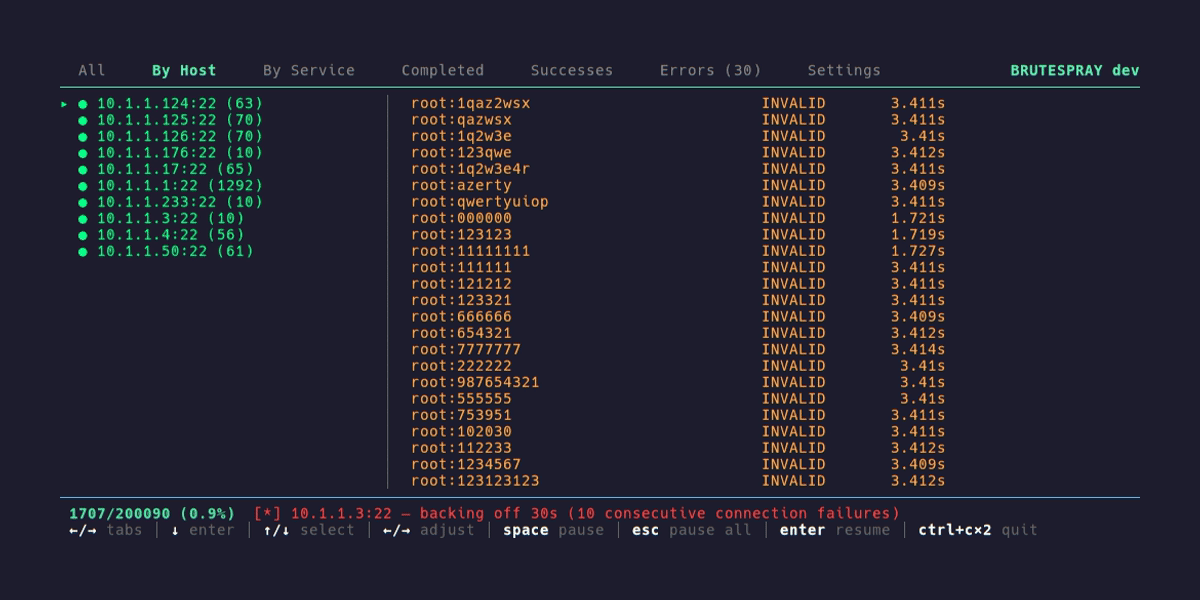
Features

  • 40+ protocols — SSH, FTP, RDP, SMB, MySQL, PostgreSQL, Redis, LDAP, WinRM, and more
  • Module parameters — Per-module settings via -m KEY:VALUE (auth type, target path, NTLM domain, etc.)
  • Multi-auth support — HTTP Basic/Digest/NTLM auto/forced modes, SMTP PLAIN/LOGIN, IMAP/POP3 SASL, SMB pass-the-hash
  • Interactive TUI — Tabbed views including Findings, live settings, pause/resume hosts (details)
  • Multiple input formats — Nmap GNMAP/XML, Nessus, Nexpose, JSON, lists (details)
  • Password spray mode — Lockout-aware spraying with configurable delays (details)
  • SOCKS5 proxy — Full proxy support with authentication (details)
  • Resume & checkpoint — Interrupt with Ctrl+C, resume later (details)
  • Embedded wordlists — Layered manifest system compiled into the binary (details)
  • Summary reports — JSON, CSV, Metasploit RC, NetExec scripts (details)
  • Performance tuning — Dynamic threading, circuit breaker, rate limiting (details)
  • YAML config files — Per-engagement settings (details)

How Brutespray Compares

Feature brutespray hydra medusa ncrack brutus
Single static binary ✅ ❌ ❌ ❌ ✅
Interactive TUI ✅ ❌ ❌ ❌ ❌
Checkpoint / resume ✅ ❌ ❌ ✅ ❌
Spray mode (lockout-aware) ✅ ❌ ❌ ❌ ❌
Per-attempt JSONL output ✅ ⚠️ ❌ ❌ ❌ (success-only)
SOCKS5 + proxy rotation ✅ ⚠️ ❌ ❌ ❌
Embedded SSH bad-keys (CVE-tagged) ✅ ❌ ❌ ❌ ✅
Pipeline stdin (naabu / fingerprintx / masscan) ✅ ❌ ❌ ❌ ✅
Pre-auth RDP recon (NLA / sticky-keys) ✅ ❌ ❌ ❌ ✅
Nmap gnmap + XML / Nessus / Nexpose import ✅ ⚠️ ❌ ❌ ⚠️ (nmap only)
Per-module params (-m KEY:VAL) ✅ ❌ ❌ ❌ partial
Service count 41 50+ 34 14 23

Symbols reflect documented behavior at PR time. Competing tools change quickly.

Supported Services

ssh ftp ftps telnet smtp smtp-vrfy imap pop3 mysql postgres mssql mongodb redis vnc snmp smbnt rdp http https vmauthd teamspeak asterisk nntp oracle xmpp ldap ldaps winrm rexec rlogin rsh wrapper

Full details and service-specific notes: docs/services.md

Print discovered services from a scan file with -P -q:

Documentation

Guide Description
Installation Go install, release binaries, build from source, Docker
Usage CLI flags, config files, input formats
Services All 40+ protocols with ports, status, and notes
Examples Common usage patterns and recipes
Interactive TUI Keybindings, tabs, Findings, live settings
Advanced Spray mode, proxy, resume, performance tuning
Wordlists Manifest system, layers, overrides, customization
Output & Reporting Summary reports, Metasploit/NetExec integration

Star History

Star history

Frequently asked questions

Is brutespray free to use?

brutespray is open source under the MIT licence. There is no licence fee and no seat count — you can self-host it or, where the project offers one, pay a vendor for a managed version instead.

What does brutespray do?

Fast, multi-protocol credential brute-forcer. Parses Nmap, Nessus, and Nexpose output to automatically test default and custom credentials across 30+ protocols.

What is brutespray written in?

brutespray is primarily written in Go. Its source is publicly available at https://github.com/x90skysn3k/brutespray, and it has 2,542 GitHub stars.