authelia is a free, open source identity & access management (iam) project written in Go and released under Apache-2.0. It has 29,482 GitHub stars, 1,531 forks and 137 open issues, and was last pushed 11 hours ago. On this registry it ranks #4 of 70 tracked projects in Identity & Access Management (IAM), with 5 head-to-head comparisons available. It gained 337 stars over the last 30 tracked days.

What is authelia?

Authelia is an open-source authentication and authorization server written in Go that provides single sign-on and multi-factor authentication for web applications through a web portal, aimed at self-hosters and platform teams who need to protect services sitting behind a reverse proxy.

What it is

Authelia is an authentication and authorization server that acts as a companion for reverse proxies. Rather than authenticating users inside each application, it sits in front of them and allows, denies, or redirects requests, presenting a web portal where users complete login and second-factor challenges. It is written in Go, licensed under Apache-2.0, and distributed both as a standalone service and as a container. The project lives in the cloud-native and self-hosting ecosystem, with first-class integrations for Docker and Kubernetes and out-of-the-box compatibility with Traefik and Caddy.

The concrete problem it solves is the fragmentation of authentication across a fleet of self-hosted or internally hosted web applications. Instead of each service carrying its own login, session, and second-factor logic, Authelia centralizes that responsibility and delegates the decision to the proxy in front of the app. It also exposes OpenID Connect 1.0 and OAuth 2.0 so that applications can consume it as an identity provider directly. The result is one portal, one set of access rules, and one place to enforce second factors across every protected endpoint.

Key capabilities

  • OpenID Connect 1.0 and OAuth 2.0 provider, OpenID Certified™ for the Basic OP, Implicit OP, Hybrid OP, Form Post OP, and Config OP profiles.
  • Post-Quantum Cryptography readiness.
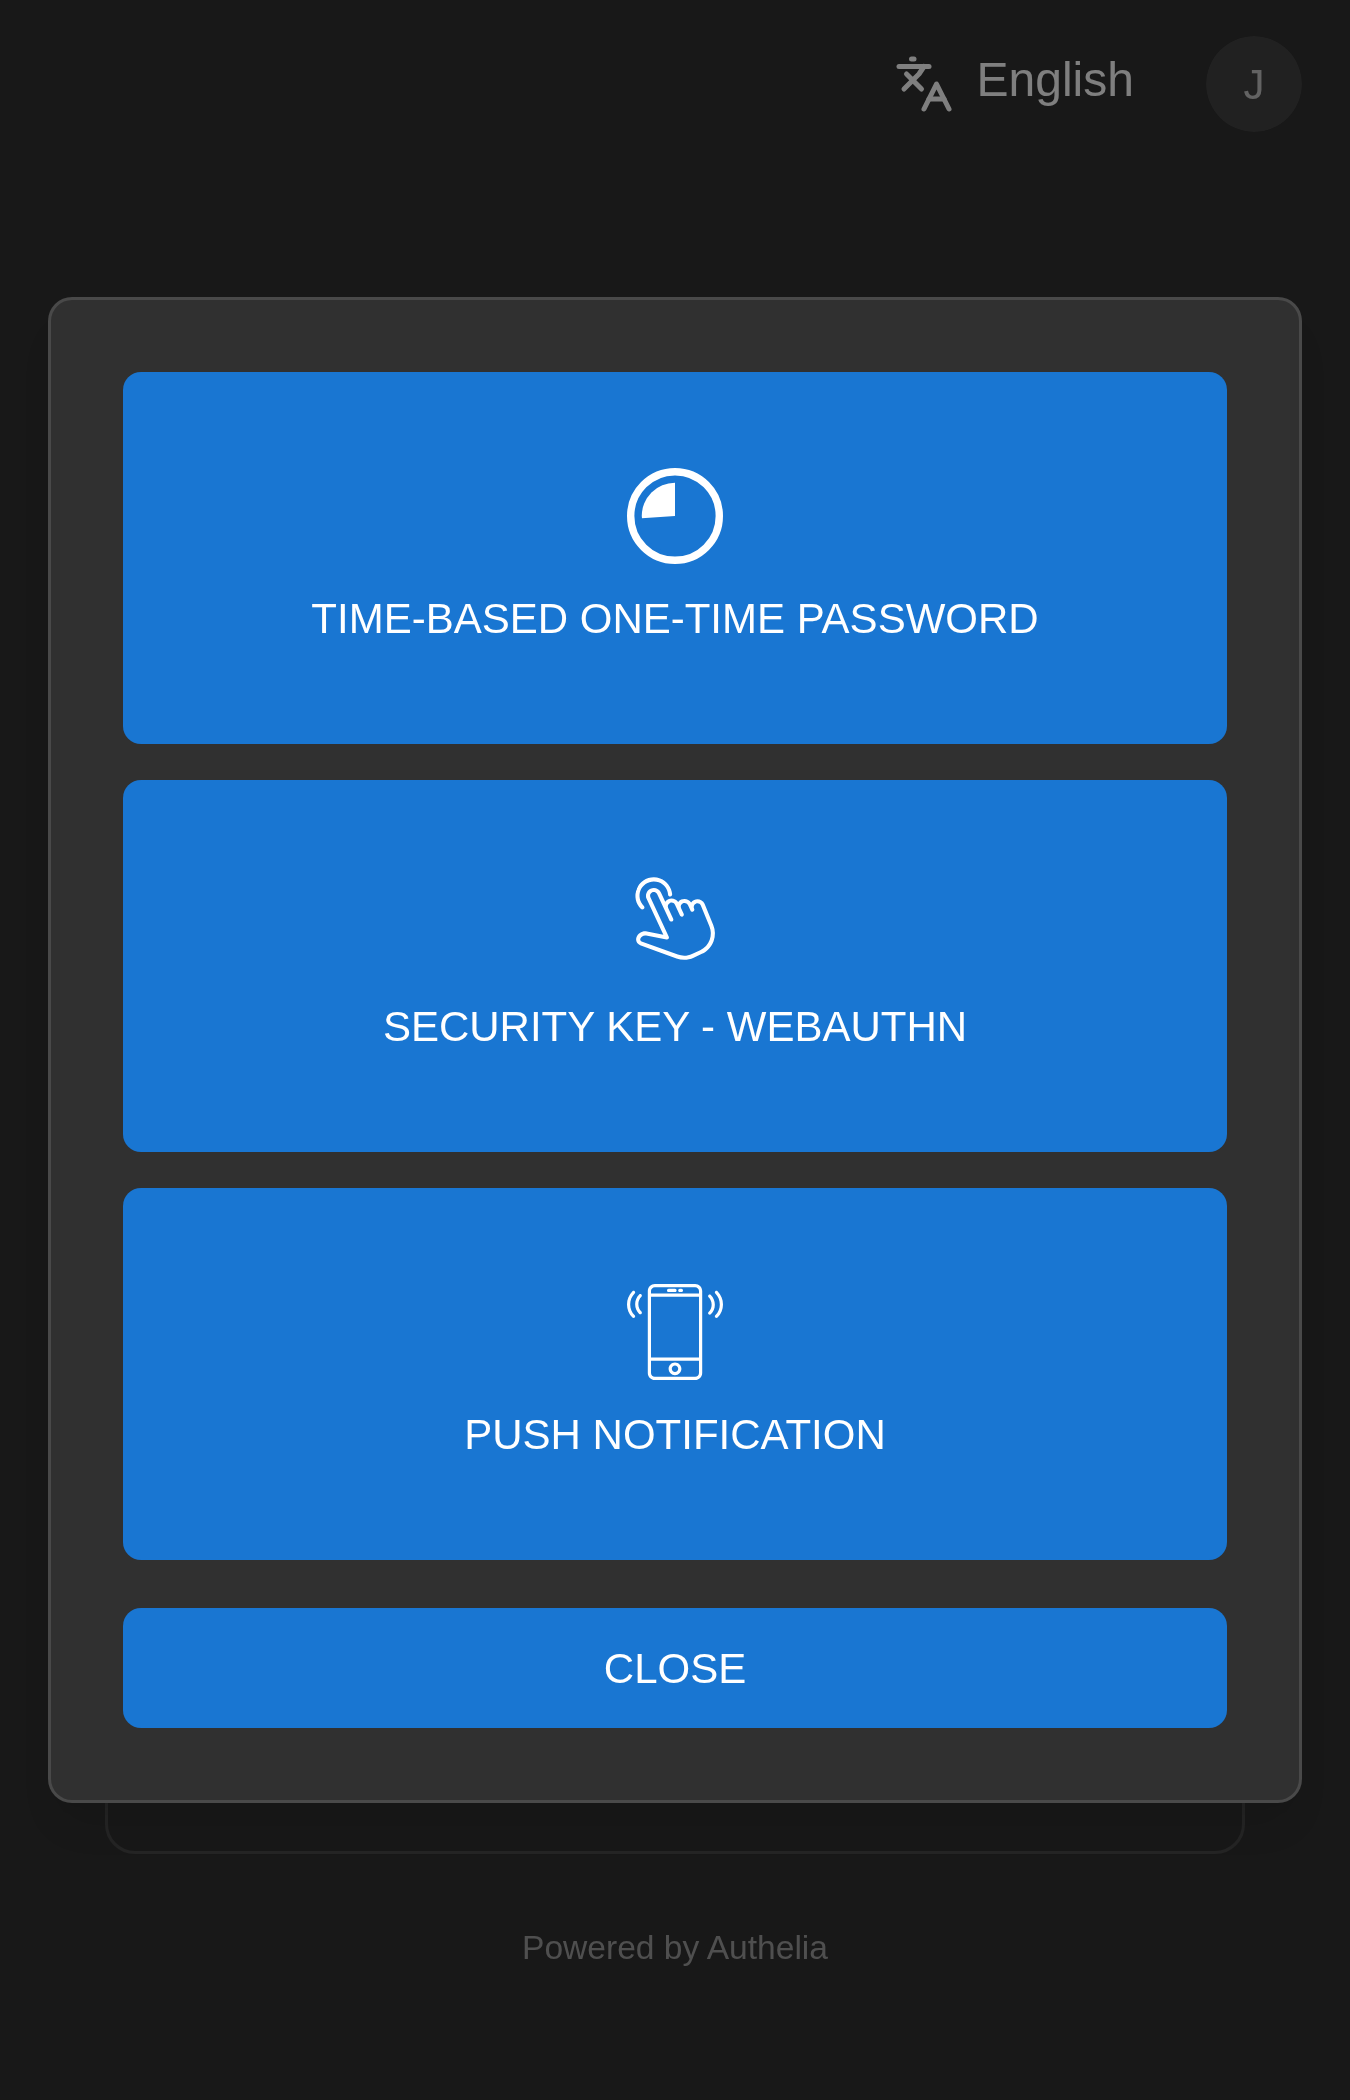
  • Multiple second factors: FIDO2 WebAuthn security keys such as a YubiKey, Time-based One-Time passwords, and Mobile Push Notifications via Duo.
  • Passwordless authentication using WebAuthn passkeys.
  • Fine-grained access control rules matching subdomain, user, user group membership, request URI, request method, and network, with a choice between one-factor and two-factor policy per rule.
  • Access restriction after too many invalid authentication attempts, plus password reset with identity verification by email confirmation.
  • High availability through a remote database and Redis as a highly available key-value store, and native proxy integration via Traefik ForwardAuth and the Caddy forward_auth directive.

Who uses it and how

  • Self-hosters running a reverse proxy in front of multiple services, who want a single login and second-factor prompt instead of per-application credentials.
  • Users of the LinuxServer SWAG container, which ships curated Authelia configuration alongside a published setup guide.
  • Kubernetes operators deploying through ingress-nginx, the Traefik Kubernetes CRD or Ingress, Istio, or Envoy Gateway, with Helm chart installation available in beta.
  • Teams already standardized on Duo who want mobile push approval as their second factor.
  • Organizations that need basic authentication preserved for endpoints governed by a one-factor rule while applying two-factor policy elsewhere.

Getting started

Install as a standalone service from the AUR, APT, or FreeBSD Ports, or use a static binary or .deb package from the releases page. Container deployment is available on Docker and Kubernetes, with orchestration via the Helm chart in beta.

How it compares

No comparable single sign-on or identity provider tools are named in the facts provided here, so no direct product comparison can be made. Among the integrations the project does name, it occupies a distinct position: it is not a reverse proxy like Traefik or Caddy, and not a second-factor vendor like Duo, but the authentication layer that sits between them. On that basis it stands alone in this registry.

When to use it — and when not to

A self-hoster must operate supporting infrastructure: a remote database and Redis are required for the highly available configuration, and password reset with identity verification depends on outbound email confirmation. Anyone unwilling to run and maintain a database, a key-value store, and mail delivery alongside the authentication server itself should look elsewhere. Note also that the OpenID Connect offering, the Helm chart, and the Kubernetes integration paths are all described as beta, so teams requiring only generally available components should weigh that before adopting.

project readme (upstream, from github) — read inline

Build Codecov OpenSSF Best Practices OpenSSF Scorecard SLSA 3 License Sponsor

GitHub Release Docker Tag Docker Size Docker Pulls AUR source version AUR binary version AUR development version

Discord Matrix

Authelia is an open-source authentication and authorization server providing two-factor authentication and single sign-on (SSO) for your applications via a web portal. It acts as a companion for reverse proxies by allowing, denying, or redirecting requests.

Documentation is available at https://www.authelia.com/.

The following is a simple diagram of the architecture:
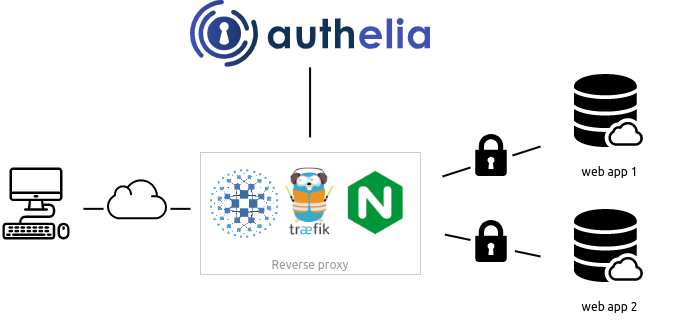
Authelia can be installed as a standalone service from the AUR, APT, FreeBSD Ports, or using a static binary, .deb package, as a container on [Docker] or [Kubernetes].

Deployment can be orchestrated via the Helm Chart (beta) leveraging ingress controllers and ingress configurations.
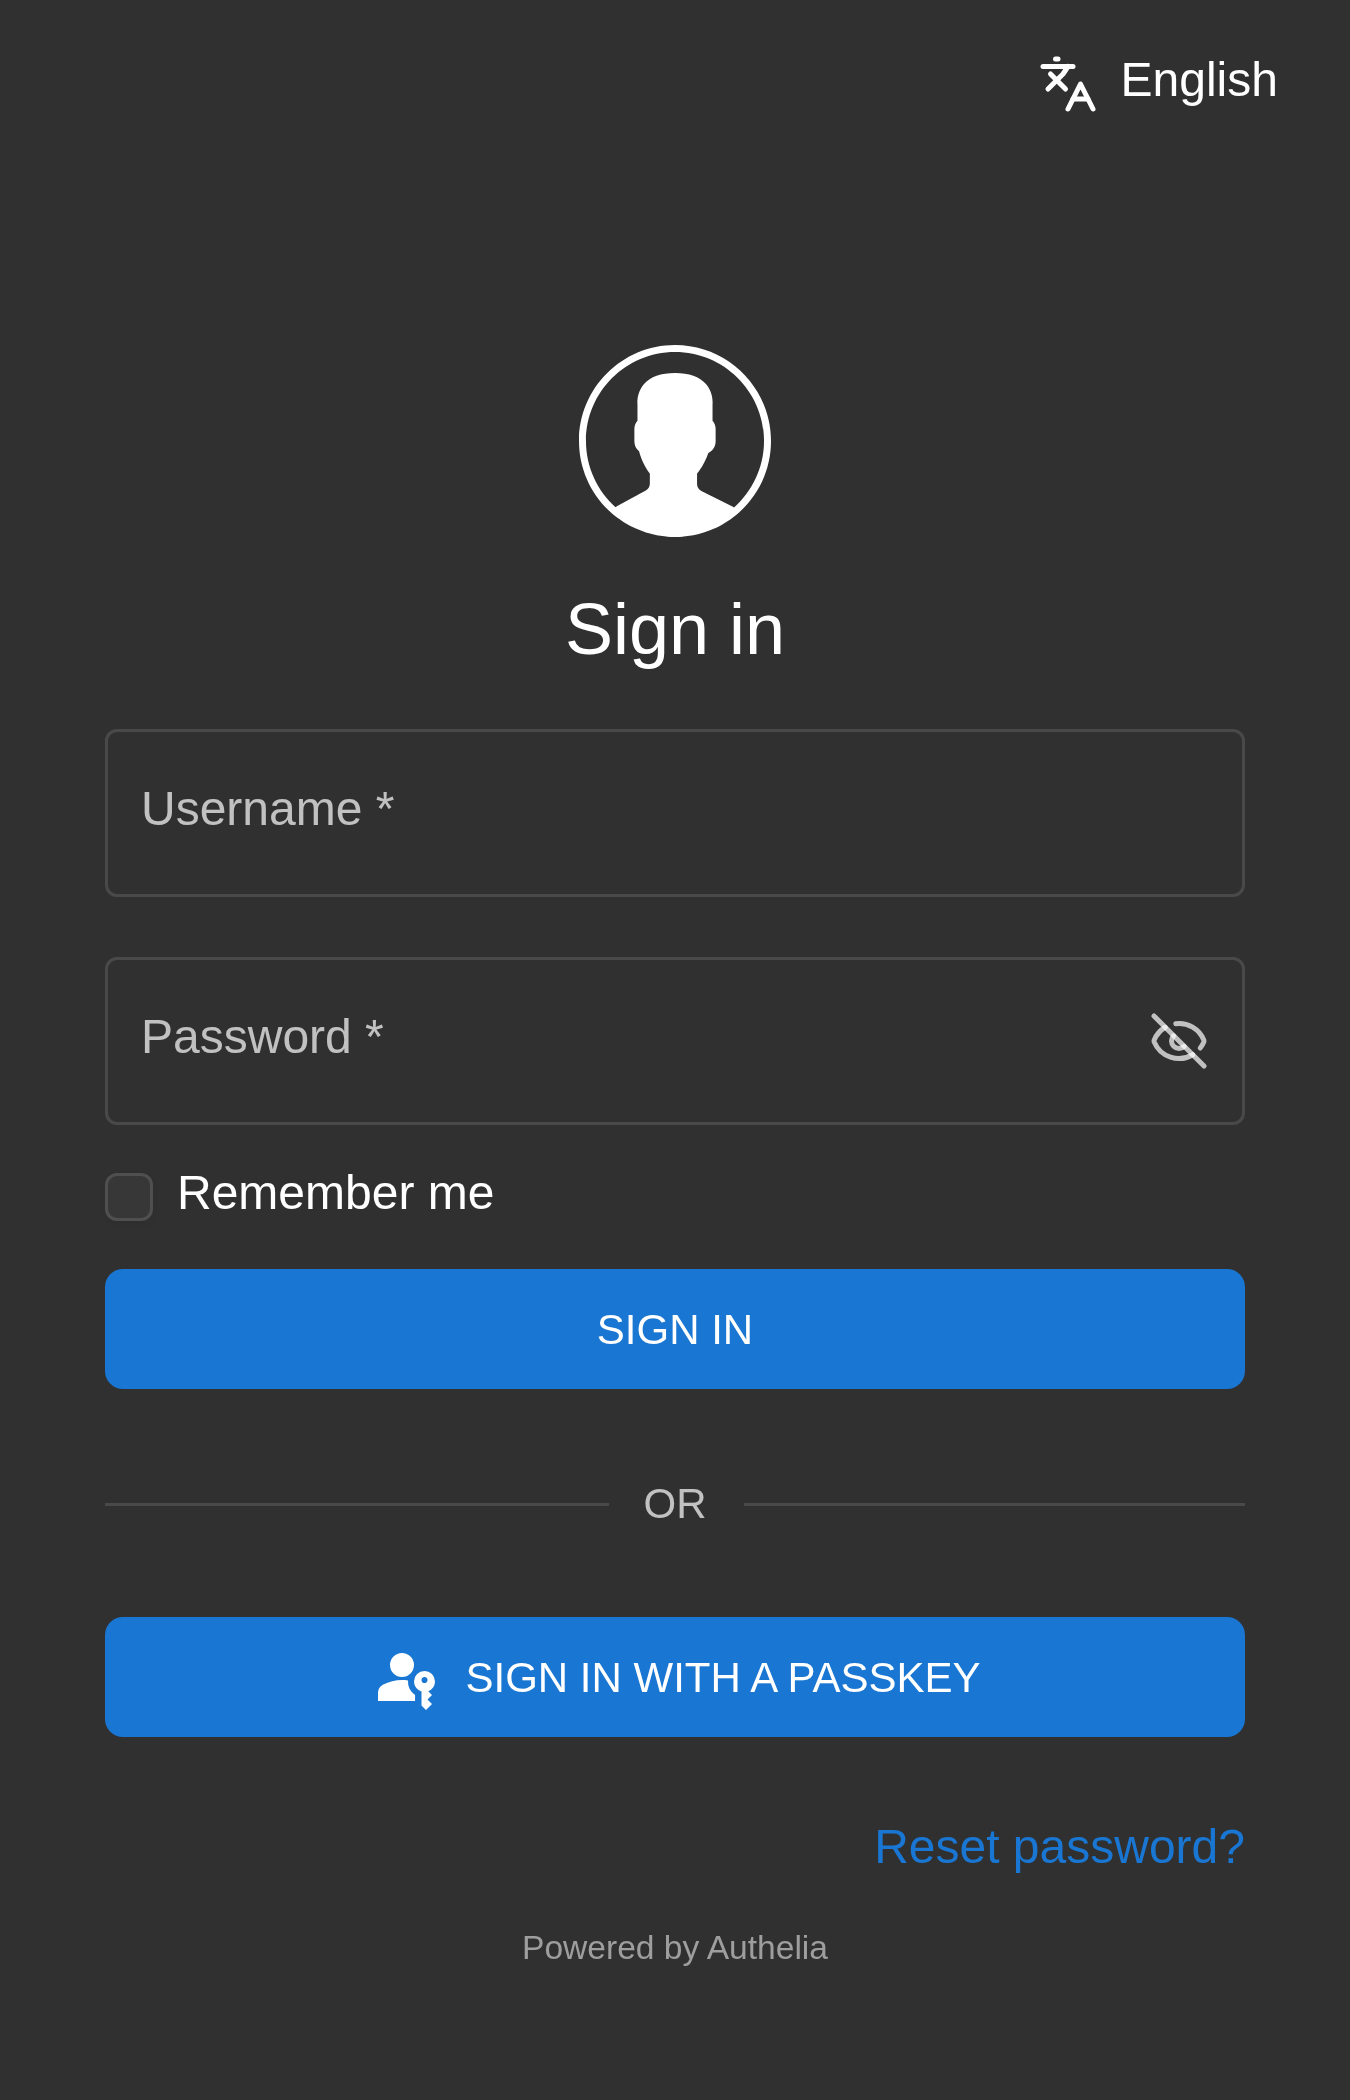
Here is what Authelia's portal looks like:
Features summary

This is a list of the key features of Authelia:

  • OpenID Connect 1.0 / OAuth 2.0
  • Post-Quantum Cryptography
  • Several second factor methods:
  • Passwordless Authentication via WebAuthn (Passkeys)
  • Password reset with identity verification using email confirmation.
  • Access restriction after too many invalid authentication attempts.
  • Fine-grained access control using rules which match criteria like subdomain, user, user group membership, request uri, request method, and network.
  • Choice between one-factor and two-factor policies per-rule.
  • Support of basic authentication for endpoints protected by the one-factor policy.
  • Highly available using a remote database and Redis as a highly available KV store.
  • Compatible with Traefik out of the box using the ForwardAuth middleware.
  • Curated configuration from LinuxServer via their SWAG container as well as a guide.
  • Compatible with [Caddy] using the forward_auth directive.
  • Kubernetes Support:

For more details take a look at the Overview.

If you want to know more about the roadmap, follow Roadmap.

OpenID Connect 1.0 / OAuth 2.0

Authelia is [OpenID Certified™] to the Basic OP / Implicit OP / Hybrid OP / Form Post OP / Config OP profiles of the [OpenID Connect™ protocol]. While this offering is still effectively on the roadmap as a beta it's very comprehensive and well implemented already, also allowing us comprehensive certification. Read more about the [OpenID Certified™] status of Authelia in the OpenID Connect 1.0 Integration Guide.
</a>

Proxy support

Authelia works in combination with [nginx], [Traefik], [Caddy], [Skipper], [Envoy], or [HAProxy].
Getting Started

See the Get Started Guide or one of the curated examples below.

docker compose

The docker compose bundles act as a starting point for anyone wanting to see Authelia in action. You will have to customize them to your needs as they come with self-signed certificates.

Local

The Local compose bundle is intended to test Authelia without worrying about configuration. It's meant to be used for scenarios where the server is not be exposed to the internet. Domains will be defined in the local hosts file and self-signed certificates will be utilized.

Lite

The Lite compose bundle is intended for scenarios where the server will be exposed to the internet, domains and DNS will need to be setup accordingly and certificates will be generated through LetsEncrypt. The Lite element refers to minimal external dependencies; File based user storage, SQLite based configuration storage. In this configuration, the service will not scale well.

Deployment

Now that you have tested Authelia and you want to try it out in your own infrastructure, you can learn how to deploy and use it with Deployment. This guide will show you how to deploy it on bare metal as well as on Kubernetes.

Security

Authelia takes security very seriously. If you discover a vulnerability in Authelia, please see our Security Policy.

For more information about security related matters, please read the documentation.

Contact Options

Several contact options exist for our community, the primary one being Matrix. These are in addition to GitHub issues for creating a new issue.

Matrix

Community members are invited to join the Matrix Space which includes both the Support Room and the Contributing Room.

  • The core team members are identified as administrators in the Space and individual Rooms.
  • All channels are linked to Discord.

Discord

Community members are invited to join the Discord Server.

  • The core team members are identified by the CORE TEAM role in Discord.
  • The [#support] and [#contributing] channels are linked to Matrix.

Email

You can contact the core team by email via team@authelia.com. Please note the security@authelia.com is also available but is strictly reserved for [security] related matters.

Breaking changes

Since Authelia is still under active development, it is subject to breaking changes. It's recommended to pin a version tag instead of using the latest tag and reading the release notes before upgrading. This is where you will find information about breaking changes and what you should do to overcome said changes.

Why Open Source?

You might wonder why Authelia is open source while it adds a great deal of security and user experience to your infrastructure at zero cost. It is open source because we firmly believe that security should be available for all to benefit in the face of the battlefield which is the Internet, with near zero effort.

Additionally, keeping the code open source is a way to leave it auditable by anyone who is willing to contribute. This way, you can be confident that the product remains secure and does not act maliciously.

It's important to keep in mind Authelia is not directly exposed on the Internet (your reverse proxies are) however, it's still the control plane for your internal security so take care of it!

Contribute

If you want to contribute to Authelia, please read our contribution guidelines.

Authelia exists thanks to all the people who contribute so don't be shy, come chat with us on either Matrix or Discord and start contributing too.

Thanks goes to these 96 wonderful people (emoji key)
Clément Michaud Amir Zarrinkafsh James Elliott Antoine Favre BankaiNoJutsu Callan Bryant Ian FrozenDragoon vdot0x23 Sohalt Stoica Tedy Dylan Smith Philipp Staiger Paul Williams akusei Dustin Sweigart Shawn Haggard SootySec Valentin Höbel Mike Kusold TheCatLady Lauri Võsandi Kennard Vermeiren ThinkChaos Hasan Marcel Marquardt Jon B. Alex Gustafsson Arsenović Arsen dakriy Dave yossbg Justin Sievenpiper Andrew Moore Manuel Nuñez protvis74 Jamie (Bear) Murphy Robin van Boven alphabet5 Robert Meredith Adrian Gąsior James White Auzborn123 SvanGlan andreas-berg Michał Mieszczak Stephen Kent levkoburburas Josh Gordon silasfrancisco Ricardo Pesqueira Brynn Crowley Hendrik Sievers Wang Weixuan Pierre Kisters peter Nick O'Connor Nikita Pedorich Andre Toerien erusc Kevin Cox Br1an deprrous Ricardo Rivera RDW Justin Mike Dominik Schmidt Shihta Kuan Toshaan Bharvani haowei Eng Zer Jun MBM Paul Calabro guoguangwu Webysther Sperandio Jacquet Corentin Michael Stapelberg fbird Dan curlwget DCsunset Jonas Geiler oliverpool tcx4c70 feinedsquirrel GeistFighter GuiPoM Michel Heusschen bishtawi billcarsoon rowanarts Christian Franzl Yaroslav Halchenko Riccardo Padovani TowyTowy
📖 Documentation Overlords
and these 226 wonderful people who keep the documentation worth reading

Philipp Rintz somebody-somewhere-over-the-rainbow Lukas Klass James Hodgkinson Chris Smith Mihály Bereczki Silver Bullet Timo Andrew Kliskey Kristof Mattei ZMiguel Valdiviesso Daniel Miller Kevyn Bruyere Max Victor Chris Whisker nasatome Begley Brothers (Development) Dimitris Zervas David Chidell Ian Gallagher Wu Han lavih Nicolas Reymundo polandy Michael Campbell Aram Akhavan Shadow Patrick Ruckstuhl Dennis Gaida Alestrix bgh-github Zhao Xiang Lim HannesJo0139 Clément Radenac boomam Northguy Brennan Kinney Astrocephale Ohelig Dinh Bao Dang tiuub Harold Budiman Jojo Marcus Georgi samos667 0xsysr3ll Dan Eyal Benaroche Dani Auston Pramodh Barboza Thomas Steinbach Steve-Brule Tom Andreas Brett FO Roman Krasilnikov tomaszduda23 Louison SARLIN--MAGNUS AlexViridi Xabi Caio Silva jess Ikko Eltociear Ashimine Frederic Hemberger Georg Lauterbach contrun Dylan Drost shamoon Biel Frontera Karlos Lorenz Schmid Helvio Pedreschi otbutz Kieran Konstantin Andreas Brenk EDIflyer Will Scargill Jerry Garrett Webb Hugo Stanislas Constantin Kraft Philipp matvey00z Jacob Gee-Clarke Jonas Lewin Austin Alvarado Chris D electrofloat Krasimir Nedelchev James Hillyerd tetricky Trung Le Gelven Nico A. Stadler StephenRoille Lenard Hess Aamir Azad Hobbabobba NunoHiggs Marco Emilio "sphakka" Poleggi felixilgatto Edward Betts owine Erik Bob Du Kitof Alex</article> </details> </section>   </div> </div> <section class=

Frequently asked questions

Is authelia free to use?

authelia is open source under the Apache-2.0 licence. There is no licence fee and no seat count — you can self-host it or, where the project offers one, pay a vendor for a managed version instead.

What does authelia do?

The Single Sign-On Multi-Factor portal for web apps. OpenID Certified™ and Post-Quantum Cryptography Ready.

What is authelia written in?

authelia is primarily written in Go. Its source is publicly available at https://github.com/authelia/authelia, and it has 29,482 GitHub stars.